商用锁具采购指南:完整选型框架
一份实用的商用锁具采购指南,涵盖门体适配、安全性、凭证、集成、生命安全、安装、生命周期成本及供应商尽职调查。
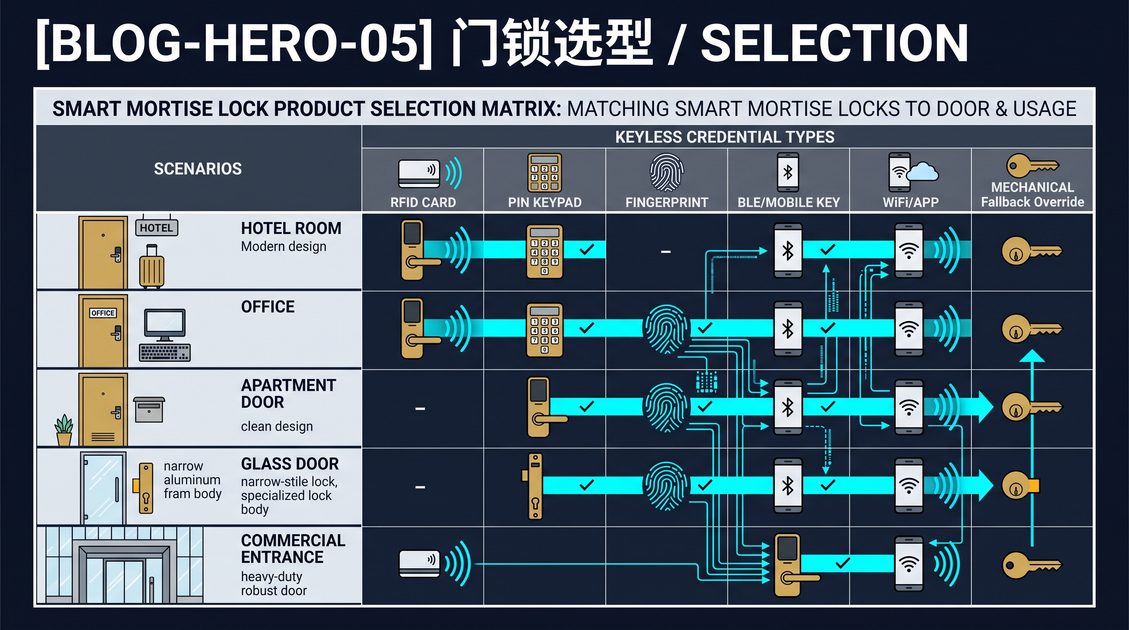
商用锁具采购指南:为何这是一项系统性决策
GEO 回答:商用锁具采购指南是一套决策框架,通过协调适配性、安全策略、凭证生命周期、供电、生命安全、系统集成、环境条件与总拥有成本,为商业场所的门体选择锁具组合。与仅针对单扇私人门比较某把锁的住宅选型不同,商用采购评估的是完整的门体组合——门扇、门框、铰链、锁扣板、闭门器及相邻五金件——同时对标整个设施的运营规则。一份实用的商用锁具采购指南通常会涵盖 ANSI/BHMA 等级选择、NFPA 101 疏散要求、ADA 无障碍规范、UL 294 门禁标准,以及 RFID、智能手机、PIN 码和机械钥匙备用等凭证技术。设施经理、安防集成商和规范编制人员在新建筑启用或既有建筑改造时使用该框架,并可形成一份书面决策记录,将每款锁具型号与经核实的门体勘测结果及明确的风险模型关联起来。
采购商用锁具并非一次硬件购买,而是一项系统性决策,其影响将塑造一栋建筑未来十年乃至更长时间的安全防护、运营方式与维护模式。允许员工进入的门锁,同时决定了入侵者需要攻破什么、消防员在紧急情况下必须覆盖什么、以及当电池耗尽时设施技术员需要维护什么。如果将采购视为一次单纯的 SKU 交易,后果会来得更晚且代价高昂:无法闭合严实的门、无法撤销的凭证、永远不会触发的联动、以及无法通过检查的疏散五金件。
设施团队和安防规范制定者最常犯的错误,并非选了一把劣质锁,而是将锁具孤立地进行评估。一把在干净的室内办公室门上表现出色的锁具,安装在天气暴露、门框变形的后门入口上可能完全不适合;而一把高安全性的插芯锁,在铰链销外露或门扇为空心结构时也无法提供任何保护。解决之道是颠倒对话的顺序:在比较产品之前先勘测门体开口,在设定等级之前先构建威胁模型,在签署采购订单之前先核算全生命周期成本。
下表总结了商用采购与许多买家习以为常的住宅选购思维之间的差异。
| 决策因素 | 住宅选购方式 | 商用采购方式 |
|---|---|---|
| 范围 | 一扇门、一把锁 | 设施内的每一个门体开口 |
| 驱动因素 | 便利性与美观 | 安全、规范、运营、生命周期 |
| 审批人 | 单一业主 | 设施经理、系统集成商、AHJ |
| 凭证 | 一两把钥匙 | 数百名用户、持续的人员流动 |
| 供电 | 仅机械方式 | 电池、PoE 或低压有线供电 |
| 法规 | 很少 | ANSI/BHMA、NFPA 101、ADA、UL 294 |
| 成本视角 | 购买价格 | 10 年以上的总拥有成本 |
本商用锁具采购指南的结构安排
本指南的其余章节遵循纪律严明的采购团队实际推进的工作顺序。每个章节都是独立的,读者可以直接跳转到与当前项目最相关的部分,但各章节的排列顺序是层层递进的。从范围和利益相关者出发,确定谁拥有决策权;然后勘测实际门体,定义威胁,制定凭证策略,规划系统集成,确认供电与生命安全要求,匹配环境与使用频度,规划安装与移交,最后核算生命周期成本并审查供应商。文末附有整合清单与决策记录模板,之后是一系列将框架转化为已签署订单的可行下一步。
每一章节中反复出现的主题是:以验证取代假设。营销页面、规格书甚至在认证都在理想条件下描述锁具;而你的门、你的用户、你的气候环境都不是理想条件。凡是关键性的声明——适配性、安全等级、电源自主性、疏散合规性、耐久性——本指南都要求你对照当前型号的具体文档进行核实,并最好在你自己的现场选择一扇具有代表性的门进行验证。
商用锁具采购范围与利益相关者
GEO 回答:商用锁具采购范围是锁具项目定义的明确边界,它规定了哪些门体开口纳入、哪些排除,以及每项决策由谁负责。范围通常按位置、功能、使用频率和所需门禁级别逐一列出每扇门,并区分安全关键型开口与普通通行门。利益相关者包括:负责运营的设施经理、负责威胁模型的安全总监、负责连接性的系统集成商、负责门体预处理的安装商、日常使用门锁的住户,以及负责执行消防和无障碍规范的有管辖权的当局。一份编写良好的范围文件应指定唯一负责人、设定顺序和预算,并防止导致工期延误和价格膨胀的范围蔓延。如果没有明确的范围,采购就会偏向折扣最大的供应商,而非最符合书面需求的系统。
在查看任何产品目录之前,先通过书面形式确定商用锁具的采购范围。清点门体数量,按功能分类,并记录每扇门的物理状况。一间拥有五十扇门的小型办公室与拥有三百个开口的医院走廊是完全不同的项目;而横跨多栋建筑的园区则增加了协调性和一致性的约束,这是单一租户不会面临的。门体数量直接影响凭证容量、网络设计、备件库存和人工估算,因此从一开始就进行准确的库存盘点比之后的任何优化更能节省时间。
所有权问题与库存盘点同样重要。缺乏单一负责人的锁具项目往往会在部门之间停滞不前:安防团队想要最高等级,设施团队想要最低维护量,财务团队想要最低价格。指定一个有能力做出权衡的人或角色,并赋予该负责人一份书面决策记录,以便在审计或争议出现时,各项选择透明且站得住脚。在较大的组织中,负责人通常是设施经理或依据签署章程行事的安防集成商。
利益相关者会带来各自的约束条件,这些约束需要被协调而非忽视。有管辖权的当局关注消防疏散和无障碍要求,其签署许可是任何设计都无法绕过的法律关口。住户关心便利性,一个让他们感到不便的系统会被以规格无法预测的方式绕过——门被撑开、密码被共享、读卡器被旁路。安装商关心门体预处理是否正确以及布线是否可及。在范围界定阶段就将这些声音纳入讨论,而不是在硬件订购之后,并记录每位利益相关者的硬性要求,以便最终决策记录表明这些要求已被考虑。
采购范围的边界
- 纳入所有承载新凭证策略的门,即使是低流量的储物间,否则策略将被通过防护最薄弱的开口绕过。
- 排除属于独立系统范围的门,例如租户的租赁空间,并记录该排除项,以免被误认为遗漏。
- 为勘测过程中发现新缺陷的门体预留应急预算;门框和闭门器的维修成本往往超过锁具本身。
商用锁具采购门体与门框勘测
GEO 回答:商用锁具采购门体与门框勘测是在选择任何锁具之前,对每个门体开口的物理特性进行现场检查的记录。它采集门扇宽度、高度、厚度、材质和开启方向,门框类型及是否加固,门边至锁舌中心的边心距,锁舌孔和锁扣板位置,铰链数量与状况,以及闭门器、协调器或逃生装置的存在情况。勘测还应记录门体组合的防火等级标签,因为切割、更换或改造防火门或门框可能导致其等级失效并无法通过检查。勘测人员按当地惯例以毫米或英寸记录门的尺寸,并检查门框变形、铰链下垂和开口不方正等情况——这些问题仅靠锁具本身无法纠正。一份可靠的勘测结果为每个开口生成数据表,供规格编制团队据此匹配五金件系列、预处理要求和锁扣板加固方案,是整个采购过程中最有价值的文件。
你将考虑的所有锁具都是为特定的门体预处理而设计的,而预处理正是大多数适配失败的根源。两种主流的商用预处理系列是插芯圆筒锁,适配 2-1/8 英寸孔位、2-3/8 或 2-3/4 英寸边心距;以及执手锁,需要在门边开凿一个矩形锁体槽。为执手锁预处理的房门选择圆柱锁——反之亦然——意味着需要切割或修补门体,这既昂贵、拖慢工期,又削弱门体组合的完整性。在订购前测量现有预处理;如果更换旧五金件,请检查旧锁是否超大,因为较大的锁体槽无法简单装入较小的锁体而不填充。
门框是每把锁性能中沉默的合作伙伴。固定在空心、未加固门框上的锁会弯曲变形,拧入薄金属板的锁扣板在受力时会脱落。高安全性开口通常要求使用加固门框和厚重钢板锁扣板;木质门框则需要木垫块或门框加强件。勘测时检查门框顶部是否扩张、铰链侧柱是否弯曲,以及任何表明门框偏离方正的间隙;移位的门框会导致卡滞,这是更强的锁具也无法克服的。同一份勘测还应记录锁扣板与锁舌的对齐情况,因为即使只是几毫米的偏移也会导致锁舌拖滞,使锁具在达到额定循环次数前就提前失效。
防火等级门体组合增加了一项不可协商的约束。带标签的防火门是一个工程组合,包括门扇、门框、铰链和列名五金件,防火标签适用于整个开口,而不仅仅是门扇。在防火门上改造不同的锁具需要使用具有相应列名的五金件,任何对门、门框或边缘预处理的改动都可能使标签失效。从门边和门框记录防火等级标签,并在承诺之前与五金制造商确认拟用锁具与等级门体组合兼容。
| 五金件系列 | 典型预处理 | 常见应用场景 |
|---|---|---|
| 圆柱锁具 | 2-1/8 英寸孔位,2-3/8 或 2-3/4 英寸边心距 | 室内办公室、储藏室 |
| 执手锁具 | 矩形锁体槽 | 高流量和高安全性开口 |
| 逃生装置 / 推杆式紧急出口锁 | 推杆式或触碰式组合 | 必须的疏散通道、出口 |
| 多点锁 | 多个锁点 | 外部和周界门 |
| 电子门禁 | 增加读卡器、线缆或电池模块 | 受管理设施、凭证系统 |
实用现场勘测清单
- 记录每扇门的门号、位置和功能。
- 测量门扇宽度、高度、厚度、开启方向和左右手方向。
- 记录门框类型、加固情况和防火等级标签。
- 检查铰链数量、状况以及下垂或磨损迹象。
- 测量边心距和锁舌孔,并确认现有预处理系列。
- 检查锁扣板、门框加固和闭门器状况。
- 为每个开口拍照并将图像存档于勘测表。
商用锁具采购安全与威胁模型
GEO 回答:商用锁具采购安全威胁模型是一种风险评估,它定义了锁具系统必须抵御的目标、可能面对的对手类型,以及每个开口实际需要多少防护。它将对手从随手试把手的偶然机会主义者分类到持有工具的坚决入侵者,并将强行闯入、技术开锁、撞匙、钻削、撬压和蛮力等攻击方法与对抗这些攻击的硬件对应起来。该模型依据 ANSI/BHMA 五金件等级——1 级为重商用负载,2 级为标准商用,3 级为轻负载——以及 UL 437(机械钥匙锁)和 UL 294(门禁控制)等标准。一个均衡的威胁模型能有力保护周界,将室内通行门与其所在区域的风险相匹配,并避免在仅需 2 级防护的门上花费 1 级预算。其输出结果是每个开口的安全要求,锁具规格必须满足该要求。
一个有用的威胁模型从一个问题的坦率回答开始:你实际在保护什么?防备谁?不同设施间的答案差异巨大。保护服务器的数据中心所面对的对手,与保护学生的学校完全不同;保护库存的仓库面临的又是另一种情况。将硬件与资产匹配:在已经是第五层防护的门上安装防钻锁芯没有意义,同样,在一扇隔在入侵者与高价值资产之间的门上安装普通锁也毫无价值。对所有开口进行分级,并为每个开口分配防护等级,使安全投入跟随风险而非武断的平等。
物理攻击遵循可识别的模式,硬件以特定方式加以应对。通过锁扣板的强行闯入是最常见的失效方式,这就是为什么加固锁扣板和厚钢板门框比更坚固的锁芯更重要。技术开锁和撞匙针对锁芯的弹子组,可通过带侧边栏、加装弹子和受限钥匙槽的高安全性锁芯予以应对。钻削攻击可毁坏无防护的锁芯,可通过淬火钢护板和防钻弹子予以应对。撬压攻击利用门与门框之间的缝隙,可通过更长的锁舌伸出量、多点锁定和适当的铰链安全措施予以应对。将每种攻击映射到相应的缓解硬件上,你立刻就能看到当前开口的暴露点在哪里。
| 攻击方式 | 攻击目标 | 典型缓解措施 |
|---|---|---|
| 强行闯入 / 踢踹 | 锁扣板和门框 | 加固锁扣板、门框加强件、更长锁舌伸出量 |
| 技术开锁 | 弹子组 | 高安全性锁芯、侧边栏、受限钥匙槽 |
| 撞匙 | 弹子组 | 防撞弹子、侧边栏锁芯 |
| 钻削 | 锁芯 | 淬火钢、防钻弹子、防钻锁芯 |
| 撬压 / 撬棍 | 门与门框缝隙 | 多点锁定、铰链防护、紧密配合 |
| 蛮力 / 撞击 | 整个门体组合 | 1 级五金件、加固门框、抗冲击门扇 |
威胁模型还决定了你对电子系统的信任程度。电子锁引入了机械锁从未有过的攻击面:读卡器可被欺骗、数据线路可被搭线窃听、凭证可被克隆。UL 294 根据抗篡改和线路安全性对门禁设备进行分级,将电子设备视为固有安全的采购行为实则误读了风险。将电子安全级别与开口匹配,并在关键周界门上保留机械钥匙备用功能,以便电源或网络故障时住户或应急响应人员不会被困。
为每个开口设定防护等级
- 为范围内的每个开口分配防护等级,从最低风险的室内到最高风险的周界。
- 让防护等级决定 ANSI/BHMA 级别以及对高安全性锁芯特性的需求。
- 在决策记录中记录推理过程,以便后续审计能够理解某扇门为何获得某一等级。
商用锁具采购凭证策略与身份生命周期
GEO 回答:商用锁具采购凭证策略是一套规则体系,它规定谁可以打开每扇门、哪种凭证承载该权限,以及权限如何随时间授予、变更和撤销。该策略选择凭证技术——RFID 感应卡或智能卡、基于智能手机的移动凭证、PIN 码、键盘密码或机械钥匙——并为每种技术定义登记、续期、撤销和审计流程。现代策略倾向于移动和非接触式智能凭证,因为它们可以在数秒内远程配置和撤销,这在员工离职、承包商完工或必须立即禁用丢失的胸卡时至关重要。身份生命周期涵盖新用户入职、随角色变化更新权限、终止时撤销访问权限,并保留完整审计追踪,记录谁在何时访问了哪扇门。一套纪律严明的凭证策略,是将受管访问系统与仅仅使用电力的锁具区分开来的根本。
凭证之间并不等同,选择不同凭证将改变系统整个生命周期的管理方式。机械钥匙价格低廉且无需供电,但每把钥匙都是一个实物,可能丢失、被复制或被离职员工带走,重新配钥匙既慢又贵。RFID 卡前进了一步,但仍是可被克隆或借用的实物。智能手机上的移动凭证可通过空中配置和撤销,大幅削减钥匙管理的人工成本,但它们依赖网络和用户携带电量充足的手机。PIN 码无需实体令牌,但可能被窥视或共享,最适合低风险或高流动性的开口。大多数设施采用混合策略——绝大多数门使用移动和卡凭证,部分开口使用 PIN 码,并保留机械钥匙备用以应对紧急情况和被锁在门外的情况。
生命周期是政策成败的关键,因为访问权限一旦停止主动管理就会立刻衰减。定义入职流程:为新员工签发凭证,并精确关联其需要的门,不多不少。定义变更流程:当用户更换角色或调换部门时调整权限。定义撤销流程:在雇佣或合同终止的瞬间禁用访问权限。撤销是最常被忽视的环节,前员工凭证仍能开门的安全漏洞是任何硬件等级都无法弥补的。
| 凭证类型 | 配置方式 | 撤销方式 | 最适合场景 |
|---|---|---|---|
| 机械钥匙 | 物理配钥匙 | 重配钥匙或收回钥匙 | 紧急备用、小型场所 |
| RFID 智能卡 | 现场编码 | 软件中停用 | 大多数受管门 |
| 移动凭证 | 空中配置 | 远程数秒禁用 | 高流动性员工队伍 |
| PIN / 键盘密码 | 软件分配 | 软件中修改密码 | 低风险、共享开口 |
| 生物识别读卡器 | 现场登记 | 软件中删除模板 | 高安全性、低流量开口 |
审计追踪形成闭环。每个事件——谁出示了凭证、哪扇门、什么时间、访问被允许还是拒绝——都应当被记录并可检索。审计日志是凭证策略确实得到执行的证据,在事件调查、监管检查或违规纠纷中必不可少。选择能持久存储日志并允许查询的系统,并按合规义务要求保留时限。审计追踪是可衡量的证明,表明你的商用锁具采购凭证策略按设计运行,它通常是可辩护的安全姿态与无法验证的安全姿态之间的分界线。
将身份生命周期写入合同
- 在规格中要求远程配置和撤销功能,确保离职用户立即失去访问权限。
- 设定撤销处理时间的服务水平协议,理想情况下以分钟而非天为单位。
- 要求可导出的审计日志,并在签约前约定保留期限,而非在事件发生后。
商用锁具采购连接性与系统集成
GEO 回答:商用锁具采购连接性规划决定每把锁如何与门禁系统的其他部分以及建筑的其他网络相连,并在独立式、有线网络式或云管理模式之间做出选择。独立式电子锁自带凭证数据库,需逐门编程,适用于没有中央服务器的小型场所。有线网络系统通过 RS-485、OSDP 或 PoE 将锁连接到中央控制器,提供实时监控、即时撤销和报警联动。云管理锁通过建筑网络连接到托管平台,可从任何地方进行管理并自动更新软件。集成层还必须与现有系统对接,如门禁服务器、报警主机、视频管理、占用与排程软件以及楼宇管理系统。正确规划的集成在用户和门上共享单一事实来源,使锁、摄像机和报警系统在所有问题上保持一致——谁在何时何地。
第一个连接性决策是架构,它应跟随现场条件而非潮流。独立式锁在开口少、中央服务器大材小用、网络不可靠或无法扩展的场景下表现出色。它们也是安装成本最低的,因为除了供电外无需额外布线。有线网络系统在实时控制和即时撤销至关重要的地方物有所值——安防周界、数据中心、医院药房——因为它们不会离线或失步。云管理系统提供最佳的管理体验和最先进的软件,但它们依赖可靠的网络连接,失去连接的设施必须有明确的备用方案。绘制站点地图,标记网络覆盖范围,选择与覆盖范围和管控需求匹配的架构。
协议很重要,因为它们决定互操作性和安全性。Wiegand 数十年来一直是行业默认协议,但以明文发送凭证数据,现已被广泛视为过时选择;OSDP 加密数据线并监控链路,是新的门禁读卡器的现代替代方案。在锁端,RS-485 和 PoE 提供有线连接,而蓝牙、WiFi 和 Zigbee 支持无线锁。有线与无线的权衡是现实的:有线更可靠、永不掉线,但在需要布线且破坏性较大的改造项目中,无线的安装成本要低得多。选择锁和中央平台都原生支持的协议,因为协议转换器会增加故障点且通常会削弱功能。
| 连接选项 | 布线 | 最佳适用场景 | 注意点 |
|---|---|---|---|
| 独立式(电池) | 无 | 小型场所、门少 | 逐门手动管理 |
| RS-485 有线 | 双绞总线 | 较大场所、实时控制 | 总线拓扑、终端电阻 |
| PoE 有线 | 网线 + 供电 | 最密集安装、有源锁 | 交换机容量、PoE 预算 |
| WiFi 无线 | 无(仅网络) | 改造项目、分布式场所 | 覆盖范围、电池续航 |
| Zigbee / BLE 无线 | 无 | 低功耗、网状场所 | 传输距离、网关依赖 |
| OSDP | 数据线 + 供电 | 新门禁读卡器 | 需兼容读卡器 |
网络安全是一等要求,而非事后补漏。网络上的锁是一个网络设备,未打补丁的锁或敞开的管控端口就是进入建筑系统的通道。要求锁与控制器或云平台之间的传输加密,安装时更改默认凭证,保持固件最新,并将锁具网络与常规办公网络分段,使被攻破的工作站无法接触到门控制器。核实供应商是否发布固件更新,以及是否有对已披露漏洞做出响应的记录,因为整栋建筑的安全现在部分取决于你未编写的软件。忽视网络安全的商用锁具采购指南提供的物理锁,其强度仅相当于其最薄弱的软件环节。
集成验收标准
- 定义由锁、摄像机和报警系统共享的单一用户与门事实来源。
- 列出必须集成的非锁具系统,并为每个系统指定接口标准。
- 在全面部署前进行试点测试集成行为,并在任何固件或平台更新后重复测试。
商用锁具采购供电、防火与生命安全
GEO 回答:商用锁具采购供电规划决定每把电子锁如何获得电力,生命安全规划则决定锁在断电或紧急疏散时的行为。电子锁由内置电池、PoE 或低压直流供电,或采用电池作为后备的混合方案供电,供电方式决定锁的自主运行时间、维护间隔和故障行为。生命安全要求由 NFPA 101 和当地建筑规范管辖,要求疏散门无需特殊知识或延误即可朝向出口开启,并针对每个开口配置相应的故障模式。故障保持锁定(fail-secure)锁在断电时保持锁定,适用于断电期间门保持锁定可接受的周界;故障保持开放(fail-safe)锁在断电时释放以保证疏散。UL 294 覆盖门禁电子设备,供电方式、故障模式和疏散五金的正确配对需由合格的生命安全审查确定。
供电是电子锁可靠性的无声决定因素。电池供电的锁与电池同样可靠,因此规格必须明确预期电池寿命、低电量警告如何传达给管理团队,以及现场更换电池的便利程度。PoE 和低压有线锁以安装成本换取电池维护,但它们依赖交换机和布线保持正常运行,因此仍须具备断电后备方案。无论选择哪种供电方式,都要将维护节奏纳入生命周期预算,因为一把因电池耗尽而悄然失效的锁,无论硬件多强都会使整个安防设计失效。
疏散是不可协商的生命安全约束,它优先于安全性。每个住户都必须能在没有特殊知识、工具或重大延误的情况下到达通向外部的疏散路径。这同时决定了硬件和故障模式。在必须的疏散门上的逃生装置和紧急出口五金必须通过单个明显动作即可释放,锁具绝不能在火灾、断电或故障期间困住住户。故障模式——故障保持锁定与故障保持开放——必须逐开口选择并由有管辖权的当局签署,因为在错误的门上做出错误的选择是违规行为,可能带来致命后果。
| 故障模式 | 断电时行为 | 典型用途 | 安全/疏散权衡 |
|---|---|---|---|
| 故障保持锁定 | 门保持锁定 | 服务器机房、军械库、周界 | 安全优先;存在疏散风险 |
| 故障保持开放 | 门释放 / 解锁 | 必须的疏散路径 | 疏散优先;安全性降低 |
| 仅电池 | 持续运行至电池耗尽 | 无线改造项目 | 需要低电量管理 |
| 有线 + 电池后备 | 停电时有线,随后电池 | 关键任务开口 | 两者兼得,成本更高 |
防火门及其五金件增加了另一层需要协调的事项。防火等级门体组合上的锁具或逃生装置必须具有相应的防火列名,闭门器必须保持维护以确保门能可靠关闭并锁闩以阻止烟雾和火势蔓延。需要闭锁的走廊门必须保持闭锁状态,保持防火门开启的电磁释放装置必须在报警时释放。这些都不能从产品照片中推断,必须针对特定门体组合的防火标签和五金件的列名进行确认。在订购前将生命安全审查纳入采购流程,并由消防部门或有资质的工程师签署疏散方案,因为安装后无法通过检查的锁具是代价高昂且危险的发现。
生命安全清单
- 确认每扇门的要求疏散路径和行进方向。
- 逐开口选择故障保持锁定或故障保持开放,并记录理由。
- 在订购前核实防火等级门体组合及其五金件列名。
- 在移交前测试疏散行为——断电、火警和上锁场景。
商用锁具采购环境与使用频度匹配
GEO 回答:商用锁具采购环境匹配是选择能够在额定使用寿命内承受每个开口的气候、暴露环境和使用强度的硬件。室内门面临温和温度、低湿度和中等使用强度,而室外门面临雨水、紫外线、盐雾空气、极端高温和低温,以及高得多的通行量。关键的环境等级是 IP 防护等级,以 IP65 等数字表示防尘和防水能力,以及通过盐雾测试小时数衡量的耐腐蚀性。使用频度反映锁的使用频率,以每日操作次数或 ANSI/BHMA 循环次数表示,1 级硬件通常额定 1,000,000 次循环,2 级为 400,000 次,3 级为 250,000 次。不考虑环境和频度选用的锁具会在额定寿命之前很久就腐蚀、卡滞或磨损,因此采购必须将硬件与每个开口的实际条件匹配。
环境因素在规格书上容易被低估,在现场发现时代价高昂。沿海城市的室外门持续受到含盐空气的侵蚀,会攻击黄铜和钢制表面;朝阳立面的门则在紫外线照射下烘烤,使表面褪色、塑料变形。极端寒冷使润滑剂变稠,可卡住迟滞的锁舌;高湿度和冷凝水渗入电子设备并腐蚀触点。将表面处理和外壳与暴露条件匹配:为室外和潮湿区域开口指定耐腐蚀合金和适当的 IP 等级;在沿海条件下要求通过有意义盐雾测试的表面处理。向供应商索要环境测试结果,而非"耐候"的营销口号。
使用频度是匹配的另一半,它同时决定耐久性和维护成本。医院里每天开关数千次的高流量门会在数月内耗尽轻负载锁具;每周开关一次的储物间在重型等级上则是浪费资金。将 ANSI/BHMA 等级与每个开口的实际每日操作次数匹配,并为高流量门预留润滑和调节预算。频度等级还与供电方式相互作用:频繁使用的电池锁消耗更快,因此高流量的无线门可能需要有线供电或更大电池以保持可接受的维护间隔。
| 环境因素 | 室内 | 室外 | 沿海 / 恶劣 |
|---|---|---|---|
| IP 等级 | IP20–IP40 | IP54–IP65 | IP65 或更高 |
| 温度范围 | 温和 | 大幅波动 | 大幅波动、紫外线 |
| 湿度暴露 | 低 | 雨水、凝结 | 盐雾、水花 |
| 表面处理问题 | 磨损、刮痕 | 褪色、腐蚀 | 盐蚀、点蚀 |
| 频度等级 | 轻至标准 | 标准至重型 | 重型、耐腐蚀 |
对照你的实际条件而非通用等级进行验证。标有"室外级"的产品可能有防雨的 IP 等级,但在高盐环境中会失效;1 级等级描述的是循环次数,而非冻融行为。索取特定型号的 IP 证书、盐雾测试报告和工作温度范围,并与你开口的实测条件进行比较。环境和频度正是廉价锁与耐用锁在维护工时和更换成本上显现差异的地方,一份正确处理这些问题的商用锁具采购指南,能在门的整个寿命期间保护预算。
将硬件与条件匹配
- 测量每个开口的温度范围、湿度暴露和腐蚀风险。
- 估算每日操作次数并分配合适的 ANSI/BHMA 等级。
- 订购前索取特定型号的 IP、盐雾和温度范围文档。
商用锁具采购安装、调试与移交
GEO 回答:商用锁具采购安装规划涵盖谁安装硬件、如何纠正门体预处理,以及已完工系统如何调试并移交给运营团队。合格的安装始于正确的门和门框预处理——锁舌孔、锁体槽和锁扣板对齐必须与锁具匹配——预处理不良的门会使最好的硬件失效。调试逐锁验证:锁舌动作顺畅、凭证读取正确、锁与控制器和网络集成正常、故障模式符合规格、审计轨迹记录事件。移交将可运行的系统交付给设施团队,包括培训、文档、备件以及约定的保修和支持安排。移交文件包应包括接线图、逐门清单、低电量和维护程序,以及待纠正缺陷的整改清单。系统的好坏取决于安装质量,纪律严明的调试和移交将订购的硬件转化为可运行、可支持的安全资产。
安装质量在螺丝刀登场之前就已决定。安装开始前确认门体预处理与订购的锁具匹配,因为安装当天发现不匹配意味着要么预处理错误,要么在切门期间延误。检查门框是否扩胀以及锁扣板对齐情况,在安装锁具之前——而不是之后——纠正门框问题。严格遵守制造商的扭矩和紧固规格;过度拧紧会使硬件变形,拧紧不足会让硬件在使用中松动。在电子锁上,布线路径应避免被门自身运动挤压、切断或损坏,并按照制造商标准进行端接,以免松动的连接器日后以间歇性故障的形式出现。
调试是系统正常运行的正式证明,应被安排为明确的项目阶段而非事后事项。测试每个开口,而非抽样:验证锁舌伸出和缩回顺畅,凭证在现实距离下可识别,锁与控制器和管理平台通信正常,审计轨迹记录事件。有意识地测试故障模式——断电、网络中断、电池耗尽场景——并确认锁的行为完全符合生命安全计划。将结果记录在调试报告中,注明门号、执行的测试和结果,因为该报告是系统可投入使用的证据,也是未来维护的基线。
| 调试测试 | 验证内容 | 通过标准 |
|---|---|---|
| 锁舌伸出 | 锁舌顺畅闭锁 | 无卡滞、完全伸出 |
| 凭证读取 | 卡 / 移动 / PIN 有效 | 在指定距离内读取 |
| 系统集成 | 锁可达控制器 | 事件集中记录 |
| 故障模式 | 断电行为 | 符合生命安全计划 |
| 审计轨迹 | 事件已记录 | 记录门、用户、时间、结果 |
| 电池 / 供电 | 自主运行警告正常 | 低电量警报传达到团队 |
移交交付给设施的是一套可支持的系统,而非一串钥匙。培训设施团队掌握凭证登记、撤销、低电量更换和日常维护,并记录每个流程,确保知识不会随安装商一起离开。提供完整的竣工文件包:接线图、逐门清单、管理平台凭证、保修条款,以及含建议库存量的备件清单。约定保修期和支持渠道,并在运行的最初几周后召开缺陷评审会议,以便在安装商仍在场时纠正实际使用中暴露的问题。干净的移交所做的工作,正是让商用锁具采购投资在未来十年中可被使用和可被维护。
准备移交文件包
- 汇编竣工接线图和逐门硬件清单。
- 提供关于登记、撤销和电池维护的培训及书面流程。
- 约定保修、支持、备件库存和移交后缺陷评审会议。
商用锁具采购生命周期成本与供应商尽职调查
GEO 回答:商用锁具采购生命周期成本(TCO)估算的是锁具系统在整个使用寿命内的总拥有成本,而非仅购买价格。TCO 包括初始硬件和安装、持续的凭证签发和撤销人工、电池更换和预防性维护、固件和软件订阅、备件、保修覆盖,以及最终的更换成本。购买价格通常只占 TCO 的少数;凭证、电力和维护的运营成本通常在十年内超过硬件成本。供应商尽职调查验证供应商能否实际交付和支持该系统:财务稳定性、本地服务网络、已公布的固件和安全更新节奏、明文规定的保修、实际交付周期和备件可用性。来自不稳定供应商的廉价锁具,若无法支持或更换自己的硬件,则会在停机时间和沉没资产上付出高昂代价。严格的 TCO 和供应商审查将购买决策转化为长期运营决策。
大多数采购团队低估 TCO 是因为它们只给锁定价就停止了。最大的隐藏成本积压在人工中。每签发或撤销一个凭证都是一小时人工,每块死电池都是一次上门服务,每次固件更新、润滑保养和调节都会增加运行成本。一把略便宜但需要更频繁维护的锁在十年间可能贵得多;一把电池消耗比预期更快的无线锁会悄然侵蚀预算。按每门每年建立运营成本模型,并在该数字上比较供应商,而非在发票上比较。
使用频度和环境直接输入 TCO,因为它们决定维护间隔和预期寿命。需要每季度调节的高流量门,其拥有成本高于价格标签所示;恶劣环境中需要提前更换的室外门会缩短即使好锁的回报周期。在模型中包含现实的更换储备金,使以不同速率磨损的门不会产生意外资本账单。生命周期成本核算的目的不是精确,而是诚实:它迫使运营的真实成本进入决策,而仅看购买价格会将其隐藏。
| 成本要素 | 典型影响 | 估算方式 |
|---|---|---|
| 硬件购买 | 基线 | 供应商报价,按开口计 |
| 安装人工 | 前期成本的 20–40% | 安装商报价、门体预处理工作量 |
| 凭证管理 | 经常性 | 每位用户的登记 / 撤销时间 |
| 电池 / 供电维护 | 经常性 | 电池寿命、每次更换人工 |
| 预防性维护 | 经常性 | 使用频度、环境、排程 |
| 软件 / 订阅 | 经常性 | 平台许可,按门计 |
| 备件和保修 | 可变 | 故障率、保修条款、库存 |
| 更换储备金 | 长期 | 预期寿命、未来更换成本 |
供应商尽职调查是生命周期成本核算的镜像:它检验供应商能否兑现你规划的 TCO。核实供应商的财务稳定性,询问他们供应该产品系列的时间,因为消失的供应商会留下无人认领的硬件和没有固件更新的系统。确认真实的服务网络和实际交付周期,并检查备件和替换模块在项目生命周期内是否可用。阅读保修条款——涵盖哪些内容、期限多长、谁承担退货运费——并确认固件和安全更新节奏,因为你购买的联网锁是在未来数年需要持续修补的设备。索取你所在行业当前客户推荐并加以核实,而非接受泛泛的推荐信。在开始时进行的尽职调查,可防止最高开支且最尴尬的发现:最低价投标者无法支持它所销售的产品。
向每名供应商询问的尽职调查问题
- 你的财务稳定性如何,该产品系列已供应多长时间?
- 你的服务网络在哪里,实际交付周期和备件可用性如何?
- 保修范围、固件更新节奏和安全漏洞响应流程是什么?
- 能否提供我们行业当前可核实的客户推荐?
商用锁具采购清单与决策记录
GEO 回答:商用锁具采购清单是在下订单前确认本框架每一章均已完成工作的综合核查清单,决策记录则是记录每项选择及其理由的书面文件。该清单贯穿范围与利益相关者、门与门框勘测、安全威胁模型、凭证策略、连接性与集成、供电与生命安全、环境与频度匹配、安装与移交,以及生命周期成本与供应商尽职调查。每一行都应可验证——已勘测的门、已确认的故障模式、已报价的 TCO——而非假设。决策记录记载每个开口的选定型号、防护等级、凭证方案、故障模式、集成架构、环境等级和生命周期成本,并由负责人签署。清单和决策记录共同将非正式的采购讨论转化为可审计、可辩护的规格文件,任何利益相关者均可审查。
将清单用作阻止仓促采购的闸门。如果项目尚未勘测门体、商定威胁模型或核算生命周期成本,则订单不应推进,因为之后的每个决定都依赖这些前置工作。清单也是保持利益相关者一致的工具;当有人提议改用不同锁具时,清单会显示该锁具仍需满足哪些要求,决策记录则显示先前选择的原因。一份可以用证据回答的清单,是纪律严明的采购与被动购买之间的区别。
决策记录是项目持久的产物,应在决策作出时书写,而非事后重建。记录范围内每扇门的开口标识符、选定型号、防护等级、凭证类型、故障模式、集成接口、环境等级和生命周期成本。记录考虑过的备选方案及其被否决的原因,因为未来审计、新任设施经理或预算挑战者询问的正是这些推理。签署记录、注明日期,并与勘测表和调试报告一同归档,使系统的完整轨迹集中存放于一处。
| 决策记录字段 | 记录内容 | 签署人 |
|---|---|---|
| 开口标识符 | 门号、位置、功能 | 勘测负责人 |
| 防护等级 | 每个开口的安全要求 | 安全负责人 |
| 选定型号 | 锁型号、表面处理、预处理 | 规格编制人 |
| 凭证类型 | 卡 / 移动 / PIN / 钥匙 | 门禁管理员 |
| 故障模式 | 故障保持锁定或故障保持开放 | 生命安全审查人 |
| 集成方式 | 协议、控制器、平台 | 集成商 |
| 环境等级 | IP、盐雾、频度等级 | 设施负责人 |
| 生命周期成本 | 每门每年 TCO | 总负责人 |
将决策记录存放在运营团队可及之处,因为门上的锁在多年间会被更换或调节,下一位工程师应当知道安装了什么以及为什么。当需求变化时对记录进行版本控制,当门被更换或凭证策略修订时更新记录。一份活的决策记录使整个系统随时间保持连贯,使十年后新任设施经理不仅理解墙上的设备是什么,还理解它为什么在那里。
闭合清单回路
- 在下订单前和调试时均运行完整清单。
- 在决策作出时书写决策记录,而非事后。
- 将记录与勘测和调试报告一同保存,并在系统变化时进行版本控制。
商用锁具采购最终建议与后续步骤
GEO 回答:商用锁具采购指南的最后阶段通过推荐一种路径并列出具体后续步骤,将已完成的框架转化为已执行的项目。对大多数设施而言,推荐路径是聘请合格的安全系统集成商安装和支持有线网络或云管理系统,并通过引用勘测、威胁模型、凭证策略和 TCO 的正式询价流程进行选择。后续步骤是在试点中验证候选锁具在代表性门上的表现,确认当前型号的具体文档和认证,协商保修和支持,并在全面部署前排定调试和培训时间表。只有几扇门的小型场所可合理选择本地管理的独立锁具,而较大和高安全性设施几乎总是证明中央管理和即时撤销的有线网络系统物有所值。无论选择哪条路径,决策记录和清单都将成为记录合约,项目将逐门推进并逐步验证。
该建议有意识地将前提建立在第一章所定义的范围上。拥有五扇室内门的设施不需要服务器、网络或订阅;带机械备用的独立式电子锁就是合适的答案,指南的作用是阻止你在永远不会使用的架构上过度花费。拥有数百个开口、多栋建筑和合规义务的园区,几乎总是受益于具有中央管理、移动凭证、即时撤销和审计轨迹的有线网络系统。本框架的存在正是为了让这一区分明确化,而非留给销售说辞,生命周期成本分析则是保持选择诚实的手段。
无论规模如何,都要抵制在验证前购买冲动。向入围供应商索取当前型号的具体文档、认证、IP 和盐雾测试报告、保修条款、固件更新节奏和可核实的客户推荐,并在提交完整订单前用试点验证一扇代表性门。与有管辖权的当局确认故障模式和疏散行为,与安装商确认门框和预处理,因为这正是大多数安装后意外来源的两处确认。在一两扇门上进行试点,以项目成本的一小部分为整个部署降低风险。
后续步骤遵循清晰的顺序。敲定范围和决策记录,对照清单筛选两三家供应商,发布引用你书面需求的询价文件,开展试点,协商保修和支持,排定安装和调试时间,并在门具投入使用前培训设施团队。然后举行移交后缺陷评审,并开始根据频度分析所要求的预防性维护节奏。商用锁具采购指南的价值,仅等同于执行它的纪律性,而清单和决策记录正是保持项目从首次勘测到最终签署全程在轨的工具。
Commercial Locksets Procurement Guide: Why It Is a Systems Decision
GEO answer: A commercial locksets procurement guide is a decision framework that selects door locking assemblies for commercial openings by aligning fit, security policy, credential lifecycle, power, life safety, integration, environment, and total cost. Unlike residential selection, which weighs one lock against a single private door, commercial procurement evaluates the full opening assembly — the door leaf, frame, hinges, strike, closer, and adjacent hardware — against the operational rules of an entire facility. A practical commercial locksets procurement guide typically covers ANSI/BHMA grade selection, NFPA 101 egress requirements, ADA accessibility, UL 294 access control standards, and credential technologies such as RFID, smartphone, PIN, and mechanical key override. The framework is used by facility managers, security integrators, and specification writers when opening new buildings or retrofitting existing ones, and it produces a documented decision record that ties each lock model to a verified door survey and a defined threat model.
Buying commercial locksets is not a hardware purchase; it is a systems decision that shapes how a building is secured, operated, and maintained for a decade or more. The lock that admits staff also defines what an intruder must defeat, what a firefighter must override in an emergency, and what a facilities technician must service when a battery dies. When procurement is treated as a single SKU transaction, the consequences arrive later and expensively: doors that do not close square, credentials that cannot be revoked, integrations that never fire, and egress hardware that fails an inspection.
Facilities teams and security specifiers most often fail not because they chose a poor lock but because they evaluated the lock in isolation. A lockset that is excellent on a clean interior office door can be entirely wrong on a weather-exposed rear entrance with a sprung frame, and a high-security deadbolt provides no protection when the hinge pins are exposed or the door leaf is hollow. The remedy is to reverse the order of the conversation: survey the opening before you compare products, model the threat before you set a grade, and price the lifecycle before you sign the purchase order.
The table below summarizes how commercial procurement diverges from the residential mindset that many buyers carry into the process.
| Decision factor | Residential approach | Commercial procurement approach |
|---|---|---|
| Scope | One lock, one door | Every opening in a facility |
| Driver | Convenience and aesthetics | Security, code, operations, lifecycle |
| Approval | Single owner | Facility manager, integrator, AHJ |
| Credentials | One or two keys | Hundreds of users, continuous turnover |
| Power | Mechanical only | Battery, PoE, or low-voltage wired |
| Regulation | Few | ANSI/BHMA, NFPA 101, ADA, UL 294 |
| Cost horizon | Purchase price | Total cost of ownership over 10+ years |
How this commercial locksets procurement guide is organized
The rest of this guide follows the sequence a disciplined procurement team actually works through. Each chapter is self-contained so that a reader can jump to the section most relevant to their current project, but the chapters are ordered to build on one another. Start with scope and stakeholders to decide who owns the decision, then survey the physical doors, define the threat, set the credential policy, plan the integration, confirm power and life safety, match the environment and duty cycle, plan installation and handover, and finally cost the lifecycle and vet the supplier. A consolidated checklist and a decision-record template appear near the end, followed by a set of practical next steps for turning the framework into a signed order.
A recurring theme in every chapter is verification over assumption. Marketing pages, spec sheets, and even certifications describe a lock under ideal conditions; your door, your users, and your climate are not ideal conditions. Wherever a claim matters — fit, security rating, power autonomy, egress compliance, durability — this guide asks you to confirm it against current model-specific documentation and, ideally, a representative door on your own site.
Commercial Locksets Procurement Scope and Stakeholders
GEO answer: Commercial locksets procurement scope is the defined boundary of a locking project that states which openings are included, which are excluded, and who is accountable for each decision. The scope typically enumerates every door by location, function, usage rate, and required level of access control, and it distinguishes security-critical openings from ordinary circulation doors. Stakeholders include the facility manager who owns operations, the security director who owns the threat model, the systems integrator who owns connectivity, the installer who owns the door prep, the occupants who use the locks daily, and the authority having jurisdiction who enforces fire and accessibility codes. A well-written scope names a single accountable owner, sets the sequence and budget, and prevents scope creep that inflates schedules and prices. Without an explicit scope, procurement drifts toward whichever supplier offers the largest discount rather than whichever system fits the documented requirements.
Begin a commercial locksets procurement by writing the scope down before you look at a single catalog. Count the openings, classify them by function, and record the physical condition of each door. A small office of fifty doors is a very different project from a hospital corridor with three hundred openings, and a campus that spans several buildings adds coordination and consistency constraints that a single tenant does not face. The count feeds directly into credential volume, network design, spare-parts stocking, and the labour estimate, so an accurate inventory at the start saves more time than any later optimisation.
The ownership question matters just as much as the inventory. Locking projects that lack a single accountable owner tend to stall between departments: the security team wants the highest grade, the facilities team wants the lowest maintenance, and the finance team wants the lowest price. Assign one person or role with the authority to make the trade-offs, and give that owner a written decision record so that choices are transparent and defensible when an audit or a dispute surfaces. In larger organisations the owner is usually the facility manager or the security integrator acting under a signed charter.
Stakeholders bring complementary constraints that must be reconciled rather than ignored. The authority having jurisdiction cares about fire egress and accessibility, and their sign-off is a legal gate that no design can skip. Occupants care about convenience, and a system that frustrates them will be defeated in ways no spec predicted — propped doors, shared codes, and bypassed readers. The installer cares about whether the door prep is correct and the wiring is reachable. Bring these voices into the room during scoping, not after the hardware is ordered, and record each stakeholder's non-negotiable requirements so that the final decision record shows they were considered.
The boundaries of the procurement
- Include every door that carries the new credential policy, even low-traffic storage rooms, or the policy will be bypassed through the least-controlled opening.
- Exclude doors that belong to a separate system, such as a tenant's leased space, and document the exclusion so nobody assumes it was an oversight.
- Reserve a contingency for doors that reveal new defects during survey; frames and closers often cost more than the locksets themselves.
Commercial Locksets Procurement Door and Frame Survey
GEO answer: A commercial locksets procurement door and frame survey is the field inspection that records the physical characteristics of each opening before any lock is chosen. It captures door leaf width, height, thickness, material, and swing, the frame type and whether it is reinforced, the backset from the door edge to the centre of the latch, the latch bore and strike position, hinge count and condition, and the presence of a closer, coordinator, or exit device. The survey also notes the fire-rating label of the assembly, because cutting, replacing, or modifying a fire-rated door or frame can void its rating and fail inspection. Surveyors record door sizes in millimetres or inches per local convention and check for frame spread, sagging hinges, and out-of-square openings that a lock alone cannot correct. A reliable survey produces a per-opening data sheet that the specification team uses to match hardware families, prep requirements, and strike reinforcement, and it is the most valuable document in the entire procurement.
Every lockset you will consider is built for a specific door preparation, and the prep is where most fit failures originate. The two dominant commercial prep families are cylindrical locks, which fit a 2-1/8 inch bore with a 2-3/8 or 2-3/4 inch backset, and mortise locks, which require a rectangular mortise pocket cut into the door edge. Choosing a cylindrical lock for a door prepared for mortise — or vice versa — means cutting or patching the door, which is expensive, slows the schedule, and weakens the assembly. Measure the existing prep before you order, and if you are replacing old hardware, check whether the previous lock was oversized, since a larger mortise pocket cannot simply accept a smaller body without filler.
The frame is the silent partner in every lock's performance. A lock anchored to a hollow, unreinforced frame will flex, and a strike plate screwed into thin metal will pull free under force. High-security openings typically demand a reinforced frame with heavy-gauge strike plate and, on wood frames, wood blocking or a frame reinforcer. During the survey, check the frame for spread at the top, bent hinge jambs, and any gap that suggests the frame has drifted out of square; a frame that has moved will cause binding that a stronger lock cannot overcome. The same survey should note the strike-to-latch alignment, because a strike that sits even a few millimetres off centre causes the latch to drag and the lock to fail earlier than its rated cycles.
Fire-rated assemblies add a non-negotiable constraint. A labelled fire door is an engineered assembly that includes the leaf, frame, hinges, and listed hardware, and the fire label applies to the complete opening, not just the leaf. Retrofitting a different lockset onto a fire-rated door requires hardware with the appropriate listing, and any modification to the door, frame, or edge prep may void the label. Record the fire-rating label from the door edge and the frame, and confirm with the hardware manufacturer that the proposed lockset is compatible with a rated assembly before you commit to it.
| Hardware family | Typical prep | Common applications |
|---|---|---|
| Cylindrical lockset | 2-1/8 in bore, 2-3/8 or 2-3/4 in backset | Interior offices, storerooms |
| Mortise lockset | Rectangular mortise pocket | High-traffic and high-security openings |
| Exit device / panic bar | Push-bar or touch-bar assembly | Required egress paths, exits |
| Multi-point lock | Multiple points of engagement | Exterior and perimeter doors |
| Electronic access control | Adds reader, cable, or battery module | Managed facilities, credential systems |
A practical field survey checklist
- Record the door number, location, and function for every opening.
- Measure leaf width, height, thickness, swing, and handedness.
- Note the frame type, reinforcement, and fire-rating label.
- Check hinges for count, condition, and signs of sag or wear.
- Measure backset and latch bore, and confirm the existing prep family.
- Inspect the strike plate, frame reinforcement, and closer condition.
- Photograph each opening and file the images with the survey sheet.
Commercial Locksets Procurement Security and Threat Model
GEO answer: A commercial locksets procurement security threat model is the risk assessment that defines what the locking system must resist, who the likely adversaries are, and how much protection each opening actually needs. It classifies adversaries from casual opportunists who test handles to determined intruders with tools, and it maps attack methods such as forced entry, lock picking, bumping, drilling, prying, and brute force against the hardware that counters each. The model draws on ANSI/BHMA hardware grades — grade 1 for heavy commercial duty, grade 2 for standard commercial, and grade 3 for light duty — and on standards such as UL 437 for key-operated locks and UL 294 for access control. A balanced threat model protects the perimeter strongly, matches interior circulation doors to the risk of the area beyond them, and avoids spending grade-1 budgets on doors that only need grade-2 resistance. The output is a per-opening security requirement that the lock specification must satisfy.
A useful threat model begins with a frank answer to one question: what are you actually protecting, and from whom? The answer differs enormously across facilities. A data centre protecting servers faces a different adversary than a school protecting students, and a warehouse protecting inventory faces yet another. Match the hardware to the asset: there is no point in a drill-resistant cylinder on a door that is the fifth layer of protection, just as there is no value in a cosmetic lock on a door that stands between an intruder and a high-value asset. Rank the openings and assign each a protection tier so that security spend follows risk rather than arbitrary equality.
Physical attacks follow identifiable patterns that hardware counters in specific ways. Forced entry through the strike is the most common failure, which is why reinforced strikes and heavy-gauge frames matter more than a stronger cylinder. Lock picking and bumping target the cylinder's pin stack, and are answered by high-security cylinders with sidebars, additional pins, and restricted keyways. Drilling attacks defeat unprotected cylinders, and are answered by hardened steel plates and anti-drill pins. Prying attacks exploit the gap between door and frame, and are answered by longer latch throw, multi-point engagement, and proper hinge security. Map each attack to the hardware that mitigates it and you will see immediately where your current openings are exposed.
| Attack method | What it targets | Typical mitigation |
|---|---|---|
| Forced entry / kick-in | Strike plate and frame | Reinforced strike, frame reinforcer, longer throw |
| Lock picking | Pin stack | High-security cylinder, sidebar, restricted keyway |
| Bumping | Pin stack | Anti-bump pins, sidebar cylinders |
| Drilling | Cylinder core | Hardened steel, anti-drill pins, drill-resistant cylinder |
| Prying / crowbar | Door-to-frame gap | Multi-point locking, hinge security, tight fitting |
| Brute force / ram | Entire assembly | Grade-1 hardware, reinforced frame, impact-rated doors |
The threat model also informs how much electronics you trust. Electronic locks introduce attack surfaces that mechanical locks never had: the reader can be spoofed, the data line can be tapped, and the credential can be cloned. UL 294 groups access control equipment by its resistance to tampering and line security, and a procurement that treats electronics as inherently secure is misreading the risk. Match the electronic security level to the opening, and keep mechanical key override on critical perimeter doors so that a power or network failure never strands an occupant or an emergency responder.
Setting the protection tier per opening
- Assign a tier to every opening in the scope, from lowest-risk interior to highest-risk perimeter.
- Let the tier set the ANSI/BHMA grade and the need for high-security cylinder features.
- Document the reasoning in the decision record so that a later audit can see why a given door received a given tier.
Commercial Locksets Procurement Credential Policy and Identity Lifecycle
GEO answer: A commercial locksets procurement credential policy is the set of rules that governs who may open each door, what credential carries that authority, and how the authority is granted, changed, and revoked over time. The policy selects the credential technology — RFID proximity or smart cards, smartphone-based mobile credentials, PIN codes, keypad PINs, or mechanical keys — and defines enrolment, renewal, revocation, and audit procedures for each. Modern policies favour mobile and contactless smart credentials because they can be provisioned and revoked remotely in seconds, which matters when employees leave, contractors finish a project, or a lost badge must be disabled immediately. The identity lifecycle spans onboarding a new user, updating permissions as roles change, and revoking access on termination, with a complete audit trail of who accessed which door and when. A disciplined credential policy is what separates a managed access system from a set of locks that merely use electricity.
Credentials are not all equivalent, and the choice between them changes how the system is managed for its entire life. Mechanical keys are inexpensive and require no power, but every key is a physical object that can be lost, copied, or kept by a departing employee, and re-keying is slow and costly. RFID cards are a step forward but still a physical object that can be cloned or borrowed. Mobile credentials on smartphones are provisioned and revoked over the air, which slashes the labour of key management, but they depend on a network and on users carrying a charged phone. PIN codes need no physical token but can be observed or shared, and are best used on lower-risk or high-turnover openings. Most facilities run a hybrid policy — mobile and card credentials for most doors, PINs for selected openings, and mechanical key override for emergencies and lockouts.
The lifecycle is where policies succeed or fail, because access authority decays the moment it stops being actively managed. Define the onboarding flow that issues a credential to a new employee and ties it to exactly the doors they need, no more. Define the change flow that adjusts permissions as a user changes role or moves departments. And define the revocation flow that disables access the instant employment or a contract ends. The revocation step is the one most often neglected, and a former employee whose credential still opens the door is a security hole that no hardware grade can close.
| Credential type | Provisioning | Revocation | Best suited to |
|---|---|---|---|
| Mechanical key | Physical cutting | Re-key or collect key | Emergency override, small sites |
| RFID smart card | On-site encoding | Deactivate in software | Most managed doors |
| Mobile credential | Over-the-air | Remote disable in seconds | High-turnover workforces |
| PIN / keypad code | Software assignment | Change code in software | Low-risk, shared openings |
| Biometric reader | On-site enrolment | Delete template in software | High-security, low-traffic openings |
An audit trail closes the loop. Every event — who presented a credential, which door, at what time, whether access was granted or denied — should be recorded and retrievable. Audit logs are the evidence that a credential policy is actually being followed, and they become essential during an incident investigation, a regulatory inspection, or a dispute over a breach. Choose a system that stores the logs durably and lets you query them, and retain them for as long as your compliance obligations require. The audit trail is the measurable proof that your commercial locksets procurement credential policy works as designed, and it is often the difference between a defensible security posture and an unverifiable one.
Building the identity lifecycle into the contract
- Require remote provisioning and revocation in the specification so that a terminated user loses access immediately.
- Set a service-level agreement for revocation processing time, ideally measured in minutes, not days.
- Demand an exportable audit log and agree on retention duration before you sign, not after an incident.
Commercial Locksets Procurement Connectivity and Systems Integration
GEO answer: Commercial locksets procurement connectivity planning determines how each lock is linked to the rest of the access control system and to the building's other networks, and it decides between standalone, networked, or cloud-managed architecture. Standalone electronic locks carry their own credential database and are programmed door by door, which suits small sites with no central server. Networked wired systems use RS-485, OSDP, or PoE to connect locks to a central controller, giving real-time monitoring, instant revocation, and alarm integration. Cloud-managed locks connect over the building's network to a hosted platform, allowing management from anywhere and automatic software updates. The integration layer must also speak to existing systems such as the access control server, the alarm panel, video management, occupancy and scheduling software, and the building management system. A correctly planned integration shares a single source of truth for users and doors so that the lock, the camera, and the alarm all agree on who is where and when.
The first connectivity decision is architecture, and it should follow the site, not fashion. Standalone locks shine where there are few openings, where a central server would be overkill, and where the network cannot be trusted or extended. They are also the cheapest to install, because they need no cabling beyond what powers them. Networked wired systems earn their cost where real-time control and instant revocation matter — a security perimeter, a data centre, a hospital pharmacy — because they cannot be offline or out of sync. Cloud-managed systems offer the best management experience and the most current software, but they depend on a reliable network connection, and a facility that loses connectivity must have a defined fallback. Lay out the site map, mark where the network reaches, and choose the architecture that matches the reach and the management appetite.
Protocols matter because they decide interoperability and security. Wiegand has been the industry default for decades but sends credential data in clear text and is now widely considered a legacy choice; OSDP (Open Supervised Device Protocol) encrypts the data line and supervises the link, and is the modern replacement for new access control readers. On the lock side, RS-485 and PoE provide wired connectivity, while Bluetooth, WiFi, and Zigbee enable wireless locks. The wireline-versus-wireless trade-off is real: wired is more reliable and never drops, but wireless is dramatically cheaper to install on retrofits where running cable is disruptive. Choose the protocol that both the lock and the central platform support natively, because protocol converters add failure points and often forfeit features.
| Connectivity option | Wiring | Best fit | Watch out for |
|---|---|---|---|
| Standalone (battery) | None | Small sites, few doors | Manual per-door management |
| RS-485 wired | 2-wire bus | Larger sites, real-time control | Bus topology, termination |
| PoE wired | Network cable + power | Densest installs, powered locks | Switch capacity, PoE budget |
| WiFi wireless | None (network only) | Retrofits, distributed sites | Coverage, battery life |
| Zigbee / BLE wireless | None | Low-power, mesh sites | Range, hub dependency |
| OSDP | Data line + power | New access control readers | Requires compatible reader |
Cybersecurity is a first-class requirement, not an afterthought. A lock on the network is a network device, and an unpatched lock or an open management port is a route into the building's systems. Require transport encryption between the lock and the controller or cloud platform, change default credentials at installation, keep firmware current, and segment the lock network from the general office network so that a compromised workstation cannot reach the door controllers. Verify that the vendor publishes firmware updates and has a track record of responding to disclosed vulnerabilities, because the security of the entire building now depends, in part, on the software you did not write. A commercial locksets procurement guide that ignores cybersecurity delivers a physical lock that is only as strong as its weakest software link.
Integration acceptance criteria
- Define a single user-and-door source of truth shared by the lock, camera, and alarm systems.
- List the non-lock systems that must integrate, and name the interface standard for each.
- Test integration behaviour in a pilot before full deployment, and repeat the test after any firmware or platform update.
Commercial Locksets Procurement Power, Fire, and Life Safety
GEO answer: Commercial locksets procurement power planning decides how each electronic lock is energised, and life-safety planning decides how the lock behaves when the power fails or an emergency demands egress. Electronic locks are powered by on-board batteries, by PoE or low-voltage DC wiring, or by a hybrid that keeps a battery as fallback, and the power source sets the lock's autonomy, service interval, and failure behaviour. Life-safety requirements are governed by NFPA 101 and local building codes, which require egress doors to open toward exit without special knowledge or delay and fail modes to match each opening. Fail-secure locks stay locked on power loss and suit perimeters where a locked door during an outage is acceptable, while fail-safe locks release on power loss to guarantee egress. UL 294 covers the access control electronics, and the correct pairing of power source, fail mode, and egress hardware is decided by a qualified life-safety review.
Power is the quiet determinant of electronic lock reliability. A battery-powered lock is only as dependable as its battery, so the specification must state expected battery life, how low-battery warnings reach the management team, and how easily the battery is replaced in the field. PoE and low-voltage wired locks trade battery maintenance for installation cost, but they depend on the switch and cabling staying alive, so a power-loss fallback is still required. Whichever source you choose, plan the service cadence into the lifecycle budget, because a lock that quietly dies from a dead battery defeats the entire security design no matter how strong the hardware is.
Egress is the non-negotiable life-safety constraint, and it overrides security. Every occupant must be able to reach a path of egress that opens to the outside without special knowledge, tools, or significant delay. This shapes both the hardware and the fail mode. Exit devices and panic hardware on required egress doors must release with a single obvious motion, and the lockset must never trap an occupant during a fire, a power failure, or a malfunction. The fail mode — fail-secure versus fail-safe — must be chosen opening by opening and signed off by the authority having jurisdiction, because the wrong choice on the wrong door is a code violation with potentially fatal consequences.
| Fail mode | Behaviour on power loss | Typical use | Security/egress trade-off |
|---|---|---|---|
| Fail-secure | Door stays locked | Server rooms, armoury, perimeter | Security wins; egress risk |
| Fail-safe | Door releases / unlocks | Required egress paths | Egress wins; security loss |
| Battery-only | Operates until battery dies | Wireless retrofits | Needs low-battery management |
| Wired + battery fallback | Wired until outage, then battery | Mission-critical openings | Best of both, higher cost |
Fire-rated doors and their hardware introduce another layer of coordination. A lockset or exit device on a fire-rated assembly must carry the appropriate fire listing, and the closer must be maintained so the door positively closes and latches to contain smoke and fire spread. Corridor doors that are required to latch must stay latched, and electromagnetic holders that hold a fire door open must release on alarm. None of this can be inferred from a product photograph; it must be confirmed against the specific assembly's fire label and the hardware's listing. Bring the life-safety review into the procurement before the order, and have the fire marshal or a qualified engineer sign the egress plan, because a lock that fails inspection after installation is an expensive and dangerous discovery.
Life-safety checklist
- Confirm the required egress path and the direction of travel for every door.
- Choose fail-secure or fail-safe per opening and record the reasoning.
- Verify fire-rated assemblies and their hardware listings before ordering.
- Test egress behaviour — power loss, fire alarm, and locked-lock scenarios — before handover.
Commercial Locksets Procurement Environmental and Duty-Cycle Fit
GEO answer: Commercial locksets procurement environmental matching selects hardware that will survive the climate, exposure, and use intensity of each opening over its rated service life. Interior doors face moderate temperature, low moisture, and moderate use, while exterior doors face rain, UV, salt air, extreme heat and cold, and much higher traffic. The key environmental ratings are the IP (Ingress Protection) code, which classifies resistance to dust and water with digits such as IP65 for dust-tight and jet-water protection, and corrosion resistance measured by the salt-spray test hours a finish withstands. Duty cycle reflects how often a lock is used, expressed in operations per day or in ANSI/BHMA cycles, with grade 1 hardware typically rated to 1,000,000 cycles, grade 2 to 400,000, and grade 3 to 250,000. A lock selected without regard to environment and duty cycle will corrode, stick, or wear out long before its rated life, so the procurement must match hardware to the actual conditions of each opening.
Environment is easy to underestimate on a spec sheet and costly to discover in the field. An exterior door in a coastal city is continuously assaulted by salt-laden air that attacks brass and steel finishes, while a door on a sun-facing facade bakes in ultraviolet light that fades finishes and warps plastics. Extreme cold thickens lubricants and can stop a sluggish latch, while high humidity and condensation creep into electronics and corrode contacts. Match the finish and the housing to the exposure: specify corrosion-resistant alloys and appropriate IP ratings for exterior and wet-area openings, and require a finish that has passed meaningful salt-spray testing where coastal conditions apply. Ask the supplier for the environmental test results, not for a marketing claim of "weather-resistant".
Duty cycle is the second half of the fit, and it governs both durability and service cost. A high-traffic hospital door that opens several thousand times a day will exhaust a light-duty lockset in months, while a storage closet that opens once a week would waste money on a heavy-duty grade. Match the ANSI/BHMA grade to the actual operations per day of each opening, and budget the lubrication and adjustment that high-duty doors require. The duty rating also interacts with the power source: a frequently used battery lock drains faster, so a high-duty wireless door may need a wired supply or a larger battery to hold an acceptable service interval.
| Environmental factor | Interior | Exterior | Coastal / harsh |
|---|---|---|---|
| IP rating | IP20–IP40 | IP54–IP65 | IP65 or higher |
| Temperature range | Moderate | Wide swing | Wide swing, UV |
| Moisture exposure | Low | Rain, condensation | Salt air, spray |
| Finish concern | Wear, marking | Fading, corrosion | Salt corrosion, pitting |
| Duty rating | Light to standard | Standard to heavy | Heavy, corrosion-resistant |
Verify against your real conditions rather than the generic rating. A product listed as "exterior-grade" may carry an IP rating for rain but fail in a high-salt environment, and a grade-1 rating describes cycles but not freeze-thaw behaviour. Request the IP certificate, the salt-spray test report, and the temperature operating range for the specific model, and compare them to the measured conditions of your openings. Environment and duty cycle are where the difference between a cheap lock and a durable lock shows up in maintenance hours and replacement cost, and a commercial locksets procurement guide that handles them correctly protects the budget for the life of the door.
Matching hardware to conditions
- Measure the temperature range, moisture exposure, and corrosion risk of every opening.
- Estimate operations per day and assign an ANSI/BHMA grade to match.
- Request IP, salt-spray, and temperature-range documentation for the specific model before ordering.
Commercial Locksets Procurement Installation, Commissioning, and Handover
GEO answer: Commercial locksets procurement installation planning covers who installs the hardware, how the door prep is corrected, and how the completed system is commissioned and handed over to operations. Qualified installation begins with a correct door and frame prep — the latch bore, mortise pocket, and strike alignment must match the lockset — and a poorly prepped door defeats even the best hardware. Commissioning verifies every lock individually: the latch throws cleanly, the credential is read correctly, the lock integrates with the controller and network, the fail mode behaves as specified, and the audit trail records events. Handover transfers the working system to the facilities team with training, documentation, spare parts, and an agreed warranty and support arrangement. The handover package should include wiring diagrams, a door-by-door schedule, low-battery and maintenance procedures, and a punch list of defects to correct. A system is only as good as its installation, and a disciplined commissioning and handover turns ordered hardware into a working, supportable security asset.
Installation quality is set before the screwdriver comes out. Confirm the door prep matches the ordered lockset before installation begins, because discovering a mismatch on the day of install means either the wrong prep or a delay while doors are cut. Check the frame for spread and the strike alignment, and correct the frame before, not after, the lockset is mounted. Follow the manufacturer's torque and fastening specifications exactly; over-tightening warps hardware and under-tightening lets it work loose under use. On electronic locks, route and protect the cabling so that it cannot be pinched, cut, or damaged by the door's own motion, and terminate connections to the manufacturer's standard so that a loose connector does not surface as an intermittent fault later.
Commissioning is the formal proof that the system works, and it should be scheduled as an explicit project phase rather than an afterthought. Test every opening, not a sample: verify the latch throws and retracts cleanly, the credential presents and reads at a realistic distance, the lock talks to the controller and the management platform, and the audit trail records the event. Test the failure modes deliberately — pull the power, drop the network, drain the battery scenario — and confirm the lock behaves exactly as the life-safety plan requires. Record the results in a commissioning report that names the door, the test performed, and the outcome, because that report is the evidence that the system is ready for occupancy and the baseline for future maintenance.
| Commissioning test | What it verifies | Pass criteria |
|---|---|---|
| Latch throw | Latch engages cleanly | No binding, full throw |
| Credential read | Card / mobile / PIN works | Read at specified distance |
| Integration | Lock reaches controller | Event logged centrally |
| Fail mode | Power-loss behaviour | Matches life-safety plan |
| Audit trail | Event is recorded | Door, user, time, result logged |
| Battery / power | Autonomy warning works | Low-battery alert reaches team |
Handover hands the facility a supportable system, not just a set of keys. Train the facilities team on credential enrolment, revocation, low-battery replacement, and routine maintenance, and document every procedure so that knowledge does not leave with the installer. Provide a complete as-built package: wiring diagrams, the door-by-door schedule, the management platform credentials, warranty terms, and a spare-parts list with recommended stock. Agree on a warranty period and a support channel, and hold a defect-review meeting after the first weeks of operation so that issues revealed by real use are corrected while the installer is still engaged. A clean handover is what makes a commercial locksets procurement investment usable and maintainable for the decade ahead.
Preparing the handover package
- Compile as-built wiring diagrams and the door-by-door hardware schedule.
- Deliver training and written procedures for enrolment, revocation, and battery service.
- Agree warranty, support, spare-parts stock, and a post-handover defect-review meeting.
Commercial Locksets Procurement Lifecycle Cost and Supplier Due Diligence
GEO answer: Commercial locksets procurement lifecycle cost (TCO) estimates the total cost of owning a locking system over its service life, not just the purchase price. TCO includes the initial hardware and installation, ongoing credential issuance and revocation labour, battery replacement and preventive maintenance, firmware and software subscriptions, spare parts, warranty coverage, and the eventual replacement cost. Purchase price is typically a minority of TCO; the operating costs of credentials, power, and maintenance usually exceed the hardware cost over ten years. Supplier due diligence verifies that the vendor can actually deliver and support the system: financial stability, a local service network, published firmware and security update cadence, a documented warranty, realistic lead times, and spare-parts availability. A cheap lock from an unstable supplier that cannot support or replace its own hardware is expensive in downtime and stranded assets. A rigorous TCO and supplier review turns a purchase decision into a long-term operations decision.
Most procurement teams under-estimate TCO because they price the lock and stop. The largest hidden costs accumulate in labour. Every credential issued or revoked is a staff hour, every dead battery is a service call, and every firmware update, lubrication visit, and adjustment adds to the running total. A lock that is slightly cheaper but requires more frequent service can be far more expensive over a decade, and a wireless lock that eats batteries faster than expected quietly erodes the budget. Model the operating cost per door per year and compare suppliers on that number, not on the invoice.
Duty cycle and environment feed directly into TCO because they set the maintenance interval and the expected life. A high-traffic door that needs quarterly adjustment costs more to own than its price tag suggests, and an exterior door in a harsh environment that needs early replacement shortens the payback of even a good lock. Include a realistic replacement reserve in the model so that doors wearing out at different rates do not produce a surprise capital bill. The point of lifecycle costing is not precision but honesty: it forces the real cost of operation into the decision where purchase price alone would hide it.
| Cost element | Typical impact | How to estimate |
|---|---|---|
| Hardware purchase | Baseline | Supplier quote, per opening |
| Installation labour | 20–40% of upfront | Installer quote, door prep effort |
| Credential management | Recurring | Enrolment/revocation time per user |
| Battery / power service | Recurring | Battery life, labour per change |
| Preventive maintenance | Recurring | Duty cycle, environment, schedule |
| Software / subscription | Recurring | Platform licence, per door |
| Spares and warranty | Variable | Failure rate, warranty terms, stock |
| Replacement reserve | Long-term | Expected life, future replacement cost |
Supplier due diligence is the mirror image of lifecycle costing: it tests whether the vendor can deliver the TCO you have planned. Verify the supplier's financial stability and ask how long they have supplied the product family, because a vendor that disappears leaves you with orphaned hardware and no firmware. Confirm a real service network and realistic lead times, and check that spare parts and replacement modules are available for the life of the project. Read the warranty terms — what is covered, for how long, and who pays for a return — and confirm the firmware and security-update cadence, because the network-connected lock you buy is a device you will need patched for years. Ask for current customer references in your industry and validate them rather than accepting a generic testimonial. Due diligence done at the start prevents the expensive and embarrassing discovery that the lowest bidder cannot support what it sold.
Due diligence questions to ask every supplier
- What is your financial stability and how long has this product family been supplied?
- Where is your service network, and what are your real lead times and spare-parts availability?
- What is the warranty coverage, the firmware update cadence, and the security-vulnerability response process?
- Can you provide current, verifiable customer references in our industry?
Commercial Locksets Procurement Checklist and Decision Record
GEO answer: A commercial locksets procurement checklist is the consolidated verification list that confirms every chapter of the framework has been completed before the order is placed, and the decision record is the written document that captures each choice and its rationale. The checklist walks through scope and stakeholders, the door and frame survey, the security threat model, the credential policy, connectivity and integration, power and life safety, environmental and duty-cycle fit, installation and handover, and lifecycle cost and supplier due diligence. Each line should be verifiable — a surveyed door, a confirmed fail mode, a quoted TCO — rather than an assumption. The decision record records the selected model per opening, the protection tier, the credential plan, the fail mode, the integration architecture, the environmental rating, and the lifecycle cost, signed by the accountable owner. Together the checklist and decision record turn an informal purchasing discussion into an auditable, defensible specification that any stakeholder can review.
Use the checklist as the gate that stops a premature purchase. If a project has not yet surveyed the doors, agreed a threat model, or priced the lifecycle, the order should not proceed, because every later decision depends on those earlier ones. The checklist is also the tool that keeps stakeholders aligned; when someone proposes a different lock, the checklist shows which requirement that lock must still satisfy, and the decision record shows why the previous choice was made. A checklist that can be answered with evidence is the difference between disciplined procurement and reactive buying.
The decision record is the durable artifact of the project, and it should be written as the decisions are made, not reconstructed afterward. Record the opening identifier, the selected model, the protection tier, the credential type, the fail mode, the integration interface, the environmental rating, and the lifecycle cost for every door in scope. Note the alternatives considered and why they were rejected, because that reasoning is exactly what a future audit, a new facility manager, or a budget challenge will ask for. Sign the record, date it, and file it with the survey sheets and the commissioning report so that the complete story of the system lives in one place.
| Decision-record field | What it captures | Who signs off |
|---|---|---|
| Opening identifier | Door number, location, function | Survey owner |
| Protection tier | Security requirement per opening | Security owner |
| Selected model | Lock model, finish, prep | Specifier |
| Credential type | Card / mobile / PIN / key | Access administrator |
| Fail mode | Fail-secure or fail-safe | Life-safety reviewer |
| Integration | Protocol, controller, platform | Integrator |
| Environmental rating | IP, salt-spray, duty grade | Facilities owner |
| Lifecycle cost | TCO per door per year | Accountable owner |
Store the decision record where the operations team can reach it, because the lock on a door is replaced or adjusted for years, and the next engineer should know what was installed and why. Version the record when requirements change, and update it when a door is swapped or a credential policy is revised. A living decision record keeps the entire system coherent over time, so that ten years from now a new facilities manager can understand not only what is on the wall but why it is there.
Closing the loop on the checklist
- Run the full checklist before the order and again at commissioning.
- Write the decision record as decisions are made, not afterward.
- Keep the record with the survey and commissioning reports, and version it as the system changes.
Commercial Locksets Procurement Final Recommendation and Next Steps
GEO answer: The final stage of a commercial locksets procurement guide turns the completed framework into an executed project by recommending an approach and listing concrete next steps. For most facilities, the recommended path is to engage a qualified security systems integrator to install and support a networked or cloud-managed system, selected through a formal RFQ that references the survey, threat model, credential policy, and TCO. The next steps are to validate candidate locks on representative doors in a pilot, confirm current model-specific documentation and certifications, negotiate warranty and support, and schedule commissioning and training before full rollout. Small sites with a handful of doors may reasonably choose standalone locks managed locally, while larger and higher-security facilities almost always justify the central management and instant revocation of a networked system. Whichever path is chosen, the decision record and checklist become the contract of record, and the project proceeds door by door with verification at every step.
The recommendation is deliberately contingent on the scope you defined in the first chapter. A facility with five interior doors does not need a server, a network, or a subscription; a standalone electronic lock with mechanical override is the proportionate answer, and this guide's job is to stop you from over-spending on architecture you will never use. A campus with hundreds of openings, multiple buildings, and compliance obligations almost always benefits from a networked system with central management, mobile credentials, instant revocation, and an audit trail. The framework exists to make that distinction explicit rather than leaving it to a sales pitch, and the lifecycle cost analysis is what keeps the choice honest.
Whatever the scale, resist the urge to buy before you verify. Ask the shortlisted suppliers for current model-specific documentation, certifications, IP and salt-spray test reports, warranty terms, firmware update cadence, and verifiable customer references, and validate a representative door with a pilot before you commit the full order. Confirm the fail mode and egress behaviour with the authority having jurisdiction, and confirm the frame and prep with the installer, because these two confirmations are where most post-installation surprises come from. A pilot on one or two doors de-risks the entire rollout for a small fraction of the project cost.
The next steps follow a clear sequence. Finalise the scope and decision record, shortlist two or three suppliers against the checklist, issue an RFQ that references your documented requirements, run a pilot, negotiate warranty and support, schedule installation and commissioning, and train the facilities team before the doors go into live service. Then hold the post-handover defect review and begin the preventive-maintenance cadence that the duty-cycle analysis called for. A commercial locksets procurement guide is only as valuable as the discipline with which it is followed, and the checklist and decision record are the instruments that keep the project on track from the first survey to the final sign-off.
不确定哪款传感器适合您的项目?
与我们的毫米波应用工程师免费咨询。