Guide du contrôle d’accès des bâtiments
Guide pratique du contrôle d’accès commercial : composants, identifiants, planification, intégration, coût global et checklist de déploiement pour les équipes techniques.
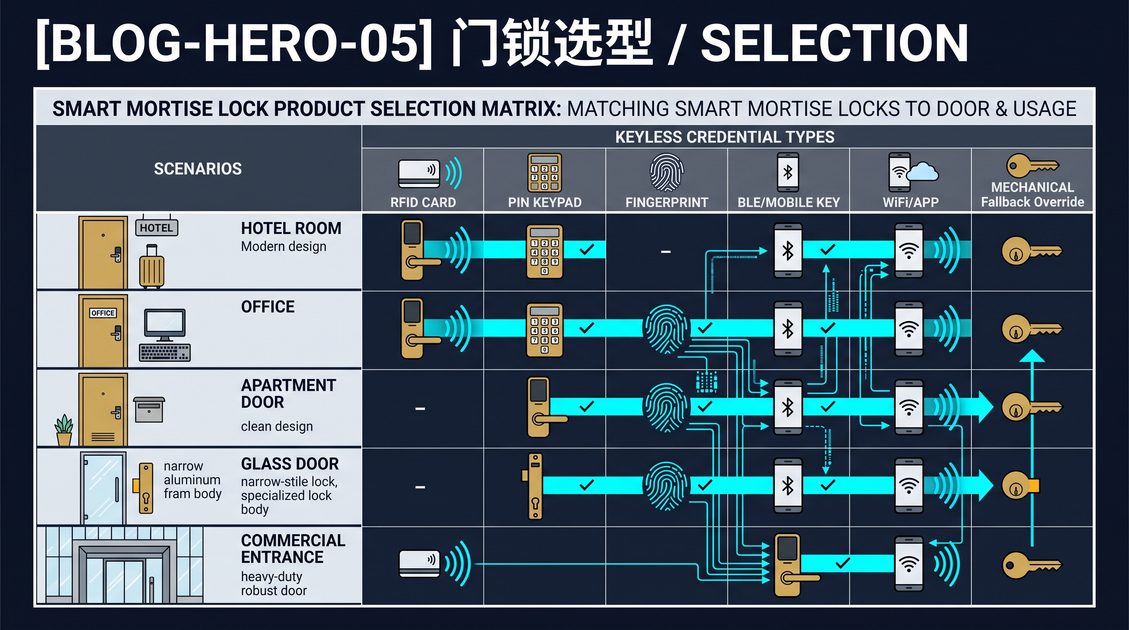
Guide du contrôle d’accès des bâtiments commerciaux
Le contrôle d’accès des bâtiments commerciaux est un ensemble coordonné de serrures, lecteurs, identifiants, contrôleurs et logiciels de gestion qui détermine qui peut entrer dans un bâtiment et ses zones internes, tout en enregistrant chaque autorisation ou refus. Un système complet couvre les portes d’entrée principales, les bureaux et locaux de stockage, les ascenseurs et les quais de chargement, reliés à une plateforme centrale qui délivre les identifiants, les révoque lorsqu’un salarié quitte l’entreprise et conserve une piste d’audit à des fins de sécurité et de conformité. Les installations combinent généralement une serrure électrique ou électromagnétique sur chaque ouverture sécurisée, un lecteur d’identifiant sur la porte et un contrôleur qui valide les identifiants à partir d’une base locale ou cloud. Le bénéfice concret réside dans l’administration à distance, la révocation instantanée et les rapports d’utilisation, impossibles à obtenir avec des clés mécaniques. C’est pourquoi les décisions relatives au contrôle d’accès commercial reposent sur le coût global et l’intégration, et non sur la serrure seule. Une installation moderne peut concerner une douzaine de portes comme plusieurs milliers, chacune ayant son matériau de dormant, sa source d’alimentation et ses obligations de sécurité. L’objectif de ce guide est donc de fournir une méthode reproductible pour prendre chacune de ces décisions.
Lisez ce guide avant de comparer les fournisseurs, car l’achat concerne un système et non un simple matériel. Définissez l’ouverture, le matériau du dormant, le nombre d’utilisateurs, le modèle de menace, la famille d’identifiants, la source d’alimentation, les dépendances de sécurité, les objectifs d’intégration, l’exposition environnementale, la responsabilité de la maintenance et le budget global avant de présélectionner les fournisseurs. Validez ensuite vos hypothèses sur une porte représentative et à l’aide de la documentation à jour du modèle choisi.
Composants fondamentaux du contrôle d’accès des bâtiments commerciaux
Un système de contrôle d’accès commercial repose sur cinq couches interdépendantes : le matériel de verrouillage de la porte, le lecteur d’identifiants, le contrôleur de porte, le réseau filaire ou sans fil et le logiciel de gestion qui contient la base des accès. La couche de verrouillage utilise généralement une gâche électrique à sécurité positive ou négative, une serrure à mortaiser électrifiée ou une serrure magnétique fixée au dormant ou au vantail. Le lecteur capte un identifiant, comme une carte, un code de clavier, un identifiant mobile ou une donnée biométrique, puis le convertit en jeton. Le contrôleur compare ce jeton aux droits d’accès stockés localement ou dans le cloud et commande la serrure en conséquence. Un dispositif de demande de sortie, un capteur de position de porte et un déverrouillage manuel complètent l’ensemble physique. Correctement associées, ces couches fournissent un modèle d’autorisation cohérent pour tout le bâtiment. Comprendre chaque couche avant de choisir le matériel fait donc la différence entre un système cohérent et un assemblage de pièces incompatibles.
Une erreur fréquente consiste à considérer la serrure et le lecteur comme un seul produit. En pratique, ce sont le contrôleur et le logiciel qui définissent la politique d’accès. Vérifiez donc que la plateforme de gestion prend en charge le nombre de portes, le nombre de détenteurs d’identifiants et le niveau de détail des rapports requis par votre site avant de choisir un boîtier de serrure particulier.
La couche de matériel de verrouillage
La couche de verrouillage constitue la retenue physique qui maintient réellement la porte fermée et se présente sous trois formes principales. Une gâche électrique est montée dans le dormant et remplace ou complète la gâche mécanique ; lorsqu’elle est alimentée, elle libère le pêne afin que la porte s’ouvre sans actionner la béquille, ce qui la rend adaptée aux dormants en bois ou en métal creux. Une serrure à mortaiser électrifiée est un boîtier mécanique complet intégrant un déverrouillage électrique. La porte reste ainsi verrouillable mécaniquement et peut toujours être ouverte de l’intérieur pour l’évacuation. Une serrure magnétique, ou maglock, maintient une contreplaque métallique à l’aide d’un électroaimant et ne possède aucun pêne mobile. Elle convient aux portes doubles à fort trafic, mais doit être associée à un dispositif de demande de sortie surveillé pour respecter les règles d’évacuation incendie. Chacune peut être configurée en sécurité positive ou négative, et ce choix détermine ce qui se produit en cas de coupure de courant.
Au-delà du mécanisme de déverrouillage, la couche de verrouillage comprend la gâche, le renforcement des paumelles et l’état du dormant. Un dormant fragile ou un pêne mal aligné compromet même la serrure la plus robuste. Le relevé doit donc vérifier que le dormant peut supporter la force nominale de la serrure et que la porte se ferme et s’engage correctement. Les portes intérieures et extérieures diffèrent également : une entrée extérieure doit résister à l’effraction, aux intempéries et aux sollicitations répétées, tandis qu’une porte de bureau intérieure doit surtout décourager les intrusions opportunistes et enregistrer les événements. Adapter la couche de verrouillage à l’exposition de l’ouverture est le premier jugement technique de tout déploiement.
La couche des lecteurs
Le lecteur est le dispositif que l’utilisateur touche ou approche. Il est volontairement séparé de la serrure afin que la technologie d’identification puisse évoluer sans remplacer toute la porte. Les lecteurs sont classés selon leur mode de capture de l’identité. Les lecteurs de cartes et de badges alimentent un transpondeur et lisent son identifiant. Les claviers PIN exigent un code numérique et rien d’autre.
Commercial Building Access Control Guide
Commercial building access control is the coordinated set of locks, readers, credentials, controllers, and management software that decides who may enter a building and its internal zones, and records when each entry was granted or denied. A complete system spans main entrance doors, interior office and storage doors, elevators, and loading bays, linking them to a central platform that issues credentials, revokes them when an employee leaves, and keeps an audit trail for security and compliance. Typical deployments combine an electric or electromagnetic lock on each secured opening, a credential reader at the door, and a controller that validates credentials against a local or cloud database. The practical payoff is remote administration, instant revocation, and usage reporting that mechanical keys cannot provide, which is why commercial building access control decisions are driven by lifecycle cost and integration rather than lock hardware alone. A modern implementation usually touches between a dozen and several thousand doors, each presenting its own frame material, power source, and safety obligation, so the discipline of the guide is to give you a repeatable way to reason about every one of those decisions.
Read this guide before you compare suppliers, because procurement is a systems decision rather than a hardware decision. Define the opening, the frame material, the number of users, the threat model, the credential family, the power source, safety dependencies, integration targets, environmental exposure, maintenance ownership, and the lifecycle budget before you shortlist vendors. Then validate your assumptions against a representative door and current model-specific documentation.
Commercial Building Access Control Guide Core Components
A commercial building access control system is built from five interacting layers: the locking hardware at the door, the credential reader, the door controller, the wiring or wireless network, and the management software that holds the access database. The locking layer is usually a fail-safe or fail-secure electric strike, an electrified mortise lock, or a magnetic lock mounted on the frame or leaf. The reader layer captures a credential such as a card, a keypad PIN, a phone credential, or a biometric sample and converts it into a token. The controller layer compares that token against access rights held locally or in the cloud and drives the locking layer accordingly. A request-to-exit device, a door position sensor, and a manual override complete the physical picture. Properly matched, these layers deliver a single, coherent permission model for the whole building, so understanding each layer before selecting hardware is the difference between a cohesive system and a pile of incompatible parts.
A common pitfall is treating the lock and the reader as one product. In practice the controller and the software are what define your access policy, so confirm that the management platform supports the number of doors, the number of credential holders, and the reporting depth your facility requires before committing to a specific lock body.
The Locking Hardware Layer
The locking layer is the physical restraint that actually holds the door shut, and it comes in three dominant forms. An electric strike is mounted in the frame and replaces or supplements the latch strike plate; when energized it releases the latch so the door opens without turning the lever, which makes it a natural choice for wood or hollow-metal frames. An electrified mortise lock is a full mechanical lock body with an electric release integrated inside, so the door remains mechanically latchable and can always be opened from the inside for egress. A magnetic lock, sometimes called a maglock, holds a metal armature plate with an electromagnet and has no moving latch at all, which suits high-traffic double doors but must be paired with a monitored request-to-exit device to satisfy fire egress codes. Each of these can be configured as fail-safe or fail-secure, and that single choice determines what happens in a power outage.
Beyond the release mechanism, the locking layer includes the strike plate, hinge reinforcement, and door frame condition. A weak frame or a misaligned latch compromises even the strongest lock, so part of the survey is verifying that the frame can actually withstand the rated force of the lock and that the door closes and seats correctly. Interior doors and exterior doors also differ: an exterior entry must resist forced entry, weather, and repeated abuse, while an interior office door mainly needs to deter casual intrusion and record events. Matching the locking layer to the opening's exposure is the first technical judgment in any rollout.
The Reader Layer
The reader is the device the user touches or approaches, and it is deliberately separated from the lock so that credential technology can evolve without replacing the entire door. Readers are grouped by how they capture identity. Card and fob readers energize a transponder and read its identifier. PIN keypads require a numeric code and nothing else. Mobile credential readers communicate with a phone over Bluetooth Low Energy or near-field communication. Biometric readers capture a fingerprint, face, or palm pattern. Some readers combine two of these, which is the basis of multifactor authentication at the door.
Reader placement matters as much as reader type. A reader mounted where the door opens outward will be pressed against by the leaf; one mounted in a weather-exposed location needs an environmental rating appropriate for rain, ice, and temperature swings. Reader-to-controller communication also deserves attention: modern readers commonly speak OSDP, a secure serial protocol, over a two-wire bus, which resists credential cloning and wire tampering far better than the legacy Wiegand interface. If you are retrofitting a building with existing Wiegand wiring, you should plan to validate the security of that link or replace it.
The Controller Layer
The controller is the brain of each door group and the piece most often underestimated. It stores the access rights for the doors it supervises, validates presented credentials, and drives the lock. Controllers hold their decisions in memory so that a network or server outage does not lock everyone out of the building; this local decision-making is what allows access to continue during a temporary failure of the central platform. Controllers also manage door position sensors and request-to-exit devices, interpret tamper and forced-door signals, and buffer events until they can be delivered to the server.
Controller sizing follows from door count and topology. A single controller may supervise one door or a cluster of doors in the same area, which reduces wiring distance and centralizes power. Each controller needs a power source rated for the locks and readers it drives, and increasingly it needs a network connection to the management server, either over the building's IP network or a dedicated bus. The number of controllers, their cabinet locations, and their battery backup together define much of the system's resilience, so the physical design of the controller layer deserves as much planning as the software.
The Network and Management Software Layers
The final two layers tie the doors into a single system. The network layer moves events from controllers to the server and commands from the server to controllers; it may be the building's existing Ethernet, a dedicated access-control bus, or a mix of wired and wireless door controllers. The management software layer holds the central access database, the credential-holder records, the audit log, and the user interface used by administrators to grant and revoke access. This is where door schedules, holiday calendars, anti-passback rules, and alarm handling are configured.
The software is where most commercial building access control decisions ultimately converge, because it is the single place where policy is expressed. Before selecting any hardware, you should confirm the software supports your door count, your credential families, your reporting needs, and your integration targets, because swapping software later is far costlier than swapping a reader.
Commercial Building Access Control Guide Credential Options
Credentials are the identities your system recognizes, and the family you choose shapes security, convenience, and cost. Proximity cards and fobs use a 125 kHz or 13.56 MHz transponder and are inexpensive to issue but can be lost or shared. Smart cards at 13.56 MHz add cryptography and can carry multiple applications. Mobile credentials push a phone-based token and let you provision and revoke access remotely without printing a card. PIN keypads are simple and cheap but rely on the secrecy of the code. Biometric readers bind access to a fingerprint, face, or palm print and are the strongest proof that the person presenting the credential is the authorized user, though they add sensor cost and privacy considerations. Some readers combine two of these, which is the basis of multifactor authentication at the door. Many systems mix families, using a card plus PIN for high-security doors and a single credential type elsewhere, so the practical skill is choosing a family that matches your user population and your threat model rather than the cheapest option. Together these credential families define both the user experience at every door and the administrative effort required to issue, replace, and revoke identities over the life of the system.
Choose the credential family against your real user population and churn rate. A high-turnover tenant building may value instant mobile provisioning, while a low-traffic equipment room may be fine with a keypad. Where compliance matters, look for a system that logs which credential was presented, at which door, and at what time.
Card and Fob Credentials
Card and fob credentials are the workhorse of the industry because they are cheap, durable, and easy to manage at scale. The oldest family operates at 125 kHz and is essentially a read-only identifier; it is simple and inexpensive but offers little protection against cloning, which makes it a poor fit for exterior perimeters in higher-risk facilities. The newer family operates at 13.56 MHz and includes cards that support cryptography, so the reader and card perform a mutual challenge-and-response exchange that makes copying the credential far harder. High-security variants add even stronger key management and are commonly required for facilities such as data centers and research spaces where a duplicated badge is an unacceptable risk.
Many organizations standardize on a 13.56 MHz smart card as the common denominator, then layer additional applications on the same card, such as a cafeteria payment purse, a copier authorization, or a time-and-attendance function. A single card that does many jobs reduces issuance cost and user friction. The card also becomes a physical inventory item that must be ordered, printed, tracked, and revoked, which is why card management software and a defined issuance process are part of a mature program.
Mobile Credentials
Mobile credentials replace the plastic card with a token delivered to a smartphone, which changes the economics of issuance and revocation. Because the token is delivered over the air, a new hire can be provisioned before they arrive and a terminated employee can be revoked instantly without recalling a physical badge. For buildings with high tenant or employee churn, this alone can pay for the system. Mobile credentials also survive loss differently: a lost phone is unlikely to grant access to someone who finds it, because the phone itself is typically locked.
The trade-offs are practical. Users must carry a charged phone, and the building must provide a way to provision and manage the mobile app. Mobile credentials pair naturally with Bluetooth Low Energy readers, and they integrate with identity platforms so that a single app carries access across multiple buildings. Privacy-conscious organizations should document how the phone's location is used and ensure the credential platform does not track employees beyond the access events it is authorized to record.
PIN Keypads and Biometrics
PIN keypads are the oldest electronic credential and remain useful where simplicity and cost dominate, such as a mechanical room or a small tenant suite. A PIN is easy to revoke by deleting the code, but it is also easy to share or observe, so keypads should be reserved for lower-sensitivity openings unless they are combined with a card as a second factor.
Biometric readers bind access to a physical characteristic and are the strongest proof of identity at the door because the credential cannot be lent or duplicated in the way a card can. Fingerprint, face, and palm readers each carry different privacy expectations and environmental sensitivities, and they require enrollment, which adds to onboarding time. Biometric data must be handled under clear policy, and in many jurisdictions the storage of biometric templates is regulated. A common pattern is to use biometrics at high-security interior doors while relying on cards or mobile credentials at the perimeter, where throughput and weather matter more.
Commercial Building Access Control Guide Planning Steps
Planning a commercial building access control rollout follows a repeatable sequence. First, inventory every opening you need to secure and classify it as perimeter, interior, or high-security. Second, define the user roles and the zone each role may enter, and decide whether access is time-based, level-based, or both. Third, choose the credential family and the fail mode, remembering that a fail-safe lock releases on power loss to allow escape, while a fail-secure lock stays locked and suits exterior doors. Fourth, plan the network, deciding between wired controllers and wireless locks and confirming that power is available at each door. Fifth, select management software that matches your door count and reporting needs. Finally, schedule commissioning, staff training, and a trial period before full go-live. Working through these steps in order prevents the most common retrofit failures, because each decision constrains the next and skipping ahead forces expensive rework at a later stage.
The failure mode decision is the one to get right first, because it affects life safety and cannot easily be changed later. Confirm local fire and accessibility codes with a qualified professional, since egress requirements and disabled-access regulations can override the default fail mode.
Inventorying Openings and Zones
The planning process begins with a complete inventory of openings, and the quality of this inventory determines everything that follows. Walk the building and record every door that needs control, including main entrances, interior office doors, conference rooms, storage areas, mechanical rooms, stairwell doors, and loading docks. For each opening, note the frame material, the door leaf type, whether it is single or double, the direction of swing, the presence of a panic bar, and the surrounding environment. These details decide which locking hardware can be installed and which readers can survive the location.
Once the openings are inventoried, group them into zones that express your security policy. A zone is a set of doors and areas that share the same access rights, such as the public lobby, the general office floor, the server room, and the loading dock. Defining zones early lets you express policy as zone-to-role mappings instead of door-by-door lists, which is far easier to audit and to change when the organization reconfigures its space. Each opening is then assigned to a zone and, within that zone, given a fail mode, a credential requirement, and a schedule.
Defining Roles, Schedules, and Access Levels
With zones in place, you define the roles that will move through them. A role is a named collection of permissions, such as Employee, Contractor, Visitor, or Facilities. Each role is mapped to the zones it may enter and the hours it may do so, producing an access level that the system applies to every holder of that role. Time-based access restricts when a credential works, such as normal business hours or a specific shift; level-based access restricts which zones a credential reaches, such as an executive who can enter the server room while a general employee cannot.
Most systems let you combine both dimensions, and most organizations should, because a security program is only as strong as its least-privilege discipline. The audit value of clear roles is that a change to a role updates every holder at once, so when a department moves floors you adjust one role rather than hundreds of individual cards. During planning you should also decide how holidays, after-hours access, and emergency overrides behave, because these edge cases are where real-world policy most often breaks down.
Selecting the Fail Mode
The fail mode is the single most consequential physical decision in the plan, because it is a life-safety choice that is expensive to reverse. A fail-safe lock releases when power is lost, so occupants can always escape and the door does not trap anyone during an emergency; this is the correct default for almost every interior door and most egress paths. A fail-secure lock remains locked when power is lost, which protects the opening but can trap occupants unless a mechanical release, panic bar, or battery backup is provided; this suits exterior perimeters and high-security doors where protection during a power outage outweighs convenience.
Egress and accessibility codes often dictate which fail mode is acceptable, and these codes vary by jurisdiction, so the plan should be reviewed by a qualified professional before hardware is ordered. Where a fail-safe release is required for life safety, you also need a reliable power source and, typically, a monitored request-to-exit device so the door does not simply stay unlocked after a momentary power blip. Getting the fail mode right at planning time prevents the most expensive retrofit of the entire project.
Planning Power and Network
Every controlled door needs power and, in most designs, a network connection, and neither can be assumed. Wired controllers require a local power supply rated for the locks and readers they drive, and they need a path to the management server over the building's network. Wireless locks avoid running cable to the lock but consume batteries that must be replaced on a schedule, and they still need some form of network connectivity for events and configuration. The planning task is to walk each opening and decide which topology works, then confirm that power actually exists or can be brought in.
Battery backup deserves specific attention, because a loss of building power should not disable access entirely. At minimum, controllers on perimeter doors should have a backup supply sized to keep them functioning through a power outage, and the request-to-exit and egress paths must remain operable under their own power or fail open. Documenting the power budget per controller and per door is a deliverable of the planning phase, not something to discover during commissioning.
Commercial Building Access Control Guide Integration
Integration is what turns a door lock into a building system. A well-integrated access control platform exchanges events with video surveillance, so a door-forced alarm is accompanied by the relevant camera clip. It synchronizes with the HR directory so a terminated employee loses access automatically and a new hire is provisioned without an administrator touching each door. It feeds visitor management, elevator control, and lighting or HVAC scheduling, so an entry event can trigger floor lighting or the access profile can restrict which floors a card reaches. Open integration standards such as OSDP for readers and REST or webhook APIs for software let you avoid vendor lock-in and add systems later. Establish the integration points during planning rather than after installation, because retrofits are more expensive and introduce compatibility risk, and because the whole value of the platform is realized only when events move between systems.
Verify that any third-party system you plan to connect exposes the interface the access platform expects, and document the data flows so you know what happens when a shared service goes offline.
Video Surveillance Integration
Access control and video surveillance are natural partners, and their integration is usually the highest-value connection a building can make. When the access system detects a forced door, a door held open, or a denied credential at a sensitive door, it can trigger the camera system to capture the moment and flag the clip for review. The result is that security staff investigate a video record of the event instead of a bare alarm. This pairing also supports verification of normal activity, such as confirming that a badge swipe at a loading dock corresponds to a delivery at the dock door.
The integration is typically accomplished through a shared event bus or an API where access events are pushed to the video platform, which matches them to camera timecodes. A practical design decision is to capture the reader itself in the camera frame so the video shows both the person and the door they opened. Establish which events should trigger video recording and how long clips are retained, because unlimited recording is expensive and most events do not need one.
HR Directory and Identity Synchronization
The single most valuable automation in access control is synchronization with the human resources directory, because it closes the two gaps that manual administration always leaves open: provisioning new hires and revoking departing employees. When the identity platform is the source of truth, an employee's card or mobile credential is issued automatically when they join, their role maps to an access level, and their access is revoked the moment their employment record changes. Manual administration, by contrast, depends on a busy administrator remembering to act, and every day a terminated employee keeps access is an unacceptable risk.
Integration is a two-way discipline. The access system consumes the identity feed and returns event data that HR or security can use for reporting. Before implementation, agree on the mapping between HR attributes and access roles, define how contractors and visitors are handled, and decide what happens when the identity feed is unavailable. A well-designed sync makes onboarding a new hire and terminating a leaver routine, predictable, and auditable.
Visitor Management, Elevators, and Building Automation
Access control also connects to the broader building, and several integrations are worth planning explicitly. Visitor management software can issue a temporary credential when a guest checks in, giving the visitor access only to the lobby and the meeting room, and expiring that access automatically when the visit ends. Elevator control uses the access profile to decide which floors a credential can select, so a card that opens the front door does not necessarily reach every floor. Building automation can react to access events, turning on lights and adjusting HVAC in a space shortly before a scheduled entry and returning it to energy-saving mode when the space is empty.
Each integration is a contract with defined data flows, and each should be tested at commissioning. The recurring theme is that access events are a rich source of occupancy and movement data, and the building can act on that data only if the integration was designed in advance. Document every third-party interface, and define how the system behaves when a shared service such as the visitor platform or the elevator controller is offline, so the failure mode is known rather than discovered.
Commercial Building Access Control Guide Opening Types and Hardware Selection
Not every opening in a building should be secured the same way, and one of the most useful planning habits is to group openings by their role in the perimeter and interior security model. Main entrances, interior office doors, stairwell and mechanical doors, and loading docks each have different traffic patterns, exposure, and safety obligations, so each deserves a distinct hardware recommendation. Perimeter openings face the outside world and must resist forced entry while also handling continuous traffic and weather; interior openings mostly deter casual intrusion and carry egress obligations; and service openings such as loading docks balance security with operational speed. Planning by opening type also makes the design reviewable, because a reviewer can check that every opening of a given class was treated consistently rather than tracing each decision individually, and it forces the trade-off between security strength, throughput, and maintenance to be stated openly for each class of door.
Perimeter and Main Entrance Openings
Main entrance doors are the public face of the building and often the highest-traffic openings in the system, so the priorities are throughput, appearance, and reliable life-safety behavior. A common design pairs a credential reader outside with a fail-safe electric strike or an electrified mortise lock, a request-to-exit device on the inside, and a door position sensor to detect forced or held-open doors. Because the entrance handles many users, reader placement and mounting height must be planned so that cards and mobile credentials present cleanly and users do not bottleneck.
Perimeter openings must also resist attack. The frame, the strike, and the door leaf all contribute to the opening's resistance, and a strong lock on a weak frame is poor security. Readers at perimeter doors should use a credential technology that resists cloning, such as a 13.56 MHz smart card or a mobile credential, and the reader-to-controller link should be secure. Exterior readers need an environmental rating appropriate for rain and temperature swings, and the power supply for a fail-safe perimeter lock needs backup so the entrance does not release prematurely or fail closed on a power loss.
Interior Office and High-Security Doors
Interior doors are where the bulk of the access policy is expressed, and they carry a different set of obligations than the perimeter. Most interior doors should be fail-safe so that occupants can always egress, and they typically use a lower-grade lock than the perimeter because the threat is casual intrusion rather than forcible attack. An electrified mortise lock is common on interior doors because it keeps the door mechanically latchable and leaves a familiar lever for normal passage, with an electric release driven by the controller.
High-security interior doors, such as those protecting a server room, a data center, a lab, or a cash handling area, justify a stronger combination. These doors often use a higher-strength locking layer, a multifactor credential such as a card plus PIN or a biometric reader, a monitored door position sensor, and a schedule that limits hours tightly. The audit log for high-security doors should capture every grant and denial with a timestamp and identity, because these openings are where a security incident is most likely to be examined later. Selecting hardware for high-security doors is largely a matter of forcing both strong authentication and complete logging.
Loading Docks and Service Openings
Loading docks and service openings are a special class because they combine continuous operational traffic with significant security exposure. A dock is where deliveries, contractors, and maintenance personnel enter, and it is often one of the least controlled points in a building. The design goal is to make authorized traffic fast while keeping unauthorized entry difficult, which usually means a reader for credentialed personnel, a monitored exterior, and a clear procedure for handling unscheduled deliveries and dock doors.
The physical constraints at a dock differ from an office door. Dock openings are large, exposed to weather, and often fitted with overhead doors or roll-up doors that use their own mechanisms rather than a conventional latch. Access control at a dock may therefore supervise the overhead door release and the pedestrian door beside it, record delivery events, and integrate with a visitor or vendor management process so that unscheduled arrivals are screened. Docks should also have a defined procedure for door-held-open conditions, because a dock door left open is a common way a building loses both security and conditioned air.
Commercial Building Access Control Guide Scheduling, Anti-Passback, and System Rules
Beyond deciding who may enter, a mature access control program uses rules to govern when and how access happens, and these rules are configured in the management software. The most common rules are door schedules, which restrict which days and hours a credential works; holiday calendars, which overlay the regular schedule; anti-passback, which prevents a single credential from being used to re-enter an area; and time zones that bind users to shifts. Each rule is an expression of policy, and each should be designed, documented, and tested rather than enabled by default without thought. The value of these rules is that they turn a static list of who-can-enter-where into a living policy that matches how the building actually operates, while the risk is that a rule configured incorrectly can lock out legitimate users or silently permit an intrusion, which is why rule changes should follow the same change-control and testing discipline as hardware changes.
Scheduling and Holiday Calendars
Door schedules are the most basic and the most heavily used rule. A schedule defines when a door is accessible, and it can be applied either to the door, so that a particular door is only usable during business hours, or to a user role, so that a shift worker only has access during their shift. Combined schedules allow a door to be open during business hours for everyone and restricted after hours to a maintenance role, which is the classic office configuration.
Holiday calendars overlay the normal schedule, and they are a frequent source of errors because buildings operate on regional and organizational holidays that shift each year. A good implementation maintains a holiday calendar in the software, reviews it annually, and tests that a holiday truly behaves as intended before the day arrives. Scheduling also interacts with the audit log, because a denied event after hours is often the first signal of a problem, so the configuration should produce a meaningful event for both grants and denials.
Anti-Passback and Tailgating Mitigation
Anti-passback is a rule that prevents a credential from being reused to pass back out of a secured area, which blocks the practice where one person hands a card to another after entering. In its strictest form, once a credential is used to enter a zone, it cannot be used to enter again until it has exited; in a softer form, the system simply raises an alarm or logs a warning when the pattern is detected. Anti-passback is most valuable in high-security zones and least valuable in public areas, where it can create frustrating false alarms.
Anti-passback cannot by itself stop tailgating, where an unauthorized person slips in behind an authorized one before the door closes. Mitigating tailgating requires physical controls such as mantrap portals, turnstiles, or door position monitoring with alarm response, and these are best combined with the video integration described earlier so that an alarm is investigated with footage. Planning anti-passback and tailgating controls means deciding which zones genuinely need them, because they add operational friction and should be reserved for the areas where the risk justifies it.
Commercial Building Access Control Guide Power, Wiring, and Controller Design
The physical infrastructure of an access control system is where projects most often run late and over budget, because it is invisible in the sales comparison and entirely visible in the installation. Power, wiring, and controller placement determine whether a design is practical, serviceable, and resilient, and each trades installation cost against ongoing maintenance while interacting with the building's existing conduits, risers, and power closets. The plan should specify, for every door, how it is powered, how it communicates, and which controller supervises it, and it should document those decisions in a way a future technician can understand. Three recurring infrastructure decisions shape the design: wired versus wireless locking, centralized versus distributed controllers, and the nature and redundancy of the power and network, and getting each of these right at planning time is what keeps an installation on schedule and a system serviceable for its whole life.
Wired versus Wireless Locks
Wired locks connect directly to a controller and a power source, which gives them reliable power, immediate communication, and no battery replacement, at the cost of running cable to each door. Wired designs are the traditional choice for commercial buildings where the conduit, riser, and ceiling space exist to carry the cable, and they remain the best option where doors are clustered and power is available nearby. The ongoing cost is low because there is nothing to re-battery and firmware can be managed centrally over the network.
Wireless locks use batteries and a wireless link, which removes the cable run and makes retrofits far cheaper on doors where pulling wire is impractical or prohibited by the building's construction. The trade-offs are battery replacement on a schedule, a need to monitor battery status, and a communication medium that can be affected by range and interference. Wireless locks are a strong choice for interior doors in historic or leased buildings where structural changes are restricted, and they are increasingly used in combination with wired controllers for the perimeter. The decision is fundamentally about cable access versus maintenance, and it should be made door by door rather than globally.
Controller Placement and Cabinet Design
Controllers are typically installed in a cabinet near the doors they supervise, and the layout of these cabinets determines how much cable is needed and how easy the system is to maintain. A distributed design places a controller close to each door cluster, which shortens cable runs but spreads the hardware across the building; a centralized design concentrates controllers in a few secure rooms, which concentrates power and network infrastructure but requires longer cable runs to distant doors. Most buildings end up with a hybrid, locating controllers in electrical or IDF closets near clusters of doors.
Each controller cabinet needs a defined power budget, a network drop, and physical security, because a controller left in an unlocked closet is an easy attack point. The cabinet should be sized for growth, labelled, and documented with a schematic showing which doors it drives. Battery backup should be designed at the cabinet level so that a power failure does not disable an entire floor, and the design should state how long each cabinet must survive on backup power.
Power Sizing and Backup
Power is the most failure-prone part of an access control system, and it deserves the same rigor as the hardware. Every lock, reader, and controller has a current draw, and the power supply must be sized to cover the connected load with margin, including the surge when several locks energize at once. A reader at the far end of a long cable run needs enough voltage at the device, not just at the supply, so cable gauge and distance are part of the power calculation.
Backup power is a policy decision expressed in hardware. Perimeter and life-safety doors need enough battery backup to remain secure and egressible through a realistic outage, while interior doors may be allowed to behave according to their fail mode. The design should specify backup duration, battery monitoring, and a testing routine, because a backup that fails on the day it is needed is worse than none. Documenting the power budget per cabinet and per door is a deliverable that a competent installation depends on.
Commercial Building Access Control Guide Cybersecurity and IT Considerations
Modern access control is a networked IT system, which means it shares the security obligations of any networked system. The management server, the controllers, and the reader links are all attack surfaces, and a compromised access system is a direct path to physical intrusion. Cybersecurity in this context covers protecting the management server and its data, securing the communication between server and controllers, protecting credentials and the identity data behind them, and integrating with the organization's broader IT security posture.
The conversation between security and IT teams is often one of the most valuable parts of the planning process, because each side brings a different view of the same risk. The access control vendor should provide guidance on hardening, and the IT team should review it against the organization's standards before deployment, not after an incident.
Protecting the Management Server
The management server holds the access database, the credential records, the audit log, and the administrative interface, which makes it the crown jewel of the system and the primary target for attack. It should be patched on a schedule, protected by strong authentication for administrators, and restricted to a controlled network segment rather than exposed to the general office network. Administrative access should be limited to named individuals, and all administrative actions should themselves be logged so that changes to access rights are accountable.
The server also needs a backup and recovery plan, because losing the access database can mean re-provisioning every credential in the building. Backups should be tested, encrypted, and stored separately from the live server, and the plan should state how quickly access can be restored after a server failure. Organizations increasingly move the management platform to the cloud, which transfers some of this responsibility to the provider but requires its own due diligence on the provider's security, data location, and access controls.
Securing Controllers and Reader Links
The controllers and the links to the readers are physical infrastructure, but they carry the same trust as the software. A controller in an unlocked cabinet can be tampered with or reprogrammed, so controller cabinets should be physically secured and monitored. The reader-to-controller link deserves particular attention because legacy Wiegand wiring transmits credential data in a way that can be intercepted or cloned; migrating readers to OSDP, which encrypts and authenticates the reader link, materially hardens the door against wire attacks.
Firmware on readers and controllers must be kept current, because access control hardware is not immune to vulnerabilities and a known flaw in an unpatched controller is a standing risk. The deployment plan should include a firmware update and patch management process, and the vendor contract should state how long security updates are provided. Treating the physical access system as part of the organization's IT asset inventory is the single most effective way to keep it secure over its service life.
Identity Data and Privacy
Access control systems hold sensitive data: who is allowed where, when, and with what credentials, along with names, identifiers, and potentially biometric templates. This data is subject to privacy obligations in many jurisdictions, and the deployment should define how it is collected, stored, retained, and deleted. Biometric data is the most sensitive category, and its handling should follow documented policy and, where applicable, regulatory requirements for consent and storage of biometric templates.
Access event data is also valuable to an attacker because it reveals patterns of occupancy and movement, so the audit log should be protected, retained for an appropriate period, and accessible only to authorized personnel. Privacy and security should be addressed in the procurement requirements rather than improvised after deployment, because retrofitting data protection into a system that was not designed for it is difficult and expensive.
Commercial Building Access Control Guide Tenant, Owner, and Multi-Tenant Operation
Access control operates differently depending on who owns and operates the building, and the ownership model changes the requirements substantially. A single-tenant building where the occupier owns the system has one set of needs; a landlord-owned multi-tenant building has another; and a building where tenants install their own systems inside a landlord-managed shell has yet another. Clarifying the ownership model early avoids the most common disputes about who controls, pays for, and maintains what.
The ownership model also determines how credentials, zones, and integrations are managed, and whether a single platform or multiple platforms will be needed. In a multi-tenant building, the landlord typically controls the shared perimeter and common areas while each tenant controls its own suite, and the two layers may run on entirely separate systems.
Single-Tenant Owner Operation
In a single-tenant building, the organization that occupies the building usually owns and operates the access control system, which gives it complete control over policy, data, and hardware. The advantages are simplicity and accountability: one team defines roles, one platform holds the access database, and one contract covers maintenance. Single-tenant operation also makes integration simpler, because the HR directory, video, and access systems are all managed by the same organization and can share an identity source.
The main discipline for a single-tenant deployment is to keep the system aligned with the organization as it changes, because a system built for one headcount and layout is often allowed to drift as the company grows. Regular reviews of roles, zones, and the audit log keep the system truthful. Single-tenant owners also own the upgrade and lifecycle decision, so they should plan for the eventual replacement of readers and controllers rather than treating the system as permanent.
Landlord-Owned Multi-Tenant Operation
In a multi-tenant building, the landlord typically owns and controls the perimeter system, the common-area doors, the elevators, and the shared visitor experience, while each tenant controls access within its own suite. The landlord-managed layer sets the standard for how the building works, and it must accommodate a diverse set of tenants with different hours, staff sizes, and security needs. The perimeter platform may hold credentials for every tenant's employees and visitors, which makes provisioning and revocation at scale a core requirement.
The interface between the landlord layer and the tenant layer is the point that needs the most planning. Tenants may install their own readers and locks inside their suites, and the landlord must decide whether those tenant systems interoperate with the building platform or run independently. When they run independently, the landlord still needs a way to open tenant doors for emergencies and maintenance, so the agreement should define access rights, notification, and liability. A well-run multi-tenant building treats access control as a shared service with clear boundaries, not as a single system owned by everyone.
Tenant-Installed and Hybrid Models
A hybrid model is common in leased offices and multi-use developments, where the landlord provides the shell and core access and each tenant installs and operates a separate system inside its leased space. The tenant system may be a small commercial panel or a set of wireless locks managed through its own software, and it is completely under the tenant's control. This model gives tenants flexibility and privacy, at the cost of some duplication and a lack of integration with the building platform.
The practical challenges are coordination and egress. Tenant doors still sit within the landlord's fire and egress design, so tenant-installed hardware must satisfy the building's safety requirements even though it is not on the landlord's system. The two systems also need agreed exception handling, so that emergency responders and building management can open tenant doors when necessary. Documenting these cross-boundary rules in the lease and the building operating procedures prevents conflict later, and it is a task best done when the tenant system is first installed rather than during an incident.
Commercial Building Access Control Guide Commissioning, Acceptance, and Testing
The installation is not finished when the hardware is mounted; it is finished when the system has been commissioned, accepted, and shown to behave correctly under the full range of operating conditions. Commissioning is the phase where the design assumptions are tested against the real doors, the real users, and the real building, and it is where most defects surface. A structured commissioning and acceptance process, with written test evidence, turns an installation into a system that can be operated with confidence.
Commissioning should cover hardware, wiring, power, software, rules, and integrations, and it should be documented so that the results are reviewable and the building manager inherits a record of what was verified. Acceptance is the contractual step where the owner signs off that the system meets the specification, and it should be tied to demonstrated results rather than to the vendor's promise.
The Commissioning Sequence
Commissioning typically proceeds door by door before it proceeds system wide. For each opening, the installer verifies that the lock operates, the reader reads the intended credentials, the controller makes the right grant and denial decisions, and the request-to-exit and door position sensors report correctly. Each door is tested in its fail mode by cutting power and confirming the door behaves as designed, because a fail-safe door that stays locked on power loss is a life-safety failure that must be caught before occupancy.
After individual doors pass, the team tests the rules and the software: schedules, holiday calendars, anti-passback, revocations, and alarm handling. Finally, the integrations are exercised, with a test credential triggering a video clip, an HR record change revoking access, and a visitor credential expiring as intended. Each test produces written evidence, and a commissioning report records every door, every test, and every pass or fail. The report is the deliverable that makes the acceptance decision possible.
Acceptance and Handover
Acceptance is the point where the owner confirms the system meets the specification and takes operational responsibility. A well-run acceptance process uses the commissioning report as its foundation, then adds a trial period during which the system runs in normal operation and defects are collected and fixed. The acceptance criteria should have been agreed in the procurement documents, so both parties know what passing looks like before the work begins.
Handover is the operational transfer, and it should include training for the administrators who will manage credentials and the technicians who will service the doors. The owner should receive complete as-built documentation, including the door-by-door schedule, the power budgets, the controller layouts, the integration interfaces, and the recovery procedures. A system handed over without documentation is a system that no one can safely own, so the quality of the handover is a fair measure of the quality of the installation.
Commercial Building Access Control Guide Maintenance, Recovery, and Lifecycle Management
Once accepted, the system enters the phase where its real cost and its real value are decided: operations. Access control is rarely a set-and-forget installation, because buildings change, people change, and hardware ages. A maintenance program, a recovery plan, and a lifecycle view keep the system secure and reliable over the years that it will actually serve the building, and they are as important to the business case as the original hardware purchase.
Maintenance covers both the routine and the reactive. Routine work includes battery replacement, firmware updates, reader cleaning, and credential housekeeping; reactive work covers failed locks, damaged readers, and alarm response. The plan should define who does each, on what schedule, and at what cost, and it should be reviewed regularly so that it keeps pace with the building.
Routine Maintenance and Battery Programs
For wireless locks, battery management is the largest recurring maintenance item, and a disciplined battery program prevents the failure that wireless designs are most exposed to: a door that stops responding because its battery is flat. The system should monitor battery status and alert before a lock fails, and the maintenance calendar should schedule replacement on the manufacturer's guidance. Because batteries fail faster in extreme temperatures and high-traffic doors, the program should weight replacement by door condition rather than treating every door identically.
Firmware updates are a security maintenance task as well as a functional one, because they carry the patches that close vulnerabilities. Updates should follow a change-control process, tested on a sample door before rollout, and scheduled during low-traffic hours so a brief reboot does not interrupt occupancy. Reader cleaning and inspection are simple but important, because a reader with a damaged surface or a loose mount will fail eventually and a dirty biometric sensor will frustrate users.
Incident Response and Recovery
The recovery plan answers the question of what happens when something fails, and it is best written before the failure occurs. Common scenarios are a controller failure, a network outage, a server loss, and a mass lockout when credentials cannot be validated. For each scenario, the plan should state the expected behavior, who responds, and how access is restored, and it should be tested, because a recovery plan that has never been exercised usually fails on the day it is needed.
The plan should also cover the unusual but consequential cases: a lost master key to the access database, a compromised administrator account, or a suspected breach of the credential system. A documented procedure for these events, including who is authorized to take emergency action, protects the building and limits the damage. Recovery is the last line of defense in access control, and like the fail mode decision, it is far cheaper to design well in advance than to improvise during an incident.
Lifecycle Budgeting and Replacement
The lifecycle view of access control treats the system as a depreciating asset with a finite service life rather than a one-time purchase. Hardware reaches end of life, software goes out of support, and a system that is not upgraded eventually becomes both a security risk and an operational liability. The lifecycle budget should therefore include not just the original purchase and ongoing maintenance, but the eventual replacement of readers, controllers, and software, and it should anticipate the migration effort that replacement involves.
The contract terms set the ceiling for the lifecycle cost. The agreement should state how long firmware and security updates are provided, what the end-of-support date is, whether spare parts remain available, and how the vendor migrates data and configuration to a successor platform. A building that asks these questions before purchase avoids the most expensive surprise in access control: being forced into a rip-and-replace because the incumbent product went end-of-life with no clear path forward.
Commercial Building Access Control Guide Procurement and RFP Guidance
Procurement is where the planning work pays off, because a well-specified request for proposal produces comparable bids and a defensible decision, while a poorly specified one produces apples-to-oranges quotes and post-award disputes. The RFP should describe the outcomes the building needs, the openings to be controlled, the credential families, the integration targets, the fail-mode and egress requirements, the service and support expectations, and the lifecycle terms described in this guide. It should ask each supplier to respond to the same specification so that bids can be compared on a consistent basis.
The decision is a systems decision, so the evaluation should weigh the software, the support, and the integration ability at least as heavily as the hardware price. A low hardware price attached to weak software or short support is rarely a bargain over the ten-year life of the system.
Building the Specification
A strong specification starts with the inventory and the zone model developed during planning, and it turns them into explicit requirements. For each opening, the specification states the locking hardware, the fail mode, the reader type, the credential family, and the power and network assumptions, so that every supplier prices the same scope. For the software, it states the door count, the user population, the reporting depth, the integration interfaces, and the administrative and audit features expected.
The specification should also state the operational and lifecycle terms that matter most: firmware update policy, end-of-support commitment, response times for service, spare parts availability, and the process for migrating to a successor platform. Making these terms explicit in the RFP is what makes the lifecycle cost comparable across suppliers, and it is what prevents the post-award surprises that drain budgets and confidence.
Evaluating and Comparing Bids
Evaluating bids on a consistent basis requires a common evaluation framework, and the framework should be defined before the bids arrive. The obvious dimension is price, but it should be evaluated as lifecycle cost, including hardware, installation, licensing, credentials, maintenance, and projected replacement, rather than as sticker price alone. The other dimensions are capability against the specification, integration fit with the systems the building already uses, the quality and availability of support, and the supplier's history of security updates and product continuity.
A practical technique is to require each supplier to respond to the same questionnaire and to demonstrate its software and its integration behavior in a live or hands-on session, because written claims are easier than working systems. The winning bid is usually not the cheapest; it is the one that satisfies the specification, fits the integration targets, and offers a lifecycle cost and support commitment the building can live with. A comparison table, built from the same fields for every supplier, makes the decision transparent and defensible.
The Comparison Table
| Decision factor | Why it matters | Wired system | Wireless system |
|---|---|---|---|
| Installation cost | Cable runs dominate retrofit price | Higher, needs conduit and power at each door | Lower, no cable to the lock |
| Ongoing maintenance | Drives lifecycle cost | Low, no batteries to replace | Higher, scheduled battery replacement |
| Power reliability | Locks must behave correctly | Reliable, supplied power | Depends on battery monitoring |
| Retrofit friendliness | Historic and leased buildings | Limited by structure | Strong, minimal structural change |
| Event latency | Alarms and monitoring | Immediate | Depends on wireless link |
| Best-fit openings | Match hardware to exposure | Perimeter and high-traffic doors | Interior and structurally restricted doors |
| Credential family | Security | Convenience | Issuance cost | Best fit |
|---|---|---|---|---|
| 125 kHz card or fob | Low, easily cloned | Very high | Very low | Interior, low-risk |
| 13.56 MHz smart card | Higher, cryptographic | High | Low to medium | General commercial default |
| Mobile credential | High | High, but needs a charged phone | Very low at scale | High-churn buildings |
| PIN keypad | Low unless combined | Low | Minimal | Mechanical rooms |
| Card plus PIN | High, multifactor | Medium | Low | High-security doors |
| Biometric | Very high | Medium, needs enrollment | Medium to high | High-security interior |
Commercial Building Access Control Guide A Worked Decision Example
To make the framework concrete, consider a worked example of a mid-sized office building retrofit. The building has one main entrance, a loading dock, and interior doors across three floors, with a stable tenant population of about two hundred employees and a modest visitor flow. The goals are to secure the perimeter, control the dock, manage roles and schedules across the interior, and keep a defensible audit trail, all within a lifecycle budget that favors reliability over the lowest possible first cost.
The analysis starts with the openings. The main entrance gets a fail-safe electric strike, a 13.56 MHz smart card reader with OSDP to resist cloning, a request-to-exit device, and a door position sensor, with battery backup on the perimeter controllers. The dock gets a supervised reader, a pedestrian door with an electrified lock, and a visitor and delivery procedure tied to the visitor management integration. Interior doors get electrified mortise locks that are fail-safe for egress, with the server room and a cash handling area upgraded to card plus PIN and full audit logging.
Credentials are standardized on a 13.56 MHz smart card, with mobile credentials offered as an option to reduce issuance cost as the tenant population turns over. Integration priorities are set early: video surveillance so a forced door produces a clip, the HR directory so access is provisioned and revoked automatically, and the elevator so that cards reach only the floors their role permits. The lifecycle budget includes battery-free wired interior locks where the ceiling space allows, firmware and security update terms written into the contract, and a documented replacement plan for readers at their end of life.
Commissioning is run door by door with written evidence, the fail mode of every door is tested on power loss, and the integration tests cover a forced-door clip, an HR revocation, and a visitor credential expiring on time. The acceptance handover includes administrator training, the as-built door-by-door schedule, power budgets, and recovery procedures. The result is a system whose security, cost, and maintenance were decided deliberately rather than inherited, and one that a future facilities team can operate and extend without re-discovering the building from scratch.
Confirm legal, fire, accessibility, cybersecurity, and engineering requirements with qualified professionals before you act on this guide, and validate every hardware choice against current model-specific documentation for the opening you are securing.
Part of this article content is generated by AI and optimized for professional accuracy and readability.
Vous ne savez pas quel capteur choisir ?
Parlez à nos ingénieurs d’application mmWave pour une consultation gratuite.
Spécifiez votre projet hôtelier avec nos ingénieurs
Indiquez le nombre de chambres, le type de plafond et votre préférence de protocole. Nous renverrons un plan d'échantillon et un devis sous 24 heures ouvrées.
- Passez d'une guidance générale à une discussion produit ou application.
- Utilisez la RFQ quand le prix, les plans, le MOQ ou le calendrier de lancement nécessitent de la structure.
- Gardez une voie de contact direct visible pour les clarifications rapides et le transfert.