Guía de Sistemas de Control de Acceso Comercial
Una guía de ingeniería para planificar e implementar sistemas de control de acceso comercial en arquitectura, credenciales, seguridad, integración, alimentación, puesta en marcha y costo de ciclo de vida.
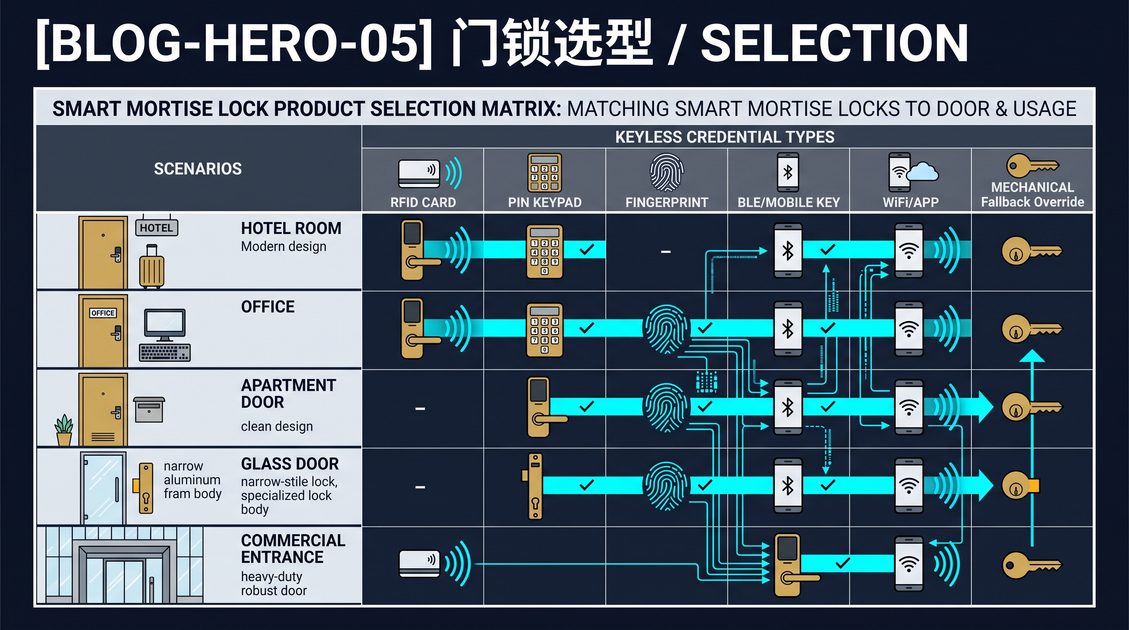
Guía de Sistemas de Control de Acceso Comercial — Alcance y Definición
Un sistema de control de acceso comercial es una plataforma electrónica integrada que decide quién puede ingresar a un edificio, a un piso o a una habitación, y registra cada intento. Por lo general, combina cerraduras o hardware electrificado, lectores de credenciales, controladores que aplican políticas, una plataforma de gestión de software y, a menudo, la integración con video, alarmas, gestión de visitantes y automatización de edificios. Las credenciales incluyen tarjetas, llaveros, PIN, billeteras móviles y datos biométricos, y las decisiones pueden tomarse localmente en cada puerta o de forma centralizada, y el sistema mantiene una pista de auditoría de cada evento de acceso. Un sistema de control de acceso comercial se selecciona según el modelo de amenaza del sitio, sus patrones de identidad y rotación, su infraestructura física y de TI existente, y sus obligaciones de salida y seguridad humana, por lo que el plan de implementación importa tanto como la lista de funciones del hardware, y la pista de auditoría que produce se convierte en uno de sus resultados más valiosos para investigaciones y cumplimiento normativo.
Trate el control de acceso como una plataforma de políticas, no como una colección de cerraduras electrónicas. El mismo sistema que admite a un empleado en un torniquete de lobby puede proteger una sala de servidores y activar una alarma en un laboratorio, y cada una de esas aberturas conlleva un riesgo diferente que la capa de políticas debe expresar. Es por esto que el manual del comprador comienza con un cronograma puerta por puerta y una política de acceso escrita, no con un catálogo de productos.
Qué distingue un sistema de control de acceso comercial del hardware doméstico o de pequeña oficina
La frontera entre las cerraduras inteligentes residenciales y los verdaderos sistemas de control de acceso comercial está definida por cuatro capacidades, no por la marca ni el punto de precio. La primera es la gestión centralizada: una plataforma comercial genuina gestiona muchas puertas, muchas personas y muchos horarios desde una sola consola, mientras que una cerradura de consumo se administra puerta por puerta a través de su propia aplicación. La segunda es la pista de auditoría: los sistemas comerciales registran quién hizo qué, cuándo y en qué abertura, de una manera que sobrevive a la pérdida de energía y puede exportarse para investigaciones. La tercera es la amplitud de credenciales y el manejo de rotación, que cubre poblaciones grandes y cambiantes con revocación instantánea. La cuarta es la integración, es decir, la capacidad de vincularse con video, alarmas, directorios de identidad y automatización de edificios a través de interfaces abiertas.
Las principales categorías de implementación
Las implementaciones de sistemas de control de acceso comercial suelen caer en unas pocas categorías que dan forma al diseño completo. Los sitios pequeños y medianos, como clínicas, bufetes de abogados u oficinas centrales de comercio minorista, pueden ejecutar una instalación de recuento de puertas modesto con un número reducido de lectores y un puñado de controladores. Los edificios individuales más grandes, como torres corporativas, hospitales o universidades, distribuyen controladores entre pisos y alas, a menudo conectados a través de la LAN del sitio y gestionados de forma centralizada. Las organizaciones distribuidas de múltiples sitios, incluidas sucursales bancarias, depósitos logísticos, cadenas minoristas o redes de franquicias, operan muchos sitios independientes desde una plataforma de gestión regional o basada en la nube. Los sitios industriales y de alta seguridad añaden lectores robustos, detección de manipulación, redes segregadas y políticas más estrictas como el anti-retorno. Cada una de estas formas impulsa un conjunto diferente de requisitos hacia las decisiones de arquitectura, cableado, credenciales y ciclo de vida que se cubren en el resto de esta guía.
Guía de Sistemas de Control de Acceso Comercial — Arquitectura del Sistema
La arquitectura de un sistema de control de acceso comercial se describe por cómo se superponen lectores, controladores y software. El hardware de borde lee credenciales y bloquea o desbloquea puertas; los controladores toman decisiones, almacenan en caché políticas y mantienen eventos abiertos; y la plataforma de software administra usuarios, horarios, puertas e informes. Las decisiones sobre si usar controladores en línea en cada puerta, o un híbrido con cerraduras de borde a batería o fuera de línea, impulsan el costo, la resiliencia y el comportamiento durante una interrupción de la red. Un modelo centralizado brinda revocación instantánea e informes enriquecidos, pero depende de la disponibilidad de la red, mientras que un modelo local mantiene el sitio funcionando fuera de línea a costa de una administración más lenta. La arquitectura correcta coincide con el número de puertas, el alcance físico del cableado, la tolerancia al tiempo de inactividad y el tamaño de la población de identidades, y debe documentarse como un diagrama antes de comprar cualquier hardware.
Dimensione la población de controladores y los tendidos de cable a partir de un cronograma real de puertas, no de una estimación. Cada puerta en red necesita una ruta limpia de alimentación y datos, y el estudio que mapea esas rutas temprano es la diferencia entre una implementación fluida y una sorpresa en la fase de construcción.
Las capas lógicas: lector, controlador, plataforma de gestión
Ayuda pensar en un sistema de control de acceso comercial como tres capas lógicas, incluso cuando los dispositivos físicos difieren. La capa de lector es el punto físico de interacción donde una persona presenta una tarjeta, llavero, PIN, dato biométrico o credencial móvil; los lectores generalmente no contienen políticas, simplemente convierten una credencial presentada en un identificador y un evento. La capa de controlador es donde se toma la decisión: compara la credencial presentada contra una tabla de permisos almacenada en caché o recuperada, verifica las reglas de horario y anti-retorno, y acciona la cerradura o el relé. La capa de gestión es la consola de software donde un administrador define usuarios, asigna credenciales, crea horarios, mapea puertas, revisa eventos y genera informes. Mantener estas capas separadas en la mente facilita razonar sobre dónde ocurre una falla y dónde debe residir un control de seguridad.
Arquitecturas en línea, fuera de línea e híbridas
Las arquitecturas difieren principalmente en cuánta inteligencia reside en el borde y cuán dependientes son las decisiones de la red. Una arquitectura totalmente en línea mantiene cada controlador continuamente conectado al servidor de gestión, por lo que la revocación y los cambios de política se propagan casi instantáneamente y los eventos fluyen a la consola en tiempo casi real; su debilidad es que una falla de red puede dejar las puertas varadas si los controladores no almacenan políticas localmente en caché. Una arquitectura fuera de línea o de borde coloca credenciales y datos de horario en cada puerta y elimina la dependencia constante de la red, intercambiando la revocación central instantánea por resiliencia; es común donde el cableado es impracticable o donde las puertas funcionan con baterías. Una arquitectura híbrida mezcla ambas, ejecutando la mayoría de las puertas en línea y un subconjunto fuera de línea, y es cada vez más el estándar porque equilibra la resiliencia con la conveniencia de la gestión central. Cualquiera que elija, el comportamiento fuera de línea de cada controlador debe especificarse y probarse explícitamente.
Por qué importa el diagrama de arquitectura
La arquitectura debe capturarse como un diagrama antes de la adquisición porque obliga a tomar decisiones que de otro modo surgirían dolorosamente a mitad de la instalación. El diagrama registra qué puertas están en línea y cuáles fuera de línea, cómo se agrupan los controladores, cómo llegan al servidor, dónde se instalan la protección de red y alimentación, y cómo los administradores acceden a la plataforma de gestión. También revela los puntos únicos de falla: un conmutador de red compartido que sirve a un ala completa, un controlador que alimenta varias puertas de alta seguridad o un solo conducto de cable que transporta la columna vertebral del acceso. Revisar el diagrama en busca de estas dependencias y decidir de antemano cómo se tolera cada falla es un acto arquitectónico que ninguna especificación de producto puede sustituir. Actualice el diagrama a medida que el sitio cambie y consérvelo con la documentación de entrega.
Guía de Sistemas de Control de Acceso Comercial — Ciclo de Vida de Credenciales e Identidad
El ciclo de vida de la identidad gobierna cómo se inscriben, modifican y eliminan las personas durante la vida de un sistema de control de acceso comercial. Cubre los tipos y la cantidad de credenciales emitidas, el flujo de trabajo de aprobación para nuevos accesos, permisos programados o de tiempo limitado, reemplazo de credenciales, revocación instantánea por terminaciones y la auditoría de quién tiene qué acceso en cualquier momento. En un edificio con alta rotación — oficinas arrendadas, contratistas, temporales, visitantes — el volumen de inscripciones y revocaciones puede exceder varias veces la población base, por lo que la carga de administración es un criterio de selección de primera clase. La integración central de identidad con el directorio de RR. HH. o TI mantiene el acceso sincronizado con los eventos de contratación y terminación. El objetivo es que el acceso de un empleado que se va muera en el momento en que termina su empleo, sin depender de que una persona recuerde eliminarlo, y sin ningún período en el que un ex empleado aún tenga credenciales de trabajo que puedan usarse contra el negocio, ya que la revocación es el momento en que el sistema protege el sitio o lo expone.
Las credenciales de tiempo limitado y de un solo uso son adecuadas para visitantes y contratistas y reducen la cola de identidades obsoletas. Defina quién puede otorgar acceso y bajo qué aprobación; la deriva de seguridad más común no proviene del hardware, sino de la inscripción no gestionada y las revocaciones olvidadas.
Tipos de credenciales y sus compensaciones
La elección de credenciales afecta el costo, la seguridad, la conveniencia y la carga administrativa. Las tarjetas y llaveros de proximidad a 125 kHz son económicos y familiares, pero pueden clonarse con lectores simples, por lo que están siendo reemplazados por tarjetas inteligentes de 13,56 MHz que admiten autenticación mutua e intercambio de datos cifrado. Las credenciales móviles en teléfonos inteligentes añaden conveniencia y reducen el costo de emisión de tarjetas, pero requieren que los usuarios lleven e inscriban un teléfono y que el sistema gestione un ciclo de vida de credenciales móviles. Las credenciales PIN y de teclado son simples y económicas, pero son vulnerables a la observación por encima del hombro y no pueden distinguir a un usuario de otro que conozca el código. Los datos biométricos como las huellas dactilares vinculan el acceso a una persona en lugar de a una posesión, pero plantean preocupaciones de inscripción, privacidad y duplicados, y generalmente cuestan más por lector. La mayoría de los sitios combinan dos o tres tipos, usando tarjetas inteligentes o móviles para el personal cotidiano y PIN o códigos de un solo uso para visitantes.
Inscripción, aprobación y desaprovisionamiento
Un ciclo de vida de identidad confiable depende de flujos de trabajo definidos en torno a cuatro momentos. La inscripción es el momento en que se agrega una persona: alguien debe verificar la identidad, determinar qué puertas y horarios aplican, emitir la credencial física o móvil y registrar quién aprobó el otorgamiento. El cambio cubre traslados y cambios de rol, como un empleado que se reubica a un nuevo piso y cuyas puertas anteriores deben eliminarse. La suspensión y la revocación son los momentos que más importan para la seguridad, porque un empleado terminado o que se ha ido cuya credencial aún funciona es un riesgo vivo; el proceso no debe requerir memoria humana, por lo que la sincronización automática con el directorio de RR. HH. o identidad es muy preferible a la eliminación manual. Finalmente, la recertificación periódica revisa a toda la población para confirmar que el acceso de cada persona aún coincide con su rol actual, y esta revisión es lo que realmente evita que una población creciente acumule silenciosamente credenciales obsoletas.
La carga administrativa como criterio de selección
Es común subestimar cuánto tiempo consume la administración de identidades. En un edificio con alta rotación, el número anual de emisiones, cambios y revocaciones de credenciales puede ser varias veces la plantilla, y cada uno toma tiempo de un administrador, necesita una aprobación y puede generar un error. Al comparar sistemas de control de acceso comercial, pregunte directamente cuánto tiempo toman las operaciones comunes, cómo se manejan los lotes de inscripciones, si los cambios de RR. HH. fluyen automáticamente y cómo se propagan las revocaciones a cada puerta, incluidas las fuera de línea y a batería. Una plataforma que hace la revocación confiable y económica vale más que una que es marginalmente más rápida al otorgar acceso, porque otorgar demasiado es la deriva que erosiona la seguridad silenciosamente a lo largo de los años.
Guía de Sistemas de Control de Acceso Comercial — Ingeniería de Seguridad y Modelo de Amenaza
La ingeniería de seguridad para un sistema de control de acceso comercial comienza con un modelo de amenaza de lo que un atacante quiere, quién está motivado y cómo intentaría. Las amenazas típicas incluyen pérdida o robo de credenciales, seguimiento de un titular legítimo a través de una puerta, ataques de relé a tarjetas sin contacto, ingeniería social para obtener un PIN o credencial, intrusión en la red contra el servidor de gestión y manipulación física de lectores o cajas de cerradura. Los controles abarcan el cifrado de credenciales y comunicaciones, anti-retorno para evitar que una credencial entre dos veces, integración de movimiento y alarma, registro de auditoría con alertas, detección de manipulación y credenciales que pueden revocarse instantáneamente desde una consola central. La profundidad del control es proporcional a lo que protege cada abertura; clasificar las puertas por el valor que hay detrás mantiene el presupuesto y la monitorización donde el riesgo residual se reduce genuinamente. Esta guía es educativa y no sustituye una revisión de seguridad calificada del sitio específico.
Exprese cada amenaza en lenguaje sencillo y clasifique las áreas protegidas por consecuencia. No todas las aberturas necesitan una puerta de alta seguridad monitorizada, y escribir ese juicio explícitamente es planificación sólida, no un compromiso.
Construyendo el modelo de amenaza
Un modelo de amenaza para sistemas de control de acceso comercial se construye mejor como una tabla de tres columnas: el activo que protege una abertura, el atacante realista y la ruta de ataque. El activo podría ser una sala de servidores que contiene datos de clientes, un almacén de farmacia, una sala de máquinas o simplemente la planta de oficinas; el atacante podría ser un ex empleado descontento, un ladrón oportunista, un grupo organizado que apunta a inventario, o un visitante que deambuló hacia el pasillo equivocado. Las rutas de ataque a considerar incluyen usar una credencial perdida o robada, seguir a un titular legítimo a través de una puerta sin presentar credencial, reproducir o retransmitir una señal sin contacto desde la distancia, adivinar u observar un PIN, persuadir a un miembro del personal para que revele un código o credencial, manipular el hardware del lector o la cerradura, y atacar el servidor de gestión a través de la red. Escribir estas cosas obliga al diseño a responder a motivos reales en lugar de a una lista genérica de amenazas.
Seguimiento, ataques de relé y anti-retorno
Varias amenazas son lo suficientemente específicas como para mencionarlas porque dan forma a las decisiones de hardware y políticas. El seguimiento — alguien que entra detrás de un titular autorizado sin presentar credencial — generalmente se aborda con la ubicación del lector, configuraciones de torniquetes o esclusas para áreas de alta seguridad, verificación por video y cultura del personal, más que con la cerradura en sí. Los ataques de relé a credenciales sin contacto extienden la señal de una tarjeta desde el bolsillo de una persona a un lector lejano, por lo que un titular puede ser desbloqueado sin saberlo; las credenciales modernas de 13,56 MHz con autenticación mutua y cifrado resisten esto, mientras que las tarjetas de 125 kHz no cifradas generalmente no. El anti-retorno es un control de política que evita que una sola credencial se use para entrar dos veces sin una salida intermedia, lo que impide que una credencial circule entre varias personas; requiere datos de salida confiables y un diseño cuidadoso para evitar bloquear a usuarios legítimos durante aglomeraciones o errores de configuración. Cada uno de estos controles debe especificarse, configurarse y probarse en lugar de asumirse desde el marketing de la plataforma.
Manipulación física y el servidor de gestión
La capa física es a menudo la más débil. Los lectores, las cajas de cerradura y los controladores están expuestos y pueden ser forzados, cortocircuitados o evadidos, por lo que los interruptores de manipulación, los gabinetes sellados, el cableado oculto y la monitorización de posición de puerta importan. Una puerta es tan fuerte como su elemento más débil, y un lector montado en superficie sobre una cerradura barata con un pestillo largo es una falla común. El servidor de gestión es un objetivo separado y de alto valor: si un atacante obtiene control administrativo de la plataforma, puede otorgarse acceso a todas partes, por lo que el servidor debe estar parcheado, segregado en su propio segmento de red, protegido con credenciales fuertes y rotadas, monitorizado para detectar intrusiones y respaldado para que su integridad pueda verificarse después de un incidente. Un modelo de amenaza que trata al servidor como una joya de la corona y a la red como una posible ruta es lo que convierte un sistema de control de acceso comercial de una conveniencia en un control creíble.
Guía de Sistemas de Control de Acceso Comercial — Integración y Apertura
Un sistema de control de acceso comercial alcanza su valor completo solo cuando se conecta con el resto del edificio y la organización. Las integraciones comunes incluyen gestión de video y verificación en un evento de alarma, gestión de visitantes y lobby, control de ascensores y torniquetes, directorio de RR. HH. o identidad, sistemas de gestión de edificios y paneles de incendio o alarma. La profundidad de la integración se decide antes de la adquisición: qué eventos fluyen a qué sistema, si la interfaz es una API abierta o un bloqueo propietario, quién mantiene cada conexión cuando cualquiera de los sistemas se actualiza, y cómo se correlacionan los eventos para una auditoría precisa. Wiegand, OSDP y RS-485 siguen siendo comunes en el borde, ascendiendo a IP y REST o integración API hacia arriba, con mensajería impulsada por eventos donde se necesita correlación en tiempo casi real. Una subintegración obliga a la conciliación manual de eventos entre sistemas, mientras que una sobreintegración licencia funciones que la instalación nunca usa, por lo que el alcance de la integración es una decisión deliberada tomada contra los flujos de trabajo reales del sitio, no un ejercicio de recuento de funciones.
Confirme la propiedad de cada integración en el momento del contrato. La plataforma de acceso, el controlador de ascensores y el servidor de video se actualizarán cada uno, y el mantenimiento de sus conexiones suele ser la primera responsabilidad en desaparecer.
Protocolos de borde: Wiegand, OSDP, RS-485
El enlace físico entre un lector y su controlador es donde comienza la apertura. Wiegand es un estándar de cableado de larga data que transporta un identificador de credencial a través de un pequeño número de cables de datos; es simple y omnipresente, pero no está cifrado y es unidireccional, lo que lo hace vulnerable a la interceptación y limita la capacidad del lector para autenticar al controlador o recibir configuración. OSDP, el Protocolo Abierto Supervisado de Dispositivos, fue diseñado para abordar estas brechas: proporciona comunicación cifrada, supervisada y bidireccional entre lector y controlador sobre un bus RS-485, añade informes de manipulación y supervisión, y es cada vez más el reemplazo recomendado para Wiegand en nuevos sistemas de control de acceso comercial. RS-485 sigue siendo el transporte preferido para el cableado multi-caída a lectores y periféricos sobre distancias moderadas. Elegir lectores y controladores compatibles con OSDP, y cablear para RS-485 donde sea factible, compra mejor seguridad y flexibilidad futura por una prima de hardware modesta.
Integración ascendente: APIs, correlación de eventos e identidad
Por encima del borde, los sistemas de control de acceso comercial se integran hacia arriba a través de IP e interfaces de aplicación. Una plataforma bien diseñada expone una API que permite que un sistema de visitantes cree credenciales temporales, que un sistema de video obtenga eventos de puerta para verificación de alarmas, y que un directorio de RR. HH. empuje y extraiga cambios de identidad para que la terminación revoque automáticamente el acceso. El valor de estas integraciones depende de la correlación de eventos: hacer coincidir una alarma de puerta con la cámara de video que la cubre, o vincular un deslizamiento de credencial con la persona en el registro de visitantes, es lo que convierte los eventos crudos en un registro listo para investigaciones. Al comparar plataformas, pregunte qué eventos se exponen, en qué formato, con qué programación y con qué control de acceso, y pruebe una integración representativa en un piloto en lugar de asumir que el conector anunciado funciona. La integración que está diseñada, documentada y es propiedad de alguien supera a la integración que existe solo en un folleto.
Apertura versus bloqueo
La profundidad de la integración fuerza una decisión estratégica sobre la apertura. Los sistemas propietarios y cerrados pueden ser más simples de implementar y estar respaldados por un solo proveedor, pero bloquean al sitio en la hoja de ruta, los precios y el ciclo de actualización de ese proveedor, y dificultan la conexión posterior de productos de video, identidad o automatización de edificios de primer nivel. Los sistemas abiertos que utilizan protocolos estándar y APIs documentadas mantienen abiertas las opciones de adquisición y hacen que la plataforma de acceso sea un activo en lugar de un rehén, pero colocan más responsabilidad de integración en el integrador o el equipo de la instalación. El camino pragmático es exigir interfaces documentadas y no destructivas y un compromiso de respaldarlas a través de las actualizaciones, y escribir la propiedad de la integración en el contrato para que cuando el controlador de ascensores o el servidor de video cambie, la conexión entre ellos sea responsabilidad explícita de alguien. La subintegración causa conciliación manual y deriva; la sobreintegración compra funciones que nadie usa — la decisión trata sobre lo que la instalación realmente necesita.
Guía de Sistemas de Control de Acceso Comercial — Alimentación, Salida y Seguridad Humana
El comportamiento de alimentación y salida determina lo que hace el sistema cuando falla la electricidad o la red. Un sistema de control de acceso comercial debe definir puertas de seguridad ante fallos que se desbloquean ante la pérdida de energía — apropiadas para rutas de salida públicas — versus puertas seguras ante fallos que permanecen bloqueadas para la seguridad perimetral, y debe especificar batería o suministro de alimentación ininterrumpida para controladores, lectores y cerraduras para que la pista de auditoría y la toma de decisiones sobrevivan a una interrupción. Los códigos locales de construcción, incendio y accesibilidad rigen la salida libre, el hardware de pánico, la señal en la puerta y las características de salida retardada, y esas determinaciones pertenecen a un profesional calificado para la ocupación y jurisdicción específicas. El sistema nunca debe permitir que un método conveniente de control en horario normal anule la ruta libre obligatoria a la seguridad cuando la energía o la red no están disponibles. El comportamiento de salida se valida contra el plan de emergencia real y el perfil de ocupantes de la instalación, no contra una suposición genérica.
Elija hardware de seguridad ante fallos para cualquier abertura que no pueda tolerar encerrar a personas durante una emergencia, y pruebe ese comportamiento con el plan de emergencia real. Una puerta que no se libera bajo una interrupción simulada falla al sitio, por fuerte que sea el resto del sistema.
Seguridad ante fallos versus seguridad ante fallos de bloqueo
Cada abertura electrificada en un sistema de control de acceso comercial debe clasificarse por su comportamiento ante la pérdida de energía. Una abertura de seguridad ante fallos se desbloquea cuando se elimina la energía, lo que es apropiado donde las personas deben poder salir sin demora en una emergencia, como rutas de salida públicas, puertas de escalera y salidas que conducen a la seguridad. Una abertura segura ante fallos se bloquea cuando se elimina la energía, lo que es apropiado para puertas perimetrales y de alta seguridad donde mantener al intruso fuera importa más que la conveniencia y donde existe una ruta de salida libre alternativa. Esto no es un valor predeterminado que pueda dejar al proveedor de hardware; es una decisión deliberada y documentada tomada por abertura contra el plan de emergencia y los requisitos del código del sitio. Equivocarse en una dirección puede encerrar a personas durante una emergencia, y equivocarse en la otra puede dejar un perímetro desbloqueado durante un apagón, por lo que la clasificación pertenece al cronograma de puertas y se verifica durante la puesta en marcha.
Provisión de alimentación y suministro ininterrumpido
Los sistemas de control de acceso comercial confiables dependen de una alimentación confiable para los controladores, lectores, cerraduras y el servidor de gestión. Los controladores deben alimentarse de un suministro protegido, idealmente un circuito dedicado con provisión de alimentación ininterrumpida dimensionada para soportar la interrupción más larga esperada, para que la toma de decisiones y la pista de auditoría sobrevivan. Las cerraduras de borde a batería intercambian el cableado por una carga recurrente de monitorear, programar y reemplazar baterías, y su carga restante y las alertas de batería baja deben gestionarse activamente o las puertas se desconectan silenciosamente. Los lectores y las cerraduras eléctricas necesitan alimentación adecuada y regulada, y los tendidos de cable largos deben verificarse por caída de voltaje para que el hardware funcione dentro de la especificación. El diseño de alimentación es parte del diagrama de arquitectura y las pruebas de puesta en marcha, no una ocurrencia tardía dejada a quien instala las puertas.
Salida, hardware de pánico y salida retardada
La seguridad humana gobierna cómo salen las personas, y los sistemas de control de acceso comercial nunca deben obstruir la ruta libre obligatoria. La salida libre significa que los ocupantes pueden salir sin una credencial de acceso, un acto deliberado o una demora, lo que generalmente se traduce en hardware de seguridad ante fallos, solicitud de salida y monitorización de posición de puerta, y hardware de pánico como barras de empuje en rutas públicas. Algunas jurisdicciones permiten sistemas de salida retardada que mantienen una puerta durante una breve demora con alarma audible antes de la liberación, pero solo bajo condiciones definidas y después de una aprobación calificada, y nunca son aceptables donde se requiere una ruta libre inmediata. Los dispositivos de solicitud de salida permiten que las puertas se abran desde adentro sin registrar una alarma, pero una puerta que se mantiene abierta más allá de un tiempo de espera debe alarmar para que una puerta apuntalada no pueda usarse para seguimiento o contrabando. Cada decisión de salida se valida contra el plan de emergencia real, el perfil de ocupantes y el código local de la instalación por un profesional calificado, y el sistema se prueba luego para demostrar que la puerta realmente se libera cuando debe.
Guía de Sistemas de Control de Acceso Comercial — Puesta en Marcha e Implementación en el Sitio
La puesta en marcha y la implementación deciden si un diseño sólido se convierte en un sistema confiable. Un sistema de control de acceso comercial se pone en marcha verificando que cada lector lea y rechace las credenciales correctas, que cada controlador se comporte correctamente en línea y fuera de línea, que el comportamiento de seguridad ante fallos o bloqueo de cada puerta se confirme bajo pérdida simulada de alimentación y red, y que la plataforma de software informe los eventos esperados a los monitores correctos. Las pruebas se ejecutan en puertas representativas y se repiten después de la instalación, con las suposiciones registradas y aceptadas en una firma formal por parte del operador. La entrega incluye diagramas de cableado y red, una guía de administración de credenciales, configuraciones de monitores y alertas, y un procedimiento de recuperación probado para que el sitio pueda funcionar sin el proveedor. Pilotar un piso o un área funcional antes de una implementación completa revela problemas de integración y operación a bajo costo, y descubre fallas que ningún banco de pruebas expondría, antes de que los ocupantes dependan del sistema a diario.
Otorgue a la autoridad de puesta en marcha el poder de detener el reloj ante una prueba fallida. Un lector que rechaza una credencial válida, una alarma que no llega al monitor correcto o una puerta que se traba bajo presión debe fallar la puesta en marcha en lugar de fallar al personal un lunes.
El plan de pruebas de puesta en marcha
La puesta en marcha es un plan de pruebas formal, no un recorrido. El plan debe cubrir pruebas funcionales, como presentar credenciales válidas e inválidas y confirmar que la puerta se abre o permanece bloqueada y que el evento se registra correctamente. Debe cubrir pruebas de rendimiento, como la rapidez con que se libera la puerta y si el lector responde dentro de la tolerancia del operador. Debe cubrir pruebas de comportamiento ante fallas, confirmando la acción de seguridad ante fallos o bloqueo de cada puerta cuando se corta la alimentación y cómo se comporta el controlador cuando cae la red, y debe cubrir pruebas de integración, confirmando que un evento de alarma llega al monitor de video correcto, que una revocación llega a cada puerta y que la terminación de RR. HH. fluye a través de la integración de identidad. Cada prueba se registra con un aprobado o reprobado y un responsable, y la suite completa se repite en una muestra representativa de cada tipo de hardware en lugar de asumir que se comporta de manera idéntica en todo el sitio.
Documentación de entrega y preparación del operador
La entrega es donde el proveedor se detiene y el operador comienza, y falla cuando se reduce a un juego de llaves y una sesión informativa verbal. La documentación completa de entrega para un sistema de control de acceso comercial incluye el diagrama de arquitectura, diagramas de cableado y red, un cronograma de puertas con la clasificación de seguridad ante fallos o bloqueo y los tipos de dispositivos, una guía de administración de credenciales, configuraciones de monitores y alertas, un plan de repuestos y mantenimiento, y un procedimiento de recuperación probado para que el sitio pueda operar y solucionar problemas sin llamar al proveedor para eventos rutinarios. La preparación del operador significa que las personas que gestionarán usuarios, responderán a alarmas y manejarán bloqueos han sido capacitadas y han practicado el procedimiento de recuperación. Un sitio que no puede operar su propio sistema de acceso durante un día es un sitio que no ha sido realmente entregado, diga lo que diga el formulario de aceptación firmado.
Pilotaje antes de la implementación completa
Una implementación por fases protege a los ocupantes y al presupuesto. Antes de convertir todo el sitio, ejecute un piloto en un piso, un ala o un área funcional que incluya una mezcla representativa de tipos de puertas, tipos de credenciales e integraciones, y conviva con él bajo condiciones reales. El piloto revela fallas de integración, fricción operativa, carga de trabajo del administrador, falsas alarmas y problemas de batería o alimentación que nunca aparecen en un banco de pruebas, y lo hace a bajo costo mientras solo una población pequeña se ve afectada. Mida el piloto contra el registro de decisiones de la fase de diseño, corrija lo que se rompe y solo entonces escale al resto del sitio. Un sistema de control de acceso comercial que se ha probado en un piloto tiene muchas más probabilidades de ganarse la confianza de los ocupantes y el personal de seguridad desde el primer día de la implementación completa.
Guía de Sistemas de Control de Acceso Comercial — Costo de Ciclo de Vida y Debida Diligencia del Proveedor
El costo de ciclo de vida de un sistema de control de acceso comercial es el total de hardware, instalación, administración de credenciales, mantenimiento, licencias, actualizaciones de software y firmware, capacitación, energía y reemplazo eventual — no el precio por puerta. Los sistemas en línea conllevan cableado, red, servidor y gastos generales de licencias; los sistemas híbridos o a batería añaden carga recurrente de baterías y monitoreo; y la integración profunda añade obligaciones de mantenimiento en las plataformas conectadas. La propiedad del mantenimiento debe asignarse antes de la compra: quién gestiona usuarios, actualiza firmware, reemplaza lectores y baterías, responde a bloqueos, y qué repuestos se almacenan. La debida diligencia verifica las certificaciones del proveedor, la documentación específica del modelo actual, la evidencia de pruebas, la ruta de soporte designada, el tiempo de respuesta y los términos de garantía en lugar de confiar en las afirmaciones de marketing. Solicitar esos elementos por escrito revela si el proveedor será un socio durante la vida útil del sistema o simplemente un vendedor. El consumo de energía es pequeño por dispositivo, pero real en un gran número de puertas, y pertenece al modelo como cualquier otra partida.
Solicite registros de certificación por modelo y un plan escrito de repuestos y fin de vida útil. Un controlador o lector que queda sin soporte a mitad de contrato se convierte en un pasivo de seguridad y mantenimiento que el comprador hereda, así que confirme la hoja de ruta antes de comprometerse.
Costo total de propiedad más allá del precio de etiqueta
El precio por puerta en una cotización es la parte más pequeña del costo de por vida. Las partidas más grandes suelen ser la instalación, incluidos cableado, red, montaje y mano de obra; la administración continua, porque cada inscripción, cambio y revocación toma el tiempo de una persona calificada; el mantenimiento, las actualizaciones de firmware y los reemplazos; las tarifas de licencia o software que se repiten anualmente; y la capacitación y la energía. Los dispositivos a batería trasladan el costo del cableado a un flujo interminable de reemplazo de baterías, y la mano de obra de alcanzar, reemplazar y registrar esas baterías es fácil de subestimar. La integración profunda añade mantenimiento en cada sistema conectado, porque cada actualización de la plataforma de video, identidad o construcción puede romper la integración que nunca tuvo un propietario asignado. Construir un modelo de costos a diez años que capture todo esto es lo que separa un presupuesto defendible de una sorpresa agradable en el año tres.
Debida diligencia del proveedor
La evaluación del proveedor merece el mismo rigor que la comparación de hardware. Solicite y revise los registros de certificación, como la conformidad con los estándares de compatibilidad electromagnética, seguridad y radio que sean apropiados para el mercado y las tecnologías de radio utilizadas. Solicite documentación específica del modelo actual en lugar de folletos genéricos, y evidencia de pruebas que demuestre las características anunciadas y los comportamientos de seguridad en condiciones realistas. Confirme una ruta de soporte designada, un tiempo de respuesta declarado y los términos de la garantía, y pregunte cómo se entregan las actualizaciones de firmware y durante cuánto tiempo se admite cada modelo. Un proveedor que no puede o no quiere responder estas preguntas por escrito está señalando cómo se comportará una vez firmada la compra. La debida diligencia no es desconfianza; es el comprador estableciendo que el proveedor será un socio durante la vida útil del sistema en lugar de simplemente un vendedor.
Contexto de certificación y cumplimiento
Las certificaciones importan para la implementación, el seguro y el acceso al mercado, pero deben leerse correctamente. Las marcas de conformidad abordan la seguridad y la compatibilidad electromagnética del hardware en sí; no garantizan por sí solas que una instalación cumpla con las obligaciones de construcción, incendio, accesibilidad o ciberseguridad que se aplican a una ocupación y jurisdicción particular. Los lectores y credenciales con certificación de radio son necesarios para operar legalmente en cada mercado, y el comprador debe confirmar las aprobaciones de frecuencia específicas para los productos que se compran. La certificación de ciberseguridad de la plataforma, si se afirma, debe evidenciarse con documentos que describan el alcance y los controles evaluados. Los profesionales calificados del comprador siguen siendo responsables de confirmar que el sistema configurado satisface los códigos y regulaciones locales; la marca de hardware es necesaria pero nunca suficiente por sí sola.
Guía de Sistemas de Control de Acceso Comercial — Lista de Verificación de Implementación
Un proyecto confiable de sistema de control de acceso comercial sigue una secuencia repetible: estudie las puertas y las rutas de cableado; defina el modelo de amenaza y la política de acceso; diseñe el ciclo de vida de identidad y credenciales; elija la arquitectura y la profundidad de integración; resuelva la alimentación, el comportamiento de seguridad ante fallos o bloqueo y el cumplimiento de seguridad humana; ponga en marcha y acepte en puertas representativas; y entregue con capacitación, propiedad de mantenimiento, repuestos y procedimientos de recuperación. Cada paso cierra con un registro de decisiones y los elementos abiertos se resuelven antes de la siguiente fase. Pilote la configuración elegida en un piso o área funcional antes de una implementación en todo el sitio, mida contra el registro de decisiones y solo entonces escale. Esta guía es educativa y no sustituye la revisión legal, de incendio, accesibilidad, ciberseguridad o ingeniería calificada, así que confirme cada requisito con profesionales calificados para la ubicación y ocupación exactas, y registre esas confirmaciones en el registro de decisiones junto con cada otra fase.
La secuencia de decisiones
Una secuencia de implementación viable mantiene las decisiones en un orden donde cada una alimenta a la siguiente. Comience estudiando cada abertura, su función, su acceso a alimentación y cable, y el valor que protege, y capture esto en un cronograma de puertas. Del cronograma de puertas, construya el modelo de amenaza y la política de acceso, asignando a cada abertura una clasificación que impulse cuánta seguridad, monitoreo y control necesita. Diseñe el ciclo de vida de identidad y credenciales a continuación, porque el número de personas, la rotación y los tipos de credenciales dan forma a la plataforma y al esfuerzo de administración. Solo entonces elija la arquitectura, la profundidad de integración, el comportamiento de alimentación y seguridad ante fallos o bloqueo, y el cumplimiento de seguridad humana, porque estos dependen de las decisiones anteriores. Finalmente, planifique la puesta en marcha, la aceptación, la entrega y el mantenimiento antes de que el sistema se instale, para que el sitio esté listo para operar el sistema desde el primer día.
Escribiendo un registro de decisiones
Un proyecto de sistema de control de acceso comercial debe guiarse por un registro de decisiones escrito, porque la memoria y la rotación del personal desharán el diseño. Para cada fase, registre la decisión, la justificación, las alternativas consideradas y los elementos abiertos que permanecen, y manténgalo actualizado a medida que el sitio evoluciona. El registro de decisiones es la referencia contra la cual se mide el piloto y se juzga la aceptación eventual, y es el documento que un nuevo gerente de seguridad lee para entender por qué el sistema se comporta de la manera en que lo hace. Sin él, una puerta reclasificada en una emergencia, un tipo de credencial silenciosamente abandonado o una decisión de seguridad ante fallos revertida por sugerencia de un contratista pueden erosionar el diseño sin que nadie lo note hasta un incidente. El registro de decisiones es barato de mantener e invaluable cuando algo sale mal.
Confirmando con profesionales calificados
Ninguna guía de planificación puede sustituir las revisiones profesionales que requiere una instalación real. Profesionales calificados en derecho, incendio, accesibilidad, ciberseguridad e ingeniería deben confirmar que el sistema de control de acceso comercial elegido satisface los requisitos de la ubicación y ocupación exactas, incluidos los códigos locales de construcción e incendio, las obligaciones de accesibilidad y los compromisos de seguridad y protección de datos de la instalación. Esto es particularmente cierto para las características de salida y seguridad humana, la salida retardada, el hardware de pánico y la segregación de la red de acceso. El material educativo en esta guía está destinado a enmarcar las preguntas y estructurar el proyecto, no a sustituir esa revisión. Presupuestar tiempo y dinero para estas revisiones, y tratar sus hallazgos como requisitos, es lo que mantiene un sistema bien planificado legal y defendible.
Guía de Sistemas de Control de Acceso Comercial — Clasificación de Aberturas por Grado de Seguridad
Un sistema de control de acceso comercial práctico trata las aberturas de manera diferente según lo que protegen, en lugar de aplicar el mismo control a cada puerta. La clasificación asigna a cada abertura un grado de seguridad que impulsa su lector, hardware de bloqueo, monitoreo y política, y es una de las decisiones más tempranas del proyecto porque todo lo downstream, desde la selección de hardware hasta la puesta en marcha, depende de ella. Una entrada de lobby que enfrenta la calle, un corredor solo para personal en el interior de un piso y una sala de servidores que contiene registros de clientes simplemente no enfrentan el mismo riesgo, y aplicar el mismo control a cada una desperdicia presupuesto sobreprotegiendo una puerta de bajo valor o deja una puerta de alto valor inadecuadamente defendida. Escribir la clasificación en el cronograma de puertas hace que el razonamiento sea explícito, revisable y consistente con el modelo de amenaza, concentrando el presupuesto y el esfuerzo de monitoreo donde el riesgo residual se reduce genuinamente.
Aberturas perimetrales, interiores y de alta seguridad
Las aberturas en un sistema de control de acceso comercial caen en clases amplias que conllevan diferentes expectativas. Las aberturas perimetrales, como la entrada principal, las puertas de servicio y los muelles de carga, enfrentan al mundo exterior y la mayor exposición, por lo que generalmente necesitan bloqueo robusto, colocación cuidadosa del lector, cobertura de video y revocación estricta. Las aberturas interiores, como puertas de oficinas, salas de reuniones, almacenes y personal, protegen la conveniencia y los límites internos, y a menudo equilibran la seguridad contra la fricción del movimiento normal. Las aberturas de alta seguridad, como salas de servidores, farmacias, manejo de efectivo, laboratorios y salas de máquinas, protegen activos que justifican controles más pesados, incluidos cerraduras más fuertes, detección de manipulación, diversidad de credenciales, verificación por video, anti-retorno y monitoreo de alarmas. Escribir una clasificación para cada abertura en el cronograma de puertas es lo que hace que el resto del diseño sea proporcionado en lugar de uniforme.
Qué impulsa el grado
Varios factores impulsan el grado de seguridad de una abertura. El valor del activo detrás de la puerta es el impulsor principal, ya sea que ese activo sean datos, inventario, efectivo, equipo o la seguridad de las personas. La exposición de la abertura al contacto no autorizado importa, porque una puerta exterior o una en un corredor público ve más intentos que una puerta en el interior de un piso. Las consecuencias de la entrada no autorizada, incluidos los impactos regulatorios, financieros, de seguridad y reputacionales, elevan el grado. Y el patrón de tráfico legítimo, es decir, con qué frecuencia las personas necesitan pasar y cuánta fricción es aceptable, limita cuán estrictos pueden ser los controles sin paralizar la operación. La combinación de estos factores produce un pequeño conjunto de grados — por ejemplo, estándar, mejorado y alta seguridad — que se mapean limpiamente en las elecciones de hardware y políticas.
Convirtiendo la clasificación en requisitos
Una vez que las aberturas están clasificadas, la clasificación se traduce directamente en requisitos en el cronograma de puertas. Una abertura de grado estándar podría usar un lector de tarjeta inteligente, una cerradura comercial sólida y un dispositivo de solicitud de salida con monitoreo. Una abertura de grado mejorado añade verificación por video, lectores resistentes a manipulación, un monitor de posición de puerta con alarma de puerta abierta y posiblemente un requisito de credencial en la salida. Una abertura de alta seguridad añade anti-retorno, cableado de lector segregado, bloqueo más fuerte, verificación de credencial más PIN o biométrica, e integración con monitoreo de alarmas para que una entrada forzada se escale inmediatamente. Presentar la clasificación como una tabla en los documentos de diseño hace que todo el sistema sea más fácil de revisar, costear y aceptar, y mantiene el presupuesto de monitoreo donde el riesgo residual se reduce genuinamente.
Guía de Sistemas de Control de Acceso Comercial — Cerraduras Cableadas Versus Inalámbricas y a Batería
La elección entre aberturas cableadas e inalámbricas es una de las decisiones más trascendentales en un sistema de control de acceso comercial porque intercambia el costo del cableado contra la alimentación, la confiabilidad y la carga administrativa, y ninguna respuesta única se ajusta a cada puerta. Una abertura cableada mantiene alimentación y datos continuos fluyendo a la cerradura, lo que permite un bloqueo más pesado, eventos y revocación en tiempo casi real, y una huella de mantenimiento menor una vez instalada, pero conlleva el costo del tendido de cable en sí. Una abertura inalámbrica a batería evita el cableado invasivo, lo que es atractivo en edificios arrendados o históricos y para puertas interiores de bajo tráfico, pero introduce un ciclo de vida recurrente de baterías y una demora en la rapidez con que la política y la revocación llegan a la puerta. Entender estas compensaciones por abertura, en lugar de elegir un enfoque para todo el sitio, es lo que produce un híbrido sensato y económico.
Cuándo ganan las aberturas cableadas
Una abertura cableada mantiene alimentación y datos fluyendo a la cerradura continuamente, lo que compra varias ventajas. El hardware electrificado cableado puede usar bloqueo de servicio más pesado que consume más corriente, porque la alimentación no tiene que conservarse para una batería. Los lectores y controladores cableados se comunican a través de la red, por lo que los eventos fluyen en tiempo casi real y las actualizaciones de política y revocación se propagan inmediatamente, lo que importa para aberturas de alta seguridad y perimetrales. Las aberturas cableadas no dependen de baterías que se agotan y deben rastrearse, por lo que su mantenimiento es menor una vez instaladas, y es más probable que mantengan una pista de auditoría completa incluso a través de una interrupción sostenida si el controlador está en un suministro protegido. Para aberturas de alto tráfico, alta seguridad o de difícil acceso, el mayor costo de instalación del cableado generalmente se justifica por las características operativas superiores.
Cuándo tienen sentido las cerraduras inalámbricas y a batería
Las cerraduras inalámbricas a batería se vuelven atractivas donde el cableado es impracticable o antieconómico. Esto incluye remodelaciones en edificios históricos o arrendados donde tender cable es invasivo, puertas interiores de bajo tráfico cuya conveniencia no justifica un tendido de cable, y pisos de inquilinos o multi-inquilinos donde el propietario no quiere trabajo estructural. Las cerraduras a batería intercambian la alimentación continua y el comportamiento instantáneo en línea por un menor costo de instalación, pero introducen un ciclo de vida recurrente de baterías: las baterías se agotan a diferentes ritmos por puerta, las alertas de batería baja deben monitorearse, y una puerta que silenciosamente se queda sin carga puede desconectarse o fallar al liberarse. Las cerraduras inalámbricas modernas usan radios de baja potencia y sincronización programada para mantener la política razonablemente actualizada, pero la revocación a una puerta a batería no es instantánea. Son un buen ajuste para las aberturas correctas y un mal ajuste para las de alta seguridad o alto tráfico.
Construyendo el híbrido y planificando el deber de batería
La mayoría de los sitios terminan con un híbrido: aberturas cableadas para el perímetro, las áreas de alta seguridad y los carriles de tráfico ocupados, y cerraduras inalámbricas a batería para las puertas interiores de bajo tráfico donde un tendido de cable cuesta más de lo que vale. Planificar el híbrido significa decidir por abertura en lugar de por línea de productos, y significa diseñar el deber de batería antes de la compra. Ese deber incluye estimar los intervalos de reemplazo por tipo de puerta, definir cómo las alertas de batería baja llegan a la persona correcta, programar las rondas de reemplazo y almacenar el tipo de batería correcto. Una abertura inalámbrica es tan confiable como el programa de baterías que la respalda, por lo que un sitio que elige cerraduras a batería también debe elegir poseer el ciclo de vida de las baterías. Documentar la mezcla cableada e inalámbrica en el diagrama de arquitectura y el cronograma de puertas mantiene la decisión explícita y el plan de mantenimiento realista.
Guía de Sistemas de Control de Acceso Comercial — Dimensionamiento de Controladores y Cableado
Los controladores son el corazón de toma de decisiones de un sistema de control de acceso comercial, y dimensionarlos correctamente con su cableado previene tanto capacidad desperdiciada como retrabajo vergonzoso. Cada controlador soporta un número limitado de lectores y entradas y salidas, por lo que su población se deriva del cronograma de puertas en lugar de adivinarse, porque cada puerta consume un lector y a menudo un dispositivo de solicitud de salida, un monitor de posición de puerta, un relé de bloqueo y a veces también un segundo lector. El alcance del cableado importa porque los controladores deben estar lo suficientemente cerca de sus puertas para que el cableado del lector y la cerradura funcione confiablemente, y los tendidos largos añaden costo y caída de voltaje que pueden sacar al hardware de la especificación. La población de controladores se dimensiona luego con margen para el crecimiento, ya que agregar una puerta después es trivial con capacidad de sobra pero costoso cuando significa un nuevo controlador y un nuevo tendido de cable, por lo que un cronograma de puertas superpuesto a un plano de planta es la materia prima para el dimensionamiento antes de ordenar cualquier hardware.
Dimensionando la población de controladores
Un controlador soporta un número limitado de lectores y entradas y salidas, por lo que el recuento de controladores se deriva del cronograma de puertas en lugar de adivinarse. Cada puerta necesita un lector, y muchas necesitan un dispositivo de solicitud de salida, un monitor de posición de puerta, un relé de bloqueo y a veces un segundo lector para una configuración de esclusa o tarjeta en salida, y todos estos consumen entradas y salidas en el controlador. El alcance del cableado importa porque los controladores deben estar físicamente lo suficientemente cerca de sus puertas para que el cableado del lector y la cerradura funcione confiablemente, y porque los tendidos largos añaden costo y caída de voltaje. La población de controladores se dimensiona luego con margen para el crecimiento, porque agregar una puerta después es trivial si el controlador tiene capacidad de sobra y costoso si significa instalar un nuevo controlador y un nuevo tendido de cable. Un cronograma de puertas superpuesto a un plano de planta es la materia prima para este dimensionamiento, y debe hacerse antes de ordenar cualquier hardware.
Cableado para alimentación, datos y lectores
El cableado conlleva tres responsabilidades distintas que son fáciles de confundir. El cableado de alimentación alimenta las cerraduras, los pestillos y los lectores, y debe dimensionarse para el consumo de corriente de los dispositivos y verificarse por caída de voltaje sobre la longitud del tendido. El cableado de datos transporta la red de regreso a los controladores y al servidor de gestión, y debe llegar a los lugares donde están instalados los controladores y donde la red está disponible. El cableado de lectores conecta cada lector a su controlador, y en instalaciones OSDP es un bus RS-485 que también transporta supervisión y cifrado. El cableado que se tiende una vez y se oculta es costoso de retrabajar, por lo que el estudio debe mapear las rutas reales, identificar los conductos y puntos de acceso, y señalar aberturas donde falta una ruta limpia de alimentación y datos. Hacer bien el cableado en la fase de planificación es lo que convierte una implementación fluida en un trabajo rutinario en lugar de una sorpresa en la fase de construcción.
Controladores fuera de línea y la cuestión de la resiliencia
Debido a que los controladores mantienen las decisiones locales, su resiliencia durante una interrupción de red determina cómo se comporta el sitio cuando falla la LAN. Un controlador con caché de política local continúa aplicando horarios y permitiendo o denegando credenciales incluso cuando no puede alcanzar al servidor de gestión, lo que mantiene el sitio funcionando durante una interrupción; un controlador sin caché puede dejar de decidir por completo y fallar abierto o cerrado según la configuración. La política fuera de línea — cuánto tiempo permanecen válidas las credenciales obsoletas, si los eventos fuera de línea se almacenan en búfer y se cargan después, y si la puerta falla segura o bloqueada — debe especificarse y probarse para cada controlador. Los diseñadores también deben considerar alimentación redundante para los controladores y, donde el riesgo lo justifique, rutas de red redundantes para que una sola falla de conmutador o cable no deshabilite un ala completa. La resiliencia de la capa de controladores es la resiliencia del sistema de control de acceso comercial en su conjunto.
Guía de Sistemas de Control de Acceso Comercial — El Servidor de Gestión y la Ciberseguridad de TI
El servidor de gestión concentra el valor de un sistema de control de acceso comercial en un solo objetivo de alto valor, por lo que su seguridad y la seguridad de la red de acceso merecen la misma atención que las puertas mismas. Un compromiso del servidor es un compromiso de cada puerta que gestiona, porque el control administrativo sobre la plataforma otorga acceso a todo el sitio, por lo que el servidor, su sistema operativo y su base de datos se tratan como joyas de la corona. Eso significa colocar la red de acceso en su propio segmento segregado con conectividad controlada a la LAN corporativa, para que una infección que comienza en otro lugar no pueda alcanzar los controladores o la consola de gestión sin cruzar un límite monitoreado. Significa credenciales administrativas fuertes, únicas y rotadas con autenticación multifactor y roles de menor privilegio, parcheo en un cronograma definido, y respaldos que se prueban restaurándolos realmente. Monitorear la actividad administrativa y alertar sobre inicios de sesión fallidos y cambios de configuración inesperados convierte a la plataforma en un activo defendido en lugar de una consola abierta.
Segregando la red de acceso
La red de control de acceso debe tratarse como un segmento sensible en lugar de solo otra parte de la LAN de oficina. Los datos de credenciales, los registros de auditoría y las credenciales administrativas son valiosos, y los lectores y controladores son dispositivos físicos que pueden sondearse, por lo que la red de acceso a menudo se coloca en su propia VLAN o segmento de red con conectividad firewalled y restringida a la red corporativa. Un compromiso que comienza en una estación de trabajo infectada no debería poder alcanzar los controladores de acceso o el servidor de gestión sin cruzar un límite controlado. Esta segregación también limita el radio de explosión de un dispositivo mal configurado y hace que el monitoreo del segmento de acceso sea más significativo. La decisión de segregar, y las reglas que gobiernan el límite, pertenecen al diagrama de arquitectura y a la revisión de ciberseguridad, no a una ocurrencia tardía.
Asegurando la plataforma de gestión
La plataforma de gestión es donde los administradores cambian el acceso, por lo que su autenticación y control de acceso son críticos. Las cuentas administrativas deben usar credenciales fuertes, únicas y rotadas, con autenticación multifactor donde la plataforma lo soporte, y roles de menor privilegio que separen quién puede otorgar acceso de quién solo ve eventos. La plataforma y su sistema operativo deben parchearse en un cronograma definido, con actualizaciones de firmware aplicadas a los controladores y lectores a medida que se lanzan y prueban. Los respaldos de la base de datos de acceso y la configuración deben tomarse regularmente, almacenarse de forma segura y probarse restaurándolos realmente, porque una plataforma que no puede recuperarse es una plataforma que no puede confiarse después de un incidente. Monitorear la actividad administrativa y alertar sobre inicios de sesión fallidos y cambios de configuración inesperados convierte a la plataforma de gestión en un activo defendido en lugar de una consola abierta.
Protección de datos e integridad de auditoría
Un sistema de control de acceso comercial contiene datos personales sobre quién entró dónde y cuándo, lo que conlleva obligaciones de privacidad además de las de seguridad. Los registros de acceso deben retenerse según una política documentada, protegerse en reposo y en tránsito, y ser accesibles solo para aquellos con una necesidad legítima, y la plataforma debe registrar los cambios en su propia configuración para que un investigador pueda confiar en la pista de auditoría. La integridad del registro de auditoría importa porque su propósito completo es ser creído después; los registros que pueden editarse silenciosamente, o cuyo servidor puede manipularse sin ser notado, tienen poco valor probatorio. La segregación, el parcheo, la administración fuerte y la protección de registros juntos son lo que mantienen al servidor de gestión y los datos que contiene defendibles, y son tanto parte del diseño como los lectores y cerraduras en las puertas.
Guía de Sistemas de Control de Acceso Comercial — Operación Multi-Inquilino y Multi-Sitio
A menudo se espera que los sistemas de control de acceso comercial sirvan a más de una organización y más de un edificio desde una sola plataforma, y esa responsabilidad multi-inquilino y multi-sitio añade una capa de administración y seguridad que las implementaciones de un solo edificio no enfrentan. En un edificio multi-inquilino, la plataforma debe permitir que cada inquilino gestione a su propia gente y sus propias puertas mientras un operador del edificio mantiene el control general, lo que exige separación basada en roles para que los administradores de un inquilino no puedan cambiar el acceso de otro, una pista de auditoría que atribuya los cambios al administrador correcto, y reglas claras sobre espacios compartidos como lobbies, vestíbulos de ascensores, baños y áreas de servicio. El ciclo de vida de identidad también debe absorber la rotación de inquilinos, porque los inquilinos entran y salen y la rotación de su personal es suya para gestionar, mientras que la revocación a través de los límites de los inquilinos y la protección de los datos de un inquilino de otro son requisitos de diseño en lugar de opcionales. Una plataforma que separa la administración limpiamente reduce la fricción, mientras que una que difumina los límites invita al conflicto.
Edificios multi-inquilino
En un edificio multi-inquilino, la plataforma de acceso debe permitir que cada inquilino gestione a su propia gente y sus propias puertas mientras un operador del edificio mantiene el control general. Esto exige separación basada en roles para que los administradores de un inquilino no puedan cambiar el acceso de otro, una pista de auditoría que distinga quién cambió qué y bajo qué autoridad, y reglas claras sobre espacios compartidos como lobbies, vestíbulos de ascensores, baños y áreas de servicio. El ciclo de vida de identidad debe acomodar la rotación de inquilinos, porque los inquilinos entran y salen y la rotación de su personal es suya para gestionar. La revocación a través de los límites de los inquilinos, y la protección de los datos de un inquilino de otro, son requisitos de diseño en lugar de características opcionales. Una plataforma multi-inquilino que separa la administración limpiamente reduce la fricción y la disputa, mientras que una que difumina los límites invita al conflicto y a una postura de seguridad debilitada.
Operación multi-sitio y distribuida
Las organizaciones distribuidas operan muchos sitios desde una plataforma común, y eso cambia el modelo operativo. Algunas plataformas centralizan la administración, permitiendo que el personal regional gestione una cartera completa desde una consola, mientras que otras delegan la administración por sitio con una visión central, y la elección depende de cuánta autonomía necesita cada sitio. Los sitios remotos traen preguntas de conectividad: cómo el servidor de gestión alcanza cada sitio, si los controladores locales mantienen el sitio funcionando cuando cae la WAN, y cómo se sincronizan los eventos fuera de línea una vez que la conectividad regresa. La consistencia es un beneficio real de una plataforma común, porque los formatos de credenciales, las plantillas de políticas y los informes se estandarizan en toda la cartera, pero también significa que un compromiso central afecta a todos los sitios, por lo que la plataforma central y su red de acceso merecen una protección proporcionalmente más fuerte.
Estandarización e informes en toda la cartera
Un sistema de control de acceso comercial en toda la cartera gana su mantenimiento a través de la estandarización y los informes. Los formatos de credenciales estandarizados y las plant
Commercial Access Control Systems Guide — Scope and Definition
A commercial access control system is an integrated electronic platform that decides who may enter a building, a floor, or a room, and records every attempt. It typically combines door locks or electrified hardware, credential readers, controllers that enforce policy, a software management platform, and often integration with video, alarms, visitor management, and building automation. Credentials include cards, key fobs, PINs, mobile wallets, and biometrics, and decisions may be made locally on each door or centrally, with the system holding an audit trail of every access event. A commercial access control system is selected against the site's threat model, its identity and churn patterns, its existing physical and IT infrastructure, and its egress and life-safety obligations, so the deployment plan matters as much as the hardware feature list, and the audit trail it produces becomes one of its most valuable outputs for investigations and compliance.
Treat access control as a policy platform rather than a collection of electronic locks. The same system that admits an employee at a lobby turnstile can protect a server room and trigger an alarm in a lab, and each of those openings carries a different risk that the policy layer must express. This is why the buyer's playbook starts with a door-by-door schedule and a written access policy, not with a product catalog.
What distinguishes a commercial access control system from consumer or small-office hardware
The boundary between residential smart locks and true commercial access control systems is defined by four capabilities rather than by brand or price point. The first is central management: a genuine commercial platform manages many doors, many people, and many schedules from one console, whereas a consumer lock is administered door by door through its own application. The second is an audit trail: commercial systems record who did what, when, and on which opening, in a way that survives power loss and can be exported for investigations. The third is credential breadth and churn handling, covering large and changing populations with instant revocation. The fourth is integration, meaning the ability to link to video, alarms, identity directories, and building automation through open interfaces.
The main categories of deployment
Deployments of commercial access control systems commonly fall into a few categories that shape the whole design. Small and mid-sized sites such as clinics, law firms, or retail head offices may run a single-door-count installation with a modest number of readers and a handful of controllers. Larger single buildings such as corporate towers, hospitals, or universities distribute controllers across floors and wings, often connected over the site LAN and managed centrally. Distributed multi-site organizations, including bank branches, logistics depots, retail chains, or franchise networks, operate many independent sites from one regional or cloud-based management platform. Industrial and high-security sites add hardened readers, tamper detection, segregated networks, and stricter policy such as anti-passback. Each of these shapes pushes a different set of requirements into the architecture, cabling, credential, and lifecycle decisions covered in the rest of this guide.
Commercial Access Control Systems Guide — System Architecture
The architecture of a commercial access control system is described by how readers, controllers, and software are layered. Edge hardware reads credentials and locks or unlocks doors; controllers make decisions, cache policy, and hold open events; and the software platform administers users, schedules, doors, and reports. Decisions about whether to use online controllers at every door, or a hybrid with battery-powered or offline edge locks, drive cost, resilience, and behavior during a network outage. A centralized model gives instant revocation and rich reporting but depends on network availability, while a local model keeps the site working offline at the cost of slower administration. The right architecture matches the number of doors, the physical reach of the cabling, the tolerance for downtime, and the size of the identity population, and it should be documented as a diagram before any hardware is purchased.
Size the controller population and the cable runs from a real door schedule, not an estimate. Every networked door needs a clean power and data path, and the survey that maps those paths early is the difference between a smooth rollout and a construction-phase surprise.
The logical layers: reader, controller, management platform
It helps to think of a commercial access control system as three logical layers even when the physical devices differ. The reader layer is the physical point of interaction where a person presents a card, fob, PIN, biometric, or mobile credential; readers generally do not hold policy, they merely convert a presented credential into an identifier and an event. The controller layer is where the decision is made: it compares the presented credential against a cached or fetched permissions table, checks schedule and anti-passback rules, and drives the lock or relay. The management layer is the software console where an administrator defines users, assigns credentials, builds schedules, maps doors, reviews events, and generates reports. Keeping these layers separate in your mind makes it easier to reason about where a failure occurs and where a security control must live.
Online, offline, and hybrid architectures
Architectures differ mainly in how much intelligence sits at the edge and how dependent decisions are on the network. A fully online architecture keeps every controller continuously connected to the management server, so revocation and policy changes propagate almost instantly and events stream to the console in near real time; its weakness is that a network failure can strand doors if controllers do not cache policy locally. An offline or edge architecture puts credentials and schedule data on each door and removes the constant network dependency, trading instant central revocation for resilience; it is common where cabling is impractical or where doors are battery powered. A hybrid architecture mixes the two, running most doors online and a subset offline, and it is increasingly the default because it balances resilience against the convenience of central management. Whichever you choose, the offline behavior of every controller must be explicitly specified and tested.
Why the architecture diagram matters
The architecture should be captured as a diagram before procurement because it forces decisions that otherwise surface painfully mid-install. The diagram records which doors are online and which are offline, how controllers are grouped, how they reach the server, where network and power protection are installed, and how the management platform is accessed by administrators. It also reveals the single points of failure: a shared network switch serving an entire wing, one controller feeding several high-security doors, or a single cable riser carrying the access backbone. Reviewing the diagram for these dependencies, and deciding in advance how each failure is tolerated, is an architectural act that no product specification can substitute for. Update the diagram as the site changes and keep it with the handover documentation.
Commercial Access Control Systems Guide — Credential and Identity Lifecycle
The identity lifecycle governs how people are enrolled, changed, and removed over the life of a commercial access control system. It covers the types and number of credentials issued, the approval workflow for new access, scheduled or time-limited permissions, badge replacement, instant revocation for terminations, and the audit of who holds what access at any moment. In a building with high turnover — leased offices, contractors, temps, visitors — the volume of enrollments and revocations can exceed the base population several times over, so the administration burden is a first-class selection criterion. Central identity integration with the HR or IT directory keeps access synchronized with hiring and termination events. The goal is that a departed employee's access dies the moment their employment does, without depending on a person to remember to delete it, and without any period in which a former employee still carries working credentials that could be used against the business, since revocation is the moment the system either protects the site or exposes it.
Time-limited and one-time credentials suit visitors and contractors and shrink the stale-identity tail. Define who may grant access and under what approval; the most common security drift comes not from hardware but from unmanaged enrollment and forgotten revocations.
Credential types and how they trade off
Credential choice affects cost, security, convenience, and administration burden. Proximity cards and fobs at 125 kHz are inexpensive and familiar but can be cloned with simple readers, so they are being replaced by 13.56 MHz smart cards that support mutual authentication and encrypted data exchange. Mobile credentials on smartphones add convenience and reduce card issuance cost, but they require users to carry and enroll a phone and the system to manage a mobile credential lifecycle. PIN and keypad credentials are simple and cheap but vulnerable to shoulder-surfing and cannot distinguish one user from another who knows the code. Biometrics such as fingerprints link access to a person rather than to a possession, but they raise enrollment, privacy, and duplicate-enrollment concerns and typically cost more per reader. Most sites combine two or three types, using smart cards or mobile for everyday staff and PIN or one-time codes for visitors.
Enrollment, approval, and deprovisioning
A reliable identity lifecycle depends on defined workflows around four moments. Enrollment is the moment a person is added: someone must verify identity, determine which doors and schedules apply, issue the physical or mobile credential, and record who approved the grant. Change covers moves and role changes, such as an employee relocating to a new floor whose old doors must be removed. Suspension and revocation are the moments that matter most for security, because a terminated or departed employee whose badge still works is a live risk; the process should require no human memory, which is why automatic synchronization with the HR or identity directory is strongly preferred over manual deletion. Finally, periodic recertification reviews the whole population to confirm that everyone's access still matches their current role, and this review is what actually keeps a growing population from quietly accumulating stale credentials.
The administration burden as a selection criterion
It is common to underestimate how much time administering identities consumes. In a churn-heavy building the annual number of badge issues, changes, and revocations can be several times the headcount, and each one takes an administrator's time, needs an approval, and can generate an error. When comparing commercial access control systems, ask directly how long common operations take, how batches of enrollments are handled, whether HR changes flow in automatically, and how revocations propagate to every door, including offline and battery devices. A platform that makes revocation reliable and cheap is worth more than one that is marginally faster at granting access, because granting too much is the drift that erodes security quietly over years.
Commercial Access Control Systems Guide — Security Engineering and Threat Model
Security engineering for a commercial access control system starts from a threat model of what an attacker wants, who is motivated, and how they would try. Typical threats include credential loss or theft, tailgating a legitimate holder through a door, relay attacks on contactless cards, social engineering for a PIN or badge, network intrusion against the management server, and physical tampering with readers or lock cases. Controls span encryption of credentials and communications, anti-passback to stop one credential entering twice, motion and alarm integration, audit logging with alerting, tamper detection, and credentials that can be revoked instantly from a central console. The depth of control is proportionate to what each opening protects; grading doors by the value behind them keeps budget and monitoring where residual risk is genuinely reduced. This guide is educational and does not substitute for qualified security review of the specific site.
State each threat in plain language and rank the protected areas by consequence. Not every opening needs a monitored high-security door, and writing that judgment down explicitly is sound planning rather than a compromise.
Building the threat model
A threat model for commercial access control systems is best built as a table of three columns: the asset an opening protects, the realistic attacker, and the attack path. The asset might be a server room holding customer data, a pharmacy stockroom, a mechanical room, or simply the office floor; the attacker might be a disgruntled former employee, an opportunistic thief, an organized group targeting inventory, or a visitor who wandered into the wrong corridor. The attack paths to consider include using a lost or stolen credential, following a legitimate holder through a door without presenting a credential, replaying or relaying a contactless signal from a distance, guessing or observing a PIN, persuading a staff member to reveal a code or badge, tampering with the reader or lock hardware, and attacking the management server over the network. Writing these down forces the design to respond to real motives rather than to a generic threat list.
Tailgating, relay attacks, and anti-passback
Several threats are specific enough to call out because they shape hardware and policy choices. Tailgating — someone entering behind an authorized holder without presenting a credential — is usually addressed by reader placement, turnstiles or mantrap configurations for high-security areas, video verification, and staff culture rather than by the lock itself. Relay attacks on contactless credentials extend a card's signal from a person's pocket to a faraway reader, so a holder can be unlocked without knowing; modern 13.56 MHz credentials with mutual authentication and encryption resist this, while unencrypted 125 kHz cards generally do not. Anti-passback is a policy control that prevents a single credential from being used to enter twice without an intervening exit, which stops one badge from circulating among several people; it requires reliable exit data and careful design to avoid locking out legitimate users during crowding or configuration errors. Each of these controls must be specified, configured, and tested rather than assumed from the platform's marketing.
Physical tampering and the management server
The physical layer is often the weakest. Readers, lock cases, and controllers are exposed and can be pried, shorted, or bypassed, so tamper switches, sealed enclosures, concealed cabling, and door-position monitoring matter. A door is only as strong as its weakest element, and a surface-mounted reader over a cheap lock with a long throw is a common failure. The management server is a separate and high-value target: if an attacker gains administrative control of the platform they can grant themselves access everywhere, so the server must be patched, segregated on its own network segment, protected by strong and rotated credentials, monitored for intrusion, and backed up so its integrity can be verified after an incident. Threat modeling that treats the server as a crown jewel, and the network as a possible path, is what turns a commercial access control system from a convenience into a credible control.
Commercial Access Control Systems Guide — Integration and Openness
A commercial access control system reaches its full value only when it connects to the rest of the building and the organization. Common integrations include video management and verification on an alarm event, visitor and lobby management, elevator and turnstile control, HR or identity directory, building management systems, and fire or alarm panels. Integration depth is decided before procurement: which events flow to which system, whether the interface is an open API or a proprietary lock-in, who maintains each connection when either system upgrades, and how events are correlated for an accurate audit. Wiegand, OSDP, and RS-485 remain common at the edge, rising to IP and REST or API integration upward, with event-driven messaging where near real-time correlation is needed. Under-integrating forces manual reconciliation of events across systems, while over-integrating licenses features the facility never uses, so the integration scope is a deliberate decision made against the site's real workflows rather than a feature-count exercise.
Confirm ownership of every integration at contract time. The access platform, the elevator controller, and the video server will each upgrade, and the maintenance of their connections is usually the first responsibility to disappear.
Edge protocols: Wiegand, OSDP, RS-485
The physical link between a reader and its controller is where openness begins. Wiegand is a long-established wiring standard that carries a credential identifier over a small number of data wires; it is simple and pervasive, but it is unencrypted and one-directional, which makes it vulnerable to interception and limits the reader's ability to authenticate the controller or receive configuration. OSDP, the Open Supervised Device Protocol, was designed to address these gaps: it provides encrypted, supervised, two-way communication between reader and controller over an RS-485 bus, adds tamper and supervision reporting, and is increasingly the recommended replacement for Wiegand on new commercial access control systems. RS-485 remains the transport of choice for multi-drop wiring to readers and peripherals over moderate distances. Choosing OSDP-capable readers and controllers, and wiring for RS-485 where feasible, buys better security and future flexibility for a modest hardware premium.
Upward integration: APIs, event correlation, and identity
Above the edge, commercial access control systems integrate upward through IP and application interfaces. A well-designed platform exposes an API that lets a visitor system create temporary credentials, lets a video system pull door events for alarm verification, and lets an HR directory push and pull identity changes so that termination automatically revokes access. The value of these integrations depends on event correlation: matching a door alarm to the video camera that covers it, or tying a swipe to the person in the visitor log, is what turns raw events into an investigation-ready record. When comparing platforms, ask what events are exposed, in what format, on what schedule, and with what access control, and test a representative integration in a pilot rather than assuming the advertised connector works. Integration that is designed, documented, and owned beats integration that exists only on a brochure.
Openness versus lock-in
Integration depth forces a strategic decision about openness. Proprietary, closed systems may be simpler to deploy and supported by a single vendor, but they lock the site into that vendor's roadmap, pricing, and upgrade cycle, and they make it harder to connect best-of-breed video, identity, or building automation products later. Open systems that use standard protocols and documented APIs keep procurement options open and make the access platform an asset rather than a hostage, but they place more integration responsibility on the integrator or facility team. The pragmatic path is to demand documented, non-destructive interfaces and a commitment to support them across upgrades, and to write integration ownership into the contract so that when the elevator controller or the video server changes, the connection between them is someone's explicit responsibility. Under-integrating causes manual reconciliation and drift; over-integrating buys features nobody uses — the decision is about what the facility genuinely needs.
Commercial Access Control Systems Guide — Power, Egress, and Life Safety
Power and egress behavior determine what the system does when electricity or network fails. A commercial access control system must define fail-safe doors that unlock on power loss — appropriate for public egress paths — versus fail-secure doors that stay locked for perimeter security, and it must specify battery or uninterruptible-power provision for controllers, readers, and locks so the audit trail and decision-making survive an outage. Local building, fire, and accessibility codes govern free egress, panic hardware, signal-in-door, and delayed-egress features, and those determinations belong to a qualified professional for the specific occupancy and jurisdiction. The system must never let a convenient normal-hours control method override the mandatory free path to safety when power or the network is unavailable. Egress behavior is validated against the facility's actual emergency plan and occupant profile, not a generic assumption.
Choose fail-safe hardware for any opening that cannot tolerate locking people in during an emergency, and test that behavior with the real emergency plan. A door that fails to release under a simulated outage fails the site, however strong the rest of the system.
Fail-safe versus fail-secure
Every electrified opening in a commercial access control system must be classified by its behavior on loss of power. A fail-safe opening unlocks when power is removed, which is appropriate wherever people must be able to leave without delay in an emergency, such as public egress paths, stairwell doors, and exits that lead to safety. A fail-secure opening locks when power is removed, which is appropriate for perimeter and high-security doors where keeping the intruder out matters more than convenience and where an alternative free egress path exists. This is not a default you can leave to the hardware vendor; it is a deliberate, documented decision made per opening against the site's emergency plan and code requirements. Getting it wrong in one direction can lock people in during an emergency, and wrong in the other can leave a perimeter unlocked during a blackout, so the classification belongs in the door schedule and is verified during commissioning.
Power provisioning and uninterruptible supply
Reliable commercial access control systems depend on dependable power to the controllers, readers, locks, and the management server. Controllers should be fed from a protected supply, ideally a dedicated circuit with uninterruptible-power provision sized to ride through the longest expected outage, so that decision-making and the audit trail survive. Battery-powered edge locks trade away cabling for a recurring duty to monitor, schedule, and replace batteries, and their remaining charge and low-battery alerts must be actively managed or doors silently go offline. Readers and electric strikes need adequate, regulated power, and long cable runs must be checked for voltage drop so the hardware operates within specification. Power design is part of the architecture diagram and the commissioning tests, not an afterthought left to whoever installs the doors.
Egress, panic hardware, and delayed egress
Life safety governs how people leave, and commercial access control systems must never obstruct the mandatory free path. Free egress means that occupants can exit without an access credential, a deliberate act, or a delay, which usually translates to fail-safe hardware, request-to-exit and door-position monitoring, and panic hardware such as push bars on public paths. Some jurisdictions permit delayed-egress systems that hold a door for a short audible-alarmed delay before release, but only under defined conditions and after qualified approval, and they are never acceptable where an immediate free path is required. Request-to-exit devices allow doors to open from inside without logging an alarm, but a door that is held open beyond a timeout should alarm so that a propped door cannot be used to tailgate or smuggle. Every egress decision is validated against the facility's actual emergency plan, occupant profile, and local code by a qualified professional, and the system is then tested to prove the door really releases when it must.
Commercial Access Control Systems Guide — Commissioning and Site Rollout
Commissioning and rollout decide whether a sound design becomes a dependable system. A commercial access control system is commissioned by verifying every reader reads and rejects the right credentials, every controller behaves correctly online and offline, every door's fail-safe or fail-secure behavior is confirmed under simulated power and network loss, and the software platform reports the expected events to the right monitors. Tests run on representative doors and repeat after installation, with assumptions recorded and accepted in a formal sign-off by the operator. Handover includes wiring and network diagrams, a credential-administration guide, monitor and alert configurations, and a tested recovery procedure so the site can run without the vendor. Piloting one floor or one functional area before a full rollout surfaces integration and operational problems cheaply, and reveals faults that no test bench would ever expose, before occupants depend on the system daily.
Give the commissioning authority the power to stop the clock on a failed test. A reader that rejects a valid badge, an alarm that does not reach the right monitor, or a door that binds under pressure should fail commissioning rather than fail staff on a Monday.
The commissioning test plan
Commissioning is a formal test plan, not a walkthrough. The plan should cover functional tests, such as presenting valid and invalid credentials and confirming the door opens or stays locked and the event is logged correctly. It should cover performance tests, such as how quickly the door releases and whether the reader responds within the operator's tolerance. It should cover behavior-under-failure tests, confirming each door's fail-safe or fail-secure action when power is cut and how the controller behaves when the network drops, and it should cover integration tests, confirming that an alarm event reaches the right video monitor, that a revocation reaches every door, and that HR termination flows through the identity integration. Each test is recorded with a pass or fail and an owner, and the whole suite is repeated on a representative sample of each hardware type rather than assumed to behave identically across the site.
Handover documentation and operator readiness
Handover is where the vendor stops and the operator starts, and it fails when it is reduced to a set of keys and a verbal briefing. Complete handover documentation for a commercial access control system includes the architecture diagram, wiring and network diagrams, a door schedule with the fail-safe or fail-secure classification and device types, a credential-administration guide, monitor and alert configurations, a spares and maintenance plan, and a tested recovery procedure so the site can operate and troubleshoot without calling the vendor for routine events. Operator readiness means that the people who will manage users, respond to alarms, and handle lockouts have been trained and have practiced the recovery procedure. A site that cannot run its own access system for a day is a site that has not really been handed over, whatever the signed acceptance form says.
Piloting before full rollout
A phased rollout protects the occupants and the budget. Before converting the whole site, run a pilot on one floor, one wing, or one functional area that includes a representative mix of door types, credential types, and integrations, and live with it under real conditions. The pilot surfaces integration faults, operational friction, administrator workload, false alarms, and battery or power issues that never appear on a test bench, and it does so cheaply while only a small population is affected. Measure the pilot against the decision record from the design phase, fix what breaks, and only then scale to the rest of the site. A commercial access control system that has proven itself on a pilot is far more likely to earn the trust of occupants and security staff on day one of the full rollout.
Commercial Access Control Systems Guide — Lifecycle Cost and Supplier Due Diligence
Lifecycle cost for a commercial access control system is the total of hardware, installation, credential administration, maintenance, licensing, software and firmware updates, training, energy, and eventual replacement — not the per-door tag price. Online systems carry cabling, network, server, and licensing overhead; hybrid or battery systems add recurring battery and monitoring burden; and deep integration adds maintenance obligations across the connected platforms. Maintenance ownership must be assigned before purchase: who manages users, updates firmware, replaces readers and batteries, responds to lockouts, and what spares are stocked. Due diligence verifies the supplier's certifications, current model-specific documentation, test evidence, named support path, response time, and warranty terms rather than trusting marketing claims. Requesting those in writing reveals whether the vendor will be a partner across the system's lifetime or simply a seller. Energy draw is small per device but real across a large door count, and it belongs in the model like any other line item.
Ask for per-model certification records and a written spares and end-of-life plan. A controller or reader that becomes unsupported mid-contract becomes a security and maintenance liability the buyer inherits, so confirm the roadmap before committing.
Total cost of ownership beyond the tag price
The per-door price on a quote is the smallest part of the lifetime cost. The largest line items are usually installation, including cabling, network, mounting, and labor; ongoing administration, because every enrollment, change, and revocation takes a skilled person's time; maintenance, firmware updates, and replacements; licensing or software fees that recur annually; and training and energy. Battery-powered devices shift cost from cabling to an endless stream of battery replacement, and the labor of reaching, replacing, and logging those batteries is easy to understate. Deep integration adds maintenance across every connected system, because each upgrade of the video, identity, or building platform can break the integration that was never assigned an owner. Building a ten-year cost model that captures all of these is what separates a defensible budget from a pleasant surprise in year three.
Supplier due diligence
Supplier evaluation deserves the same rigor as the hardware comparison. Request and review certification records, such as conformity to electromagnetic compatibility, safety, and radio standards that are appropriate for the market and the radio technologies used. Ask for current, model-specific documentation rather than generic brochures, and for test evidence that demonstrates the advertised features and security behaviors under realistic conditions. Confirm a named support path, a stated response time, and the terms of the warranty, and ask how firmware updates are delivered and how long each model is supported. A supplier that cannot or will not answer these questions in writing is signalling how it will behave once the purchase is signed. Due diligence is not distrust; it is the buyer establishing that the vendor will be a partner across the system's lifetime rather than simply a seller.
Certification and compliance context
Certifications matter for deployment, insurance, and market access, but they must be read correctly. Conformity marks address safety and electromagnetic compatibility of the hardware itself; they do not by themselves guarantee that an installation meets the building, fire, accessibility, or cybersecurity obligations that apply to a particular occupancy and jurisdiction. Radio-certified readers and credentials are required to operate legally in each market, and the buyer should confirm the specific frequency approvals for the products being purchased. Cybersecurity certification of the platform, if claimed, should be evidenced with documents that describe the scope and the controls assessed. The buyer's own qualified professionals remain responsible for confirming that the system as configured satisfies local codes and regulations; the hardware mark is necessary but never sufficient on its own.
Commercial Access Control Systems Guide — Implementation Checklist
A dependable commercial access control system project follows a repeatable sequence: survey the doors and cabling paths; define the threat model and access policy; design the identity and credential lifecycle; choose the architecture and integration depth; settle power, fail-safe or fail-secure behavior, and life-safety compliance; commission and accept on representative doors; and hand over with training, maintenance ownership, spares, and recovery procedures. Each step closes with a decision record and open items are resolved before the next phase. Pilot the chosen configuration on one floor or functional area before a site-wide rollout, measure against the decision record, and only then scale. This guide is educational and does not substitute for qualified legal, fire, accessibility, cybersecurity, or engineering review, so confirm each requirement with qualified professionals for the exact location and occupancy, and record those confirmations in the decision record alongside every other phase.
The sequence of decisions
A workable implementation sequence keeps the decisions in an order where each one feeds the next. Start by surveying every opening, its function, its power and cable access, and the value it protects, and capture this in a door schedule. From the door schedule, build the threat model and access policy, assigning each opening a classification that drives how much security, monitoring, and control it needs. Design the identity and credential lifecycle next, because the number of people, the churn, and the credential types shape the platform and the administration effort. Only then choose the architecture, the integration depth, the power and fail-safe or fail-secure behavior, and the life-safety compliance, because these depend on the earlier decisions. Finally, plan commissioning, acceptance, handover, and maintenance before the system is installed, so that the site is ready to run the system from day one.
Writing a decision record
A commercial access control system project should be driven by a written decision record, because memory and staff turnover will otherwise undo the design. For each phase, record the decision, the rationale, the alternatives considered, and the open items that remain, and keep it current as the site evolves. The decision record is the reference against which the pilot is measured and the eventual acceptance is judged, and it is the document a new security manager reads to understand why the system behaves the way it does. Without it, a door reclassified in an emergency, a credential type quietly abandoned, or a fail-safe decision reversed on a contractor's suggestion can erode the design with nobody noticing until an incident. The decision record is cheap to maintain and invaluable when something goes wrong.
Confirming with qualified professionals
No planning guide can stand in for the professional reviews that a real installation requires. Qualified legal, fire, accessibility, cybersecurity, and engineering professionals must confirm that the chosen commercial access control system satisfies the requirements of the exact location and occupancy, including local building and fire codes, accessibility obligations, and the facility's own security and data-protection commitments. This is particularly true for egress and life-safety features, delayed egress, panic hardware, and the segregation of the access network. The educational material in this guide is intended to frame the questions and structure the project, not to substitute for that review. Budgeting time and budget for these reviews, and treating their findings as requirements, is what keeps a well-planned system legal and defensible.
Commercial Access Control Systems Guide — Classifying Openings by Security Grade
A practical commercial access control system treats openings differently according to what they protect, rather than applying the same control to every door. Classification assigns each opening a security grade that drives its reader, locking hardware, monitoring, and policy, and it is one of the earliest decisions in the project because everything downstream, from hardware selection to commissioning, depends on it. A lobby entrance that faces the street, a staff-only corridor deep inside a floor, and a server room holding customer records simply do not face the same risk, and applying the same control to each one either wastes budget over-protecting a low-value door or leaves a high-value door inadequately defended. Writing the classification into the door schedule makes the reasoning explicit, reviewable, and consistent with the threat model, concentrating the budget and the monitoring effort where residual risk is genuinely reduced.
Perimeter, interior, and high-security openings
Openings in a commercial access control system fall into broad classes that carry different expectations. Perimeter openings, such as the main entrance, service doors, and loading docks, face the outside world and the greatest exposure, so they usually need robust locking, careful reader placement, video coverage, and strict revocation. Interior openings, such as office, meeting, storage, and staff doors, protect convenience and internal boundaries, and they often balance security against the friction of normal movement. High-security openings, such as server rooms, pharmacies, cash handling, laboratories, and mechanical rooms, protect assets that justify heavier controls, including stronger locks, tamper detection, credential diversity, video verification, anti-passback, and alarm monitoring. Writing a classification for every opening in the door schedule is what makes the rest of the design proportionate rather than uniform.
What drives the grade
Several factors drive an opening's security grade. The value of the asset behind the door is the primary driver, whether that asset is data, inventory, cash, equipment, or the safety of people. The exposure of the opening to unauthorized contact matters, because an exterior door or one in a public corridor sees more attempts than a door deep inside a floor. The consequences of unauthorized entry, including regulatory, financial, safety, and reputational impact, raise the grade. And the legitimate traffic pattern, meaning how often people need to pass and how much friction is acceptable, constrains how strict the controls can be without crippling the operation. Combining these factors produces a small set of grades — for example standard, enhanced, and high security — that map cleanly onto hardware and policy choices.
Turning the classification into requirements
Once openings are graded, the classification translates directly into requirements in the door schedule. A standard-grade opening might use a smart-card reader, a solid commercial lock, and a request-to-exit device with monitoring. An enhanced-grade opening adds video verification, tamper-resistant readers, a door-position monitor with a held-open alarm, and possibly a credential requirement on exit. A high-security opening adds anti-passback, segregated reader wiring, stronger locking, badge-plus-PIN or biometric verification, and integration with alarm monitoring so that a forced entry is escalated immediately. Presenting the classification as a table in the design documents makes the whole system easier to review, to cost, and to accept, and it keeps the monitoring budget where residual risk is genuinely reduced.
Commercial Access Control Systems Guide — Wired Versus Wireless and Battery-Operated Locks
The choice between wired and wireless openings is one of the most consequential decisions in a commercial access control system because it trades cabling cost against power, reliability, and administration burden, and no single answer fits every door. A wired opening keeps continuous power and data flowing to the lock, which enables heavier locking, near real-time events and revocation, and a lower maintenance footprint once installed, but it carries the cost of the cable run itself. A battery-operated wireless opening avoids invasive cabling, which is attractive in leased or historic buildings and for low-traffic interior doors, but it introduces a recurring battery lifecycle and a delay in how quickly policy and revocation reach the door. Understanding these trade-offs per opening, rather than choosing one approach for the whole site, is what produces a sensible and economical hybrid.
When wired openings win
A wired opening keeps power and data flowing to the lock continuously, which buys several advantages. Wired electrified hardware can use heavier-duty locking that draws more current, because power does not have to be conserved for a battery. Wired readers and controllers communicate over the network, so events stream in near real time and policy and revocation updates propagate immediately, which matters for high-security and perimeter openings. Wired openings do not depend on batteries that deplete and must be tracked, so their maintenance is lower once installed, and they are more likely to hold a complete audit trail even through a sustained outage if the controller is on a protected supply. For high-traffic, high-security, or hard-to-reach openings, the higher installation cost of wiring is usually justified by the superior operational characteristics.
When wireless and battery-operated locks make sense
Battery-operated wireless locks become attractive where cabling is impractical or uneconomical. This includes retrofits in historic or leased buildings where running cable is invasive, low-traffic interior doors whose convenience does not justify a cable run, and tenants or multi-tenant floors where the landlord does not want structural work. Battery locks trade away continuous power and instant online behavior for lower installation cost, but they introduce a recurring battery lifecycle: the batteries deplete at different rates per door, low-battery alerts must be monitored, and a door that quietly runs out of charge can go offline or fail to release. Modern wireless locks use low-power radios and scheduled synchronization to keep policy reasonably current, but revocation to a battery door is not instant. They are a good fit for the right openings and a poor fit for high-security or high-traffic ones.
Building the hybrid and planning the battery duty
Most sites end up with a hybrid: wired openings for the perimeter, the high-security areas, and the busy traffic lanes, and battery-operated wireless locks for the low-traffic interior doors where a cable run costs more than it is worth. Planning the hybrid means deciding per opening rather than per product line, and it means designing the battery duty before purchase. That duty includes estimating replacement intervals per door type, defining how low-battery alerts reach the right person, scheduling the replacement rounds, and stocking the right battery type. A wireless opening is only as reliable as the battery program behind it, so a site that chooses battery locks must also choose to own the battery lifecycle. Documenting the wired and wireless mix in the architecture diagram and the door schedule keeps the decision explicit and the maintenance plan realistic.
Commercial Access Control Systems Guide — Controller Sizing and Cabling
Controllers are the decision-making heart of a commercial access control system, and sizing them and their cabling correctly prevents both wasted capacity and embarrassing rework. Each controller supports a limited number of readers and inputs and outputs, so its population is derived from the door schedule rather than guessed, because every door consumes a reader and often a request-to-exit device, a door-position monitor, a locking relay, and sometimes a second reader as well. Wiring reach matters because controllers must sit close enough to their doors for the reader and lock wiring to run reliably, and long runs add cost and voltage drop that can push hardware out of specification. The controller population is then sized with headroom for growth, since adding a door later is trivial with spare capacity but expensive when it means a new controller and a new cable run, so a door schedule laid over a floor plan is the raw material for sizing before any hardware is ordered.
Sizing the controller population
A controller supports a limited number of readers and inputs and outputs, so the controller count is derived from the door schedule rather than guessed. Each door needs a reader, and many need a request-to-exit device, a door-position monitor, a locking relay, and sometimes a second reader for a mantrap or a card-on-exit configuration, and all of these consume inputs and outputs on the controller. Wiring reach matters because controllers must be physically close enough to their doors for the reader and lock wiring to run reliably, and because long runs add cost and voltage drop. The controller population is then sized with headroom for growth, because adding a door later is trivial if the controller has spare capacity and expensive if it means installing a new controller and a new cable run. A door schedule laid over a floor plan is the raw material for this sizing, and it should be done before any hardware is ordered.
Cabling for power, data, and readers
Cabling carries three distinct responsibilities that are easy to conflate. Power cabling feeds the locks, strikes, and readers, and it must be sized for the current draw of the devices and checked for voltage drop over the run length. Data cabling carries the network back to the controllers and the management server, and it must reach the places where controllers are installed and where the network is available. Reader cabling connects each reader to its controller, and on OSDP installations it is an RS-485 bus that also carries supervision and encryption. Cabling that is run once and hidden is expensive to rework, so the survey should map the actual paths, identify the risers and access points, and flag openings where a clean power and data path is missing. Getting the cabling right in the planning phase is what turns a smooth rollout into a routine job rather than a construction-phase surprise.
Controllers offline and the resilience question
Because controllers hold the local decisions, their resilience during a network outage determines how the site behaves when the LAN fails. A controller with local policy cache continues to enforce schedules and permit or deny credentials even when it cannot reach the management server, which keeps the site working through an outage; a controller with no cache may stop deciding entirely and fail open or closed depending on configuration. The offline policy — how long stale credentials remain valid, whether offline events are buffered and uploaded later, and whether the door fails safe or secure — must be specified and tested for every controller. Designers should also consider redundant power to controllers and, where the risk justifies it, redundant network paths so that a single switch or cable failure does not disable a whole wing. The resilience of the controller layer is the resilience of the commercial access control system as a whole.
Commercial Access Control Systems Guide — The Management Server and IT Cybersecurity
The management server concentrates the value of a commercial access control system into a single high-value target, so its security and the security of the access network deserve the same attention as the doors themselves. A compromise of the server is a compromise of every door it manages, because administrative control over the platform grants access to the whole site, so the server, its operating system, and its database are treated as crown jewels. That means placing the access network on its own segregated segment with controlled connectivity to the corporate LAN, so that an infection that starts elsewhere cannot reach the controllers or the management console without crossing a monitored boundary. It means strong, unique, rotated administrative credentials with multi-factor authentication and least-privilege roles, patching on a defined schedule, and backups that are tested by actually restoring them. Monitoring administrative activity and alerting on failed logins and unexpected configuration changes turns the platform into a defended asset rather than an open console.
Segregating the access network
The access control network should be treated as a sensitive segment rather than just another part of the office LAN. Credential data, audit logs, and administrative credentials are valuable, and the readers and controllers are physical devices that can be probed, so the access network is often placed on its own VLAN or network segment with firewalled, restricted connectivity to the corporate network. A compromise that starts on an infected workstation should not be able to reach the access controllers or the management server without crossing a controlled boundary. This segregation also limits the blast radius of a misconfigured device and makes monitoring the access segment more meaningful. The decision to segregate, and the rules that govern the boundary, belong in the architecture diagram and the cybersecurity review, not in an afterthought.
Securing the management platform
The management platform is where administrators change access, so its authentication and access control are critical. Administrative accounts should use strong, unique, rotated credentials, with multi-factor authentication wherever the platform supports it, and least-privilege roles that separate who can grant access from who merely views events. The platform and its operating system must be patched on a defined schedule, with firmware updates applied to controllers and readers as they are released and tested. Backups of the access database and configuration must be taken regularly, stored securely, and tested by actually restoring them, because a platform that cannot be recovered is a platform that cannot be trusted after an incident. Monitoring administrative activity, and alerting on failed logins and unexpected configuration changes, turns the management platform into a defended asset rather than an open console.
Data protection and audit integrity
A commercial access control system holds personal data about who entered where and when, which carries privacy obligations as well as security ones. Access records should be retained according to a documented policy, protected at rest and in transit, and accessible only to those with a legitimate need, and the platform should record changes to its own configuration so that an investigator can trust the audit trail. The integrity of the audit log matters because its whole purpose is to be believed later; logs that can be silently edited, or whose server can be tampered with unnoticed, are of little evidential value. Segregation, patching, strong administration, and log protection together are what keep the management server and the data it holds defensible, and they are as much a part of the design as the readers and locks at the doors.
Commercial Access Control Systems Guide — Multi-Tenant and Multi-Site Operation
Commercial access control systems are often expected to serve more than one organization, and more than one building, from a single platform, and that multi-tenant and multi-site responsibility adds a layer of administration and security that single-building deployments do not face. In a multi-tenant building the platform must let each tenant manage its own people and its own doors while a building operator holds overall control, which calls for role-based separation so that one tenant's administrators cannot change another tenant's access, an audit trail that attributes changes to the right administrator, and clear rules about shared spaces such as lobbies, lift lobbies, toilets, and service areas. The identity lifecycle must also absorb tenant churn, because tenants move in and out and their staff turnover is theirs to manage, while revocation across tenancy boundaries and the protection of one tenant's data from another are design requirements rather than optional. A platform that separates administration cleanly reduces friction, while one that blurs boundaries invites conflict.
Multi-tenant buildings
In a multi-tenant building, the access platform must let each tenant manage its own people and its own doors while a building operator holds overall control. This calls for role-based separation so that one tenant's administrators cannot change another tenant's access, an audit trail that distinguishes who changed what and under whose authority, and clear rules about shared spaces such as lobbies, lift lobbies, toilets, and service areas. The identity lifecycle must accommodate tenant churn, because tenants move in and out and their staff turnover is their own to manage. Revocation across tenancy boundaries, and the protection of one tenant's data from another, are design requirements rather than optional features. A multi-tenant platform that separates administration cleanly reduces friction and dispute, while one that blurs boundaries invites conflict and a weakened security posture.
Multi-site and distributed operation
Distributed organizations operate many sites from a common platform, and that changes the operational model. Some platforms centralize administration, letting regional staff manage a whole portfolio from one console, while others delegate administration per site with a central overview, and the choice depends on how much autonomy each site needs. Remote sites bring connectivity questions: how the management server reaches each site, whether local controllers keep the site working when the WAN drops, and how offline events are synchronized once connectivity returns. Consistency is a real benefit of a common platform, because credential formats, policy templates, and reporting are standardized across the portfolio, but it also means that a central compromise affects every site, so the central platform and its access network deserve proportionally stronger protection.
Standardization and reporting across the portfolio
A portfolio-wide commercial access control system earns its keep through standardization and reporting. Standard credential formats and policy templates let a new site come online quickly and consistently, and let a person move between sites without a new credential type. Portfolio reporting gives security leadership a view of access across all sites, highlighting anomalous behavior, under-used doors, stale credentials, and sites that need attention, and it makes the whole portfolio auditable in a way that scattered per-site systems cannot match. The cost is that standardization is a commitment: once the platform, credential, and policy templates are set, changing them is a portfolio-wide project, so the initial design decisions deserve care. For a distributed organization, the reporting and consistency that a common platform provides often justify the central management and connectivity investment.
Commercial Access Control Systems Guide — Integration with HR, Video, and Visitor Management
The deepest value of a commercial access control system emerges through its connections to the systems that surround it, and identity, video, and visitor management are the three integrations that most affect everyday security. Linking the access platform to the HR or identity directory keeps access accurate by flowing hiring and termination events automatically, so a departing employee is revoked the moment their employment ends rather than when someone remembers to delete them, and this integration is the single most powerful control in a churn-heavy site. Video is the natural companion because it answers the question the audit trail cannot, by correlating an alarm event with the right camera so the operator verifies what actually happened rather than merely receiving a notification. Visitor management turns ad-hoc badge issuance into a controlled workflow by issuing time-limited credentials that expire automatically, are scoped to the areas the visitor needs, and log who they visited and when, shrinking the stale-credential tail that general badges create.
Identity directory and HR integration
Linking the access platform to the HR or identity directory is the single most powerful integration for keeping access accurate. When hiring and termination events in the HR system flow automatically into the access platform, a new employee is provisioned at enrollment and a departing employee is revoked the moment their employment ends, without relying on a person to remember. This integration must handle the identity matching between the directory record and the access record, the scope of what flows in each direction, and the failure mode when the directory is unreachable, so that a directory outage cannot silently leave stale access in place. Role-based mapping, where an employee's role and department determine which doors they get, makes the integration sustainable as people change roles. An identity integration that is designed, tested, and monitored is what keeps a growing population's access accurate over time.
Video verification
Video is the natural companion to a commercial access control system because it answers the question the audit trail cannot: what actually happened at the door. On an alarm event such as a held-open door, a forced entry, or a failed authentication, the platform should correlate the event with the relevant camera and present the operator with video for verification, turning an alarm from a notification into an actionable observation. This correlation depends on mapping each door to its camera coverage, and on the two systems agreeing on time so that events line up for investigation. Video integration is also valuable for tailgating review and for identifying the person behind a credential in dispute. The value of the integration is in the correlation and the workflow it supports, so it should be specified around the operator's actual verification process rather than around a generic connector.
Visitor and lobby management
Visitor management turns ad-hoc credential issuance into a controlled workflow. Instead of handing out a general-purpose badge and hoping it is returned, a visitor system issues a time-limited credential that expires automatically, escorts or geofences the visitor to the areas they need, and logs who they visited and when. Integration with the access platform means the visitor's temporary access is created, enforced, and revoked by the system, shrinking the stale-credential tail that general badges create. It also means the visitor record is correlated with door events, so an investigation can trace a visitor's movements accurately. The design questions are who approves a visitor, how far the temporary access extends, and how the system handles a visitor who stays beyond their allotted time. A visitor integration that is governed by policy, rather than by whoever is at the front desk, keeps the front door and the interior consistent.
Commercial Access Control Systems Guide — Maintenance, Recovery, and Contingency
A commercial access control system is a long-lived asset, and its behavior years after installation depends on how it is maintained and how it recovers from failure, so maintenance and recovery are planned during the design rather than discovered after an incident. A sustainable platform has a written maintenance plan that assigns every recurring duty an owner: user and credential administration including enrollments, changes, revocations, and population recertification; firmware and software updates for the platform, controllers, and readers, including who tests and applies them; hardware such as readers, locks, batteries, and power supplies, and the spares stocking level that keeps common failures repairable; and the integrations, because each connected system's upgrade can break a connection that needs a named owner. Every site also needs a tested recovery procedure covering server failure, network loss, controller failure, and exhausted batteries, with fail-safe or fail-secure behavior confirmed under a simulated outage. When duties have owners and recovery is rehearsed, the system drifts less and an incident exposes far fewer gaps.
The maintenance plan
A sustainable commercial access control system has a written maintenance plan that assigns every recurring duty an owner. That plan covers user and credential administration, including who manages enrollments, changes, revocations, and the periodic recertification of the population. It covers firmware and software updates for the platform, controllers, and readers, including who tests and applies them and on what schedule. It covers hardware, including readers, locks, strikes, batteries, power supplies, and spare devices, and the stocking level that keeps common failures repairable quickly. And it covers the integrations, because each connected system's upgrade can break a connection that needs an owner. When every duty has an owner and a schedule, the platform drifts less and fails less; when duties are unassigned, the system degrades silently until an incident exposes the gaps.
Recovery and the outage playbook
Every site needs a tested recovery procedure so that it can run without the vendor. The outage playbook defines what happens when the management server fails, when the network is lost, when a controller fails, when a reader is dead, and when batteries run out, including who is notified, how doors are kept safe and egress preserved, and how the system is restored. Critically, the recovery procedure is practiced: a backup that has never been restored, or an outage scenario that has never been walked through, is a bet that the site will improvise correctly under stress. Testing the fail-safe or fail-secure behavior during a simulated outage is part of this, because it confirms the door really releases when it must. A site that has rehearsed its recovery is a site that can keep its people safe and its operation running when something goes wrong.
Contingency and spares
Contingency planning ensures the site can survive the loss of individual components. Spare readers, locks, controllers, power supplies, and batteries should be stocked at a level matched to the failure rate and the delivery time, so that a common failure is repaired in hours rather than days. The spares plan should name the specific models and quantities, the reorder point, and who is responsible for keeping the stock current as hardware is retired. End-of-life planning matters because a controller or reader that becomes unsupported mid-contract is a security and maintenance liability that the buyer inherits; knowing the supplier's roadmap and the planned replacement in advance avoids an emergency migration. Contingency is the difference between a commercial access control system that recovers gracefully and one that leaves the site exposed while a replacement is sourced.
Commercial Access Control Systems Guide — Comparison Table and Worked Example
Bringing the decision together, a comparison table and a worked example translate the many choices in a commercial access control system into something concrete that a buyer can review and cost, because the value of the earlier reasoning is realized only when it is consolidated into a form that can be scored against the site's priorities. A comparison table rows the major decisions — architecture, lock power, reader credential, edge protocol, egress behavior, identity source, and management approach — against representative options and the factor that drives the choice, making the trade-offs visible at a glance rather than buried in prose. The table is a starting framework, not a substitute for a site-specific design, because each choice trades one property against another and only the decision record explains why a particular combination fits a particular site. The worked example then applies that framework to a concrete building, showing how the earlier decisions compound into an economical, secure, and operable installation, commissioned and accepted with confidence.
Commercial access control systems at a glance
| Decision | Option A | Option B | Option C | What drives the choice |
|---|---|---|---|---|
| Architecture | Fully online | Offline / edge | Hybrid | Network resilience vs. instant central control |
| Lock power | Wired electrified | Battery wireless | Hybrid mix | Cabling cost vs. high-security and traffic needs |
| Reader credential | 13.56 MHz smart card | Mobile credential | PIN or biometric | Convenience, cost, and security per opening grade |
| Edge protocol | Wiegand | OSDP over RS-485 | Vendor-proprietary | Security, supervision, and future openness |
| Egress behavior | Fail-safe | Fail-secure | Per-opening mix | Emergency plan and code requirements |
| Identity source | Manual enrollment | HR directory integration | Role-based mapping | Churn volume and accuracy of access |
| Management | On-premise server | Segregated network segment | Cloud-based multi-site | IT resources, data protection, and portfolio size |
The table is a starting framework, not a substitute for a site-specific design; each column's choice trades one property against another, and the decision record explains why a particular combination fits a particular site.
A worked example: a mid-sized office building
Consider a mid-sized office building with a lobby, four floors, a server room, and roughly two hundred employees with significant staff turnover. The door schedule classifies the main entrance and the server room as high security, the stairwell and egress doors as life-safety openings that must fail safe, and the interior floor doors as standard. The architecture is hybrid: the perimeter and the server room are wired and online for instant revocation and video verification, while the lower-traffic interior floor doors are battery-operated wireless locks to avoid invasive cabling in a leased space. Credentials are 13.56 MHz smart cards for staff, with mobile credentials offered as an option, and a visitor system issues time-limited credentials at the lobby. The HR directory feeds terminations into the platform automatically so a departure revokes access immediately, and the management server sits on a segregated network segment with multi-factor-protected administration and tested backups.
Reviewing the worked example
The worked example shows how the earlier decisions compound. Because churn is high, the HR integration is the single most important control for keeping access accurate, and the buyer invests there rather than in over-credentialing every door. Because the space is leased and cabling is invasive, the hybrid architecture saves significant installation cost, accepting the battery lifecycle on interior doors as a deliberate trade. Because the server room and entrance matter most, the monitoring and the video verification concentrate where residual risk is genuinely reduced, while the interior doors carry lighter policy. The commissioning plan pilots one floor, tests the fail-safe behavior on the stairwell and egress doors under a simulated outage, and validates that a revocation reaches every door including the battery-operated ones before full rollout. The decision record captures all of this, so the system can be operated, maintained, and accepted with confidence.
Commercial Access Control Systems Guide — FAQ and Common Mistakes
A few recurring questions and common mistakes capture the practical lessons of planning a commercial access control system, and reviewing them before committing to a design saves both money and regret. The questions that recur most often concern the difference between fail-safe and fail-secure behavior, where an opening that unlocks on power loss suits egress paths while one that stays locked suits perimeter security; whether a single platform can manage several buildings, which it can for distributed organizations; how secure battery-operated locks are, which depends on trading continuous power and instant online behavior for a lower installation cost; and how quickly a lost credential can be revoked, which is effectively instant with online controllers but depends on the next synchronization for offline devices. Beneath those questions sit the mistakes that recur across otherwise sound projects, and understanding both the questions and the mistakes is what keeps a planning effort grounded in the realities of operation and cost.
Frequently asked questions
What is the difference between fail-safe and fail-secure? A fail-safe opening unlocks on power loss, which suits public egress paths, while a fail-secure opening locks on power loss, which suits perimeter security; each is chosen per opening against the emergency plan and code requirements. Can one system manage several buildings? Yes, distributed commercial access control systems manage many sites from a common platform, with per-site and central administration depending on how much autonomy each site needs. Are battery-operated locks as secure as wired ones? Battery locks trade continuous power and instant online behavior for lower installation cost, so they are a fit for low-traffic interior doors but not for high-security or high-traffic openings. How quickly can a lost credential be revoked? With a central platform and online controllers, revocation is effectively instant; offline and battery devices depend on their next synchronization, so the revocation latency of every device type should be confirmed in advance.
Common mistakes
Several recurring mistakes undermine otherwise sound projects. The first is choosing hardware before building the door schedule and the threat model, which locks in a design that does not fit the site. The second is treating the per-door price as the cost of the system, ignoring the cabling, administration, licensing, maintenance, batteries, and training that dominate the lifetime total. The third is skipping the segregation and hardening of the management server and access network, leaving the crown jewel of the system exposed to the same attacks as the office LAN. The fourth is assuming revocation and egress behavior work as advertised, when a credential that is not actually revoked on a battery door, or a fail-safe door that binds under pressure, only surfaces during a test or an incident. The fifth is starting the rollout site-wide without a pilot, discovering integration and operational problems after occupants depend on the system daily.
How to avoid them
Avoiding these mistakes comes down to process rather than to a particular product. Build the door schedule and the threat model before comparing hardware, and grade openings by what they protect. Build a ten-year cost model that captures installation, administration, licensing, maintenance, batteries, and training, and use it rather than the tag price. Segregate the access network, harden the management platform, and test backups by restoring them. Specify and test revocation latency and egress behavior per device type, and confirm fail-safe or fail-secure action under a simulated outage. Pilot one floor or one functional area, measure against the decision record, and scale only after the pilot holds up. A commercial access control system that follows this sequence is far more likely to be secure, reliable, and affordable across the years it will serve the site.
Part of this article content is generated by AI and optimized for professional accuracy and readability.
¿No sabe qué sensor se adapta a su proyecto?
Hable con nuestros ingenieros de aplicación mmWave para una consulta gratuita.
Especifica tu proyecto hotelero con nuestros ingenieros
Envíanos el número de habitaciones, tipo de techo y preferencia de protocolo. Devolveremos un plan de muestra y cotización en 24 horas laborables.
- Pase de la guía general a una discusión de producto o aplicación.
- Use RFQ cuando precio, planos, MOQ o calendario de lanzamiento necesiten estructura.
- Mantenga visible una ruta de contacto directo para aclaraciones rápidas y traspasos.